Surreal Paradigms - Automotive Culture Crash
Exploring cultural clashes between media, hacker, and corporate worlds, this talk examines open source, legality, and the need to break down barriers for a more collaborative future.
Reality Checking Your AppSec Program
Explore strategies to critically assess and improve your AppSec program, focusing on compliance, maturity, education, and validation beyond traditional metrics and assumptions.
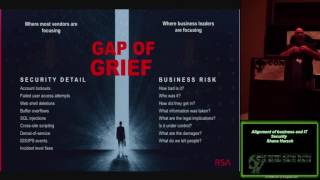
Alignment of Business and IT Security
Explore strategies for aligning business and IT security in the evolving threat landscape. Learn about visibility, analytics, and operational roles for effective threat detection and response.
Money Fame Power Build Your Success as a Security Professional
Build success in cybersecurity through business acumen, networking, and personal growth. Learn from mistakes, think creatively, and develop interpersonal skills to excel in the field.
So You've Inherited a Security Department - Now What
Learn essential strategies for managing an inherited security department, covering OSINT tools, best practices, and key areas like compliance, user education, and vulnerability scanning.
On Being an Eeyore in Infosec
Explore the challenges and pessimistic perspectives in information security, offering insights on navigating the field's complexities and maintaining resilience despite setbacks.
Attacking the Hospitality and Gaming Industries - Tracking an Attacker Around the World in 7 Years
Explore a 7-year global investigation tracking cyber attacks on hospitality and gaming industries, uncovering tactics and strategies used by sophisticated threat actors.
So You've Inherited a Security Department - Now What
Practical strategies for new security department leaders: asset management, information gathering, vulnerability assessment, and team building for effective cybersecurity operations.
Bitcoin From Zero to I Get It
Comprehensive introduction to Bitcoin: its origins, technology, and real-world applications. Gain a solid understanding of cryptocurrency fundamentals and blockchain principles.
Getting Permission to Break Things
Learn ethical hacking techniques, navigate legal issues, and gain stakeholder buy-in for security testing. Discover how to define scope, address client needs, and handle potential pitfalls in penetration testing.
Information Security and the Law
Explore legal aspects of information security, including compliance, regulations, and legal frameworks affecting cybersecurity practices and policies.
Red Teaming Your Risk Management Framework
Explore red teaming techniques to enhance your risk management framework, improving organizational security and resilience against potential threats and vulnerabilities.
HIPAA for Infosec Professionals
Comprehensive overview of HIPAA regulations for information security professionals, covering key concepts, compliance requirements, and best practices in healthcare data protection.
Protecting Third Party Risk From Plundering
Learn strategies to safeguard against third-party risks and protect your organization from potential security breaches and data plundering.
Hacking the Sabbath
Explore the intersection of technology and religious observance, examining innovative solutions for maintaining Sabbath traditions in the modern digital age.
So You Want to Be a Cyber Threat Analyst Eh
Learn about cybernetics, threat analysis, and defense strategies. Explore certifications, tools, and business models while gaining insights into risk assessment and mitigation techniques.
Information Security Assurance
Learn about advanced persistent threats, cybercrime, cyber espionage, and SCADA systems in hospitals. Explore information security assurance and attribution in this comprehensive overview of modern cybersecurity challenges.
Building a Scalable Vulnerability Management Program for Effective Risk Management
Learn to build and maintain a scalable vulnerability management program, covering asset prioritization, scanning, remediation, reporting, and continuous improvement for effective risk management.
The Upside Down - Going from NetSec to AppSec
Explore the transition from network security to application security, covering challenges, pipeline analysis, and solutions for effective cybersecurity practices.
Predictive Analytics and Machine Learning - Real Use Cases for IT Security Professional
Explore real-world applications of predictive analytics and machine learning in IT security, covering data mining, modeling techniques, and practical implementation strategies.
Does DoD Level Security Work in the Real World - Jeff Man
Explore DoD-level security's real-world effectiveness, risk assessment, and building a culture of security. Learn about the security lifecycle and components of information security.