Overview and Analysis of NIST Cybersecurity Framework
Comprehensive analysis of the NIST Cybersecurity Framework, exploring its key components, implementation strategies, and practical applications for enhancing organizational security posture.
Building a Successful Insider Threat Program
Comprehensive guide to establishing an effective insider threat program, covering monitoring, strategy, documentation, and implementation for enhanced organizational security.
Emerging Trends in Identity Access Management
Explore emerging trends in identity access management, covering consumer identity, social media integration, corporate strategies, and device identity.
Rebuilding and Transforming an Information Security Function
Explore strategies for rebuilding and transforming information security functions, covering regulatory perspectives, strategic planning, and key principles for effective implementation.
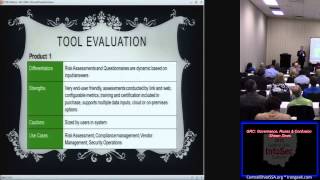
GRC Governance Ruses Confusion
Explore effective GRC governance strategies, avoiding common pitfalls and focusing on practical, business-aligned approaches for successful implementation and evaluation.
Panel Discussion - Insourcing, Outsourcing and Hybrid
Explore the pros and cons of insourcing, outsourcing, and hybrid models in information security through expert insights and real-world experiences.
Pondering the False Economy of Secrets
Explore information security through aviation analogies, discussing layers of protection, the cost of failure, and the importance of checklists in both fields.
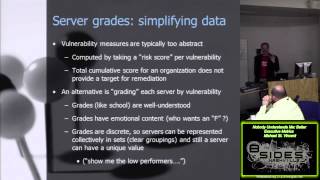
Nobody Understands Me Better - Executive Metrics
Explore effective metrics for communicating security insights to executives. Learn to present data visually, focus on business impact, and tell compelling stories that drive action and support.
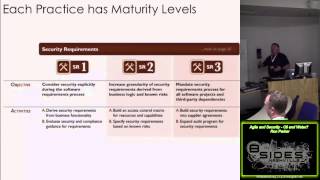
Agile and Security - Oil and Water
Explore the integration of Agile methodologies and security practices, addressing challenges and proposing solutions for effective implementation in software development.
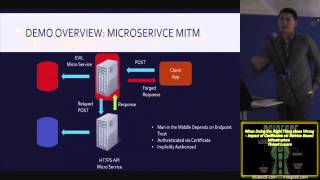
When Doing the Right Thing Goes Wrong - Impact of Certificates on Service Based Infrastructure
Explore the impact of certificates on service-based infrastructure, covering trust chains, implicit trust, and potential risks. Learn about certificate authorities and strategies for secure implementation.
Corporate Governance for Fun and Nonprofit
Explore non-profit governance essentials, including roles, responsibilities, and legal duties of officers and board members. Learn to navigate corporate structures effectively.
Examining Hacktivism - Crime and Punishment in the Digital Age
Explore hacktivism's evolution, legal implications, and societal impact through case studies, demographic analysis, and sentencing patterns in the digital age.
Overview of Darknets
Explore darknets, including Tor, Freenet, and I2P, covering installation, operation modes, pros/cons, and security considerations for anonymous online communication.
Is Threat Modeling for Me
Explore threat modeling essentials, including data flow diagrams, STRIDE methodology, and addressing threats. Learn to identify and mitigate security risks in your systems effectively.
Hacker or Criminal - Repairing the Reputation of the Infosec Community
Explore strategies to improve the public perception of information security professionals and bridge the gap between hackers and the general public.
Maturing Information Security When Compliance Doesn't Cut It
Explore strategies for maturing information security beyond compliance, focusing on business alignment, social engineering, access control, and building a robust security awareness program.
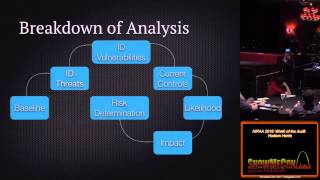
HIPAA 2015 - Wrath of the Audit
Explore HIPAA compliance challenges and audit strategies in healthcare, focusing on data protection, risk management, and regulatory requirements.
Actionable Threat Intelligence - ISIS and the SuperBall
Explore actionable threat intelligence strategies, from building threat models to implementing preemptive and reactive measures, enhancing cybersecurity through practical insights and methodologies.
Digital Supply Chain Security - The Exposed Flank
Explore digital supply chain vulnerabilities, legal complexities, and security strategies. Learn to identify risks, implement robust processes, and go beyond compliance for effective protection.
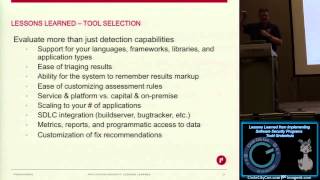
Lessons Learned from Implementing Software Security Programs
Insights on implementing software security programs, covering challenges, training, threat modeling, design reviews, testing, vendor management, and metrics for effective cybersecurity strategies.
Running Away from Security - Web App Vulnerabilities and OSINT Collide
Explore the intersection of web app vulnerabilities and OSINT techniques, uncovering potential security risks and learning effective mitigation strategies.