Planning Effective Red Team Exercises
Learn best practices for planning and executing effective red team exercises, including scenario design, objective setting, and rules of engagement to simulate real adversaries and provide maximum value to clients.
Mobile App Corporate Espionage
Explore real-world corporate espionage techniques using hidden behaviors in mobile apps, focusing on data risk threats and out-of-band communications for leaking sensitive information.
Emerging Best Practices in Software Supply Chain Security - What We Can Learn from Google, the White House, OWASP, and Gartner
Explore emerging best practices in software supply chain security, analyzing guidelines from major organizations to compile key strategies for mitigating risks in deployment pipelines.
Three’s Company - Unpacking and Settling in with Three NIST Frameworks
Explore how NIST's Risk Management, Cybersecurity, and Privacy Frameworks complement each other to enhance enterprise risk management and improve organizational security posture.
DBOM and SBOM - New Options for Better Supply Chain Cybersecurity
Explore new approaches to supply chain cybersecurity using Digital and Software Bill of Materials. Learn how these tools can enhance risk management and component traceability in complex global supply chains.
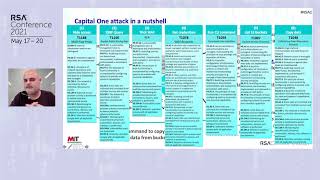
A Case Study of the Capital One Data Breach
Explore the 2019 Capital One data breach, examining attack methods, compliance issues, and corporate culture's impact on cybersecurity posture.
Supply Chain Security in the Software Era
Explore software supply chain risks and gain insights on mitigating them through real-world examples and concrete recommendations for policy makers and executives.
InfoSec is a Board Responsibility
Elevate InfoSec to a governance issue by speaking 'board talk', addressing objections, and tailoring proposals to focus on measurable benefits, risk mitigation, and corporate objectives.
Hacker TikTok - Community, Creativity, and Controversy
Panel discussion exploring security-focused TikTok creators' experiences in bringing hacking awareness, humor, and community to a new audience, highlighting successes and challenges in this emerging frontier.
CISO Panel Discussion
Insightful discussion on building and scaling top security teams, exploring strategies for talent attraction, retention, and overcoming challenges in the cybersecurity industry.
An Unlikely Friendship - Why Security Engineers and Product Managers Should Be Working Together
Discover strategies for security engineers to collaborate with product managers, enhancing security features, accelerating team growth, and unlocking revenue from security-conscious customers.
Embracing Risk Responsibly - Moving Beyond Inflexible SLAs and Exception Hell by Treating Security Vulnerabilities and Risk Like Actual Debt
Discover how to treat security vulnerabilities as debt, moving beyond rigid SLAs and exception overload. Learn strategies for responsible risk management in cybersecurity.
The Metrics Manifesto
Discover predictive analytics for security, including decision science, Bayesian methods, and quantitative risk management. Learn to measure attack surface and present advanced metrics to boards.
Retain and Recruit a Diverse Talent Pool
Strategies for building and maintaining a diverse cybersecurity workforce, addressing talent shortages through inclusive practices and innovative retention approaches.
How to Find the Money - Interviews with Leading Venture Capitalists
Venture capitalists share insights on securing funding for startups, from stealth to exit, and navigating the competitive marketplace in this informative seminar.
How to Get the CISO's Attention
Insights from industry leaders on effectively engaging CISOs, exploring strategies for startups to stand out in cybersecurity and gain executive attention.
Change Your Approach to Get It Right
Insights from IBM Security leaders on transforming cybersecurity culture and approaches. Learn innovative strategies to empower organizations and unite the industry for exponential improvement.

Strategic Competition - The Rise of Persistent Presence and Innovation
Explore how NSA and USCYBERCOM defend against sophisticated cyber threats using countermeasures and a whole-of-nation approach to protect national security and economic interests.
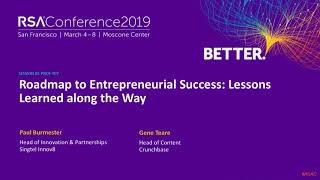
Roadmap to Entrepreneurial Success - Lessons Learned along the Way
Insider insights on startup success across global markets. Learn key patterns, avoid common pitfalls, and discover strategies for differentiating your innovative ideas and finding valuable mentorship.
The Trust Landscape
Exploring the impact of digital connectivity on trust in institutions and information, with strategies to redefine risk and restore faith in a hyperconnected world.

Lightning in a Bottle, or Burning Down the House?
Exploring the dual nature of AI in cybersecurity: its potential to strengthen defenses and amplify attacks. Discusses strategies for responsible innovation and delegation of AI across organizations.