Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Securing the Build and Deployment Pipeline - Challenges and Best Practices
Explore challenges in securing build/deployment environments for agile development and DevOps. Learn about potential vulnerabilities in automated processes and strategies to maintain code integrity.
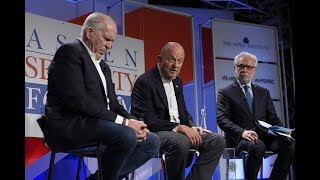
Under Assault: Assessing Top Threats to US National Security
Former CIA and National Intelligence directors discuss current external and internal threats to US national security, offering expert insights on pressing global challenges.
Security Metrics: Protecting Our Digital Assets of the Future
Explore security metrics' evolution and importance in protecting digital assets, focusing on people, processes, and technology. Learn to establish effective frameworks for measuring cybersecurity program success.
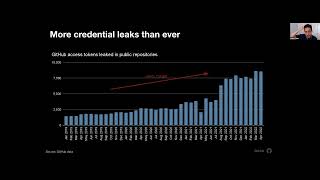
Flipping the Script on Application Security
Explore innovative approaches to application security, challenging traditional methods and introducing fresh perspectives for more effective protection strategies.
Software Supply Chain Security
Explore software supply chain security with expert Vandana Verma, covering key concepts, best practices, and strategies to protect your development pipeline from vulnerabilities and attacks.
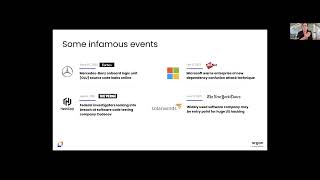
Benchmarking the Security of Your Software Supply Chain
Learn to assess and enhance the security of your software supply chain through benchmarking techniques, improving overall cybersecurity posture and reducing vulnerabilities.
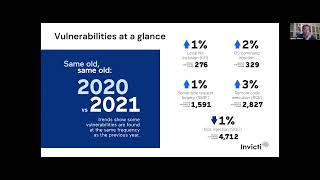
Worrisome Web Vulnerability Trends in the Race to Innovation
Explore concerning web vulnerability trends amid rapid innovation, examining their impact on security and discussing strategies for mitigation and protection.
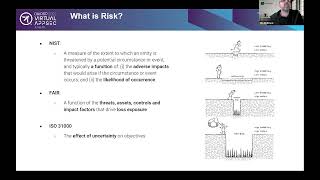
A Risk-Based Approach to API Security
Explore a risk-based approach to API security, focusing on threat modeling, vulnerability assessment, and mitigation strategies to enhance your organization's API protection.
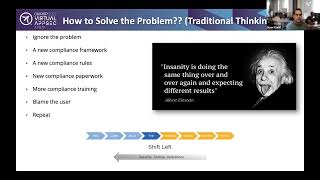
Mitigate Risks in Code - Protect Your Software-based Supply Chain
Explore strategies to mitigate risks in code and safeguard your software-based supply chain, enhancing overall security and resilience in software development.
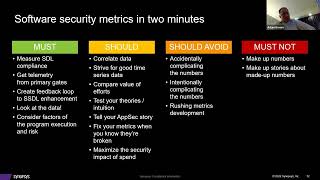
Over a Decade of Software Security - What Have We Learned
Explore key insights and lessons from a decade of software security evolution, highlighting crucial developments and best practices for modern cybersecurity professionals.
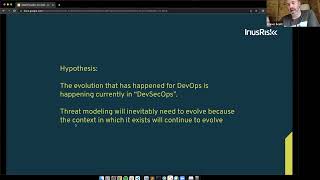
Evolving Threat Modeling Through the Open Threat Model Format
Explore the Open Threat Model Format and its role in advancing threat modeling practices for improved cybersecurity risk assessment and mitigation strategies.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Supply Chain Security with Dependency Track
Explore supply chain security using Dependency Track with experts Anandan, Bhargava, and Duster. Learn strategies to mitigate risks and enhance software security in this informative session.
Access to Capital for Local-Serving Businesses - Response Panel
Panel discussion on improving capital access for local businesses, featuring insights from diverse experts on innovative funding approaches and ecosystem support.
Threat Modeling In and For Your Organization
Comprehensive guide to implementing threat modeling practices within organizations, enhancing security strategies and fostering a proactive approach to identifying potential vulnerabilities.
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
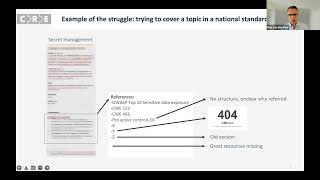
Understanding the Complete Chain of Application Security Using OpenCRE.org
Explore a comprehensive approach to application security using openCRE.org, covering key concepts and best practices for robust software protection.
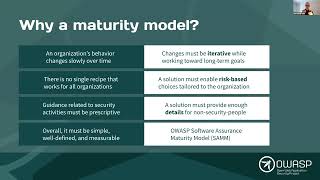
OWASP SAMM Project - Introduction to Software Assurance Maturity Model
Explore the OWASP SAMM framework for software assurance, learning key strategies to integrate security practices throughout the software development lifecycle.