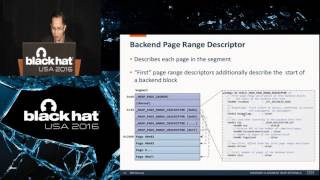
Windows 10 Segment Heap Internals
Explore Windows 10 Segment Heap internals, focusing on data structures, algorithms, and security mechanisms. Learn how to exploit memory corruption vulnerabilities in Microsoft Edge components.
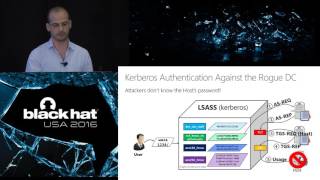
The Remote Malicious Butler Did It!
Explore remote exploitation of unattended computers using rogue Domain Controllers. Learn technical details, attack vectors, and prevention methods for enterprise security.
Ouroboros - Tearing Xen Hypervisor With the Snake
Explore a critical verification bypass bug in Xen hypervisor, allowing malicious PV guest OS to control the hypervisor and other guest operating systems. Learn about exploitation vectors and payloads.
Defense at Hyperscale - Technologies and Policies for a Defensible Cyberspace
Explore strategies for achieving defensible cyberspace through innovative technologies, operational improvements, and public policies that provide cost-effective security at scale.
What's the DFIRence for ICS?
Explore digital forensics for industrial control systems, focusing on embedded devices in critical infrastructure. Learn data collection and analysis techniques for RTUs in electric substations.
Pindemonium - A DBI-Based Generic Unpacker for Windows Executable
Explore a generic unpacking algorithm for Windows executables using Dynamic Binary Instrumentation. Learn to detect and defeat popular packing techniques, reconstruct working PEs, and handle IAT obfuscation.
Keystone Engine - Next Generation Assembler Framework
Explore Keystone, a multi-architecture assembler engine with clean API, native support for various platforms, and bindings for multiple programming languages. Ideal for reverse engineering and security research.
Dungeons Dragons and Security
Innovative security training using role-playing game to teach basic principles through building attack/defense scenarios. Engages neophytes by drawing parallels between game and real-world security challenges.
Dark Side of the DNS Force
Explore the evolution of DNS-based attacks, including random subdomain techniques, and learn about detection and mitigation strategies for protecting against these sophisticated cyber threats.
Watching Commodity Malware Get Sold to a Targeted Actor
Explore how commodity malware breaches are reclassified and upgraded for targeted attacks, and learn detection techniques to prevent threat escalation in organizational networks.
Blunting the Phisher's Spear - A Risk-Based Approach
Explore a risk-based approach to combat spear phishing, introducing the Cyber Risk Index for personalized training and access management to enhance organizational cybersecurity.
BadTunnel - How Do I Get Big Brother Power?
Discover a critical Windows flaw affecting multiple systems and applications. Learn about its wide-ranging impact and how to defend against this pervasive threat, even on unsupported systems.
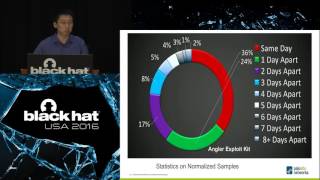
Next-Generation of Exploit Kit Detection by Building Simulated Obfuscators
Learn techniques for detecting next-gen exploit kits by simulating obfuscators. Explore implementation, evaluation, and evolution of obfuscators for 6 notorious exploit kit families to enhance cybersecurity protection.
Investigating DDOS - Architecture, Actors, and Attribution
Explore DDOS attacks, their evolution, and novel techniques for measuring, studying, and attributing them. Learn about honeypots, attack testing, and the individuals behind these cyber threats.
Language Properties of Phone Scammers - Cyberdefense at the Level of the Human
Explore forensic linguistics in cybersecurity, analyzing language patterns of phone scammers to enhance human-level defense against social engineering attacks.

The Tao of Hardware - The Te of Implants
Explore cheap hardware attacks on embedded devices and industrial control systems, including privilege escalation, kernel patching, and wireless control of PLCs. Learn about design decisions to reduce vulnerabilities.
BadWPAD
Explores WPAD protocol vulnerabilities through experiments, revealing widespread risks in networks and DNS. Presents surprising findings and discusses implications for cybersecurity.
Hardening AWS Environments and Automating Incident Response for AWS Compromises
Learn to automate incident response in AWS, collect forensic evidence, and secure your cloud environment against API key compromises through proper configuration and monitoring.
Discovering and Exploiting Novel Security Vulnerabilities in Apple ZeroConf
Uncovers critical security flaws in Apple's ZeroConf frameworks, demonstrating vulnerabilities in Multipeer Connectivity, Bonjour, and services like AirDrop, allowing impersonation and man-in-the-middle attacks.
Horse Pill - A New Type of Linux Rootkit
Explore a novel Linux rootkit that exploits container technology, bypassing UEFI secure boot and kernel module signing. Learn about its covert capabilities and discover mitigation strategies to enhance boot security.
An AI Approach to Malware Similarity Analysis - Mapping the Malware Genome With a Deep Neural Network
Explore AI-driven malware similarity analysis using deep neural networks for improved accuracy and adaptability in threat detection and classification.