Understanding SCADA's Modbus Protocol
Hands-on workshop exploring the Modbus protocol: analyze network captures, configure simulators, and generate traffic to query and fuzz Modbus devices. Practical skills for SCADA systems.
The Underground Ecosystem of Credit Card Frauds
Explore the aftermath of POS malware breaches, uncovering the organized network behind credit card fraud, from purchasing stolen data to creating counterfeit cards and cashing out.
Bar-Mitzvah Attack - Breaking SSL with 13-Year Old RC4 Weakness
Uncover SSL vulnerabilities using RC4 cipher weaknesses. Learn about passive eavesdropping attacks on TLS connections and techniques to recover secret data from encrypted communications.
Information Technology Systems in a Post-Silicon World
Explore post-silicon IT systems, emerging architectures, and AI's impact on InfoSec. Discover how innovation addresses Moore's Law limitations and shapes the future of technology and security.
I'm Not a Human - Breaking the Google reCAPTCHA
Explore techniques to bypass Google's reCAPTCHA using risk analysis manipulation, deep learning for image recognition, and automated solving methods. Discusses implications for CAPTCHA security.
Hey, Your Parcel Looks Bad - Fuzzing and Exploiting Parcelization Vulnerabilities in Android
Explore Android's Binder IPC vulnerabilities through fuzzing and exploitation techniques. Learn to identify, analyze, and exploit "BadParcel" issues for privilege escalation in high-privilege processes.

Never Trust Your Inputs - Causing Catastrophic Physical Consequences From The Sensor
Explore security vulnerabilities in analog-to-digital conversion for industrial control systems. Learn how attackers can manipulate sensor data to cause physical consequences while evading detection.
Mapping the Wireless IoT
Explore wireless IoT security challenges, signal identification techniques, and best practices for revealing unknown signals. Includes a demo of a new tool for mapping radio spectrum and identifying devices.
Break Out of The Truman Show - Active Detection and Escape of Dynamic Binary Instrumentation
Explore active detection techniques for Dynamic Binary Instrumentation, focusing on exploiting weaknesses and escaping control. Learn to identify and overcome DBI environments in cybersecurity.
Rapid Radio Reversing
Explore wireless security research techniques combining SDR and non-SDR tools. Learn efficient reverse engineering processes for analyzing and decoding radio signals in this hands-on demonstration.
Enterprise Apps - Bypassing the iOS Gatekeeper
Explore iOS security vulnerabilities through enterprise apps, examining real-world statistics and a zero-day attack that bypasses Apple's gatekeeper, revealing critical flaws in the iOS security model.
A New CVE-2015-0057 Exploit Technology
Explores CVE-2015-0057 vulnerability, User Mode Callback mechanism, and new exploit techniques in Windows kernel. Analyzes exploit methodology, vulnerability detection, and implications for system security.
DSCompromised - A Windows DSC Attack Framework
Explore a PowerShell toolkit leveraging Windows Desired State Configuration for command-and-control, malware persistence, and automatic re-infection. Learn attack techniques and defensive strategies.
Cantact - An Open Tool for Automotive Exploitation
Explore CANtact, an open-source tool for automotive network analysis. Learn to view, decode, and manipulate CAN bus traffic for reverse engineering and security testing of vehicle systems.
Hacking a Professional Drone
Explore vulnerabilities in professional drones and learn how to exploit them to take control. Discover practical fixes and remediation approaches for these security compromises.
PLC-Blaster - A Worm Living Solely in the PLC
Demonstration of a self-contained PLC worm targeting Siemens S7-1200 PLCs, showcasing network scanning, self-propagation, and remote control capabilities while evading detection.
Android Commercial Spyware Disease and Medication
Explores Android vulnerabilities exploited by spyware and proposes a detection method using fuzz testing to mitigate risks and protect user privacy on smartphones.
Automated Dynamic Firmware Analysis at Scale - A Case Study on Embedded Web Interfaces
Automated framework for discovering vulnerabilities in embedded web interfaces through dynamic firmware analysis. Validates effectiveness on 1925 firmware images from 54 vendors, uncovering critical security flaws.
The Kitchen's Finally Burned Down - DLP Security Bakeoff
Explore flaws in Data Loss Prevention solutions, including administrative interfaces and inspection engines, to understand their capabilities and shortcomings in protecting sensitive information.
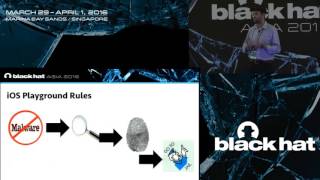
Su-A-Cyder - Homebrewing Malware for IOS Like a BO$$
Hands-on workshop for developing iOS malware using the su-A-Cyder framework. Learn techniques to create and execute malware samples on Apple devices, exploiting recent policy changes.
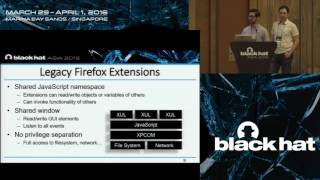
Automated Detection of Firefox Extension-Reuse Vulnerabilities
Discover a novel extension-reuse vulnerability in Firefox and learn about CROSSFIRE, a static analyzer that detects these vulnerabilities and generates exploit templates for rapid proof-of-concept creation.