How to Implement IT Security After a Cyber Meltdown
Implementing IT security post-cyber attack: strategies, challenges, and lessons learned from Saudi Aramco's 2012 incident and subsequent security unit establishment at Aramco Overseas Company.

Bringing A Cannon To A Knife Fight
Explore China's Great Cannon: its inception, functionality as a Man-in-the-Middle proxy, weaponization of users, political motivations, and future implications. Learn protective measures against this powerful censorship tool.
ROPInjector - Using Return Oriented Programming for Polymorphism and Antivirus Evasion
Explore advanced polymorphism techniques using Return Oriented Programming for antivirus evasion, with practical demonstrations of the ROPInjector tool and its effectiveness against detection methods.
Back Doors and Front Doors - Breaking the Unbreakable System
Exploring government demands for backdoor access to encrypted data, examining proposed solutions, and discussing the balance between security and privacy in digital communications.
SMBv2 - Sharing More Than Just Your Files
Unveils a new attack vector against SMBv2, affecting all IE versions. Demonstrates remote credentials theft and user impersonation from the internet, exploiting bugs for complete user compromise without interaction.
How Federal Prosecutors Use The CFAA
Explore the Computer Fraud and Abuse Act through a federal prosecutor's lens. Gain insights into charging decisions, sentencing factors, and balancing security research with law enforcement needs.
Social Engineering the Windows Kernel - Finding and Exploiting Token Handling Vulnerabilities
Explore Windows kernel token handling vulnerabilities, learn to identify and exploit them for privilege escalation, and understand patterns for conducting security reviews.
Pen Testing a City
Comprehensive methodology for reverse engineering and securing cities' IT infrastructure, exploring vulnerabilities and developing strategies for penetration testing and defense at the urban scale.
Fingerprints on Mobile Devices - Abusing and Leaking
Explore vulnerabilities in mobile fingerprint authentication, including authorization attacks, sensor spying, and backdoors. Learn to secure fingerprints and mitigate risks in this eye-opening analysis.
Universal Android Rooting Is Back
Explore universal Android rooting through kernel exploitation, focusing on a Use-After-Free bug affecting all Linux versions. Learn about innovative techniques for 64-bit devices and bypassing modern kernel mitigations.
The Memory Sinkhole - Unleashing An X86 Design Flaw Allowing Universal Privilege Escalation
Unveiling a critical x86 design flaw allowing privilege escalation, exploring forgotten backdoors, and demonstrating how to exploit vulnerabilities in processor architecture.
Commercial Mobile Spyware - Detecting The Undetectable
Uncover techniques to detect and protect against commercial mobile spyware, safeguarding personal privacy and corporate security in an era of increasing digital surveillance.
Attacking Hypervisors Using Firmware and Hardware
Explore vulnerabilities in hypervisors through firmware and hardware emulation, demonstrating attacks and their impacts. Learn about firmware rootkits and new testing modules for hypervisor security.

GameOver Zeus - Badguys and Backends
Detailed exploration of GameOver Zeus botnet, covering its operators, law enforcement investigation, and innovative legal strategies used to dismantle the cybercriminal network.
Winning the Online Banking War
Explore advanced techniques to combat banking malware, including evasion methods and a novel Zero Knowledge Protocol-based approach for securing client-server communications.
Android Security State of the Union
Explore key factors driving Android security using data from millions of devices, establishing a baseline and identifying areas for community focus and research.
Next Level Cheating and Leveling Up Mitigations
Explore advanced game cheating techniques and anti-cheat strategies, including practical attacks on popular anti-cheat engines and their implications for multiplayer gaming security.
Insecurity of Mobile Banking
Explore mobile banking app security, revealing privacy risks and vulnerabilities through static and dynamic analysis. Gain insights into global banking app practices and their implications.
Hopping on the CAN Bus
Explore automotive CAN bus systems, learn to send/receive messages, and discover vulnerabilities using CANard, an open-source toolkit for scripting CAN bus tasks.
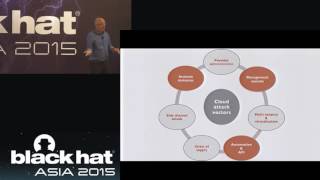
From Zero to Secure in One Minute
Automated cloud security tool for rapid instance lifecycle: pre-configured, patched, encrypted, and auto-mitigated. Introduces "Cloudefigo" for accelerated security in dynamic cloud environments.
Manna from Heaven - Improving the State of Wireless Rogue AP Attacks
Explore advanced techniques for enhancing wireless rogue AP attacks, including network spoofing and authentication bypass. Learn about a new toolkit for implementing these methods effectively.