CDPwn - Taking Over Millions of Enterprise-Things with Layer 2 Zero-Days
Unveiling critical zero-day vulnerabilities in layer 2 protocols, demonstrating their impact on enterprise device and network security, and exploring potential exploitation techniques.
What the Log - So Many Events, So Little Time
Explore Windows Event Log for efficient adversary detection, leveraging automation and MITRE ATT&CK framework to enhance cybersecurity monitoring and response capabilities.
Conclusions and Key Takeaways from Day 1
Insightful discussion on pressing InfoSec issues, including COVID-19 impact, security breaches, misinformation, and digital asset protection, featuring Black Hat Review Board members.
Biometrics and Privacy - Time to Faceoff or is that FaceApp
Explore biometric data usage, privacy legislation, and implications in APAC and globally. Learn about government and private sector practices, legal frameworks, and individual rights regarding biometric information.
Attacking and Defending Machine Learning Applications of Public Cloud
Explore techniques for attacking and defending machine learning applications in public cloud environments, focusing on visual classification vulnerabilities and countermeasures.
Identifying Multi-Binary Vulnerabilities in Embedded Firmware at Scale
Explore techniques for identifying vulnerabilities in embedded firmware, focusing on multi-binary analysis, dynamic and static approaches, and scalable solutions for IoT device security.
Cutting Edge - Microsoft Browser Security — From People Who Owned It
Deep dive into Microsoft Edge security architecture, exploring sandbox initialization, browser broker implementation, and renderer security isolation.
Real-Time Detection of Attacks Leveraging Domain Administrator Privilege
Discover a real-time method to detect attacks using Domain Administrator privileges, including Golden Tickets, through Domain Controller Event logs for immediate threat mitigation.
Network Defender Archeology - An NSM Case Study in Lateral Movement with DCOM
Explore DCOM as a lateral movement technique from attacker and defender perspectives, addressing knowledge gaps and providing methodical insights for network security professionals.
Perception Deception - Physical Adversarial Attack Challenges
Explore physical adversarial attacks on object detection systems, focusing on YOLOv3. Learn tactics to overcome challenges in real-world scenarios and understand implications for AI security.
Don't Eat Spaghetti with a Spoon - An Analysis of the Practical Value of Threat Intelligence
Explore the effectiveness of Threat Intelligence in predicting Internet malicious activity through analysis of over a million indicators across diverse real-world network sensors.
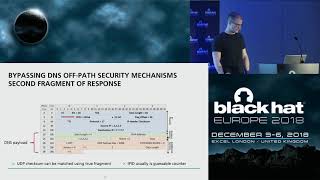
Off-Path Attacks Against PKI
Explore vulnerabilities in Certificate Authorities and learn how off-path attackers can compromise PKI security, undermining the foundation of Internet application trustworthiness.

The Undeniable Truth - How Remote Attestation Circumvents Deniability Guarantees in Secure Messaging Protocols
Explore protocol design to resist remote attestation attacks in secure messaging, covering cryptographic methods and TEE-based approaches for enhanced deniability and security.
Divide et Impera - MemoryRanger Runs Drivers in Isolated Kernel Spaces
Explore Windows 10 kernel memory protection, its vulnerabilities, and MemoryRanger's innovative approach to isolating drivers for enhanced security against malware attacks.
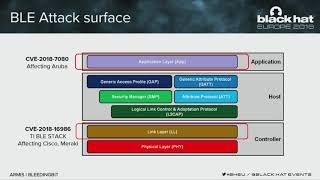
BLEEDINGBIT - Your APs Belong to Us
Explore BLEEDINGBIT vulnerabilities in BLE chips, allowing unauthenticated network penetration. Learn attack methods, packet structures, and prevention strategies for enterprise wireless access points.
Straight Outta VMware - Modern Exploitation of the SVGA Device for Guest-to-Host Escapes
Explore modern exploitation techniques for VMware Workstation's virtual graphics device, analyzing the graphics pipeline to achieve guest-to-host code execution in this in-depth security presentation.
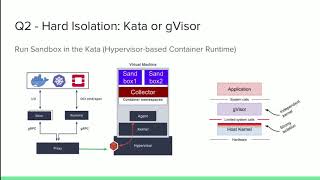
Cloud-Native Sandboxes for Microservices - Understanding New Threats and Attacks
Explore redesigned sandboxing for container environments, improving detection of microservice-oriented attacks and addressing performance challenges in contemporary systems.
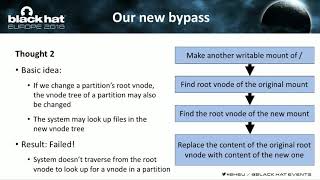
The Last Line of Defense - Understanding and Attacking Apple File System on iOS
Explore APFS architecture, previous attacks, and a new method to bypass mitigations, potentially compromising iOS file system security.

AI Gone Rogue - Exterminating Deep Fakes Before They Cause Menace
Explore the dangers of deepfakes and learn about an innovative deep learning solution for identifying complex deepfake videos, with a live demonstration of the proposed technology.
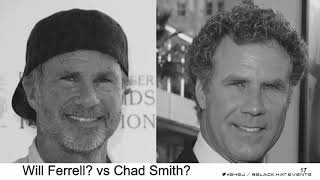
Video Killed the Text Star - OSINT Approach
Explore OSINT techniques for video analysis in security, focusing on person recognition and adapting to the growing trend of video content in internet information.
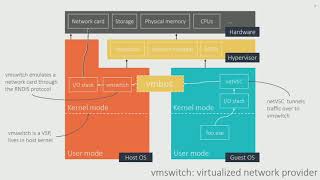
Hardening Hyper-V through Offensive Security Research
Explore offensive security research techniques to enhance Hyper-V's resilience, focusing on vulnerabilities, mitigations, and Microsoft's virtualization stack security strategies.