How We Created the First SHA-1 Collision and What it Means for Hash Security
Explore the creation of the first SHA-1 collision, its implications for hash security, and the challenges faced in developing a meaningful payload and scaling computation.
Behind the Plexiglass Curtain - Stats and Stories from the Black Hat NOC
Insider insights into Black Hat's network operations: statistics, anecdotes, and revelations from the Network Operations Center team's annual debrief.
An ACE Up the Sleeve - Designing Active Directory DACL Backdoors
Explore Active Directory DACL backdoors, their offensive potential, and stealth techniques. Learn about control relationships, elevation paths, and persistence methods in AD objects.
Cracking the Lens - Targeting HTTP's Hidden Attack-Surface
Explore hidden attack surfaces in modern web infrastructure, focusing on transparent systems for performance and analytics. Learn to identify and exploit overlooked vulnerabilities.

Broadpwn - Remotely Compromising Android and iOS via a Bug in Broadcom's Wi-Fi Chipsets
Explore a critical Wi-Fi vulnerability affecting millions of Android and iOS devices, its technical details, and potential for remote exploitation without user interaction.
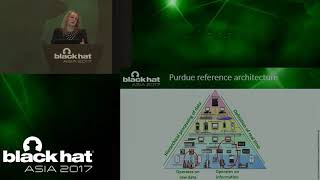
Man-in-the-SCADA - Anatomy of Data Integrity Attacks in Industrial Control Systems
Explore data integrity attacks in industrial control systems, focusing on attacker perspectives and strategies for unauthorized access to control networks and equipment.
Conclusions and Key Takeaways from Black Hat Europe 2016
Insightful discussion on critical InfoSec trends and their impact on future strategies, featuring industry experts at Black Hat Europe 2016's closing session.
Drop the ROP - Fine-Grained Control-Flow Integrity for the Linux Kernel
Explore fine-grained Control-Flow Integrity for Linux kernel security, addressing ROP attacks and dynamic kernel modules. Learn advanced mitigation techniques and implementation challenges.
Exploiting USB-IP in Linux
Explore USB/IP vulnerabilities in Linux, including buffer overflow and data injection. Learn about architecture, protocol, and security implications of this USB device sharing framework.
Conclusions & Key Takeaways from Black Hat Asia 2017
Explore key cybersecurity insights from Black Hat Asia 2017, covering topics like attacker specialization, machine learning, digital nations, and biometrics.
Bypassing Clang's SafeStack for Fun and Profit
Explore SafeStack's vulnerabilities and potential bypasses in Clang compiler, analyzing implementation weaknesses and demonstrating practical exploitation techniques for memory corruption.
Anti-Plugin - Don't Let Your App Play as an Android Plugin
Explore Android plugin technology's security risks and learn defensive strategies to protect your app from unauthorized loading and execution as a plugin.
Cross the Wall - Bypass All Modern Mitigations of Microsoft Edge
Explore techniques to bypass ASLR, DEP, and CFG exploit mitigations in Microsoft Edge on Windows 10, even with arbitrary address read/write capabilities.
Daily-Life Peeper - Bug Hunting and Exploit Techniques in IoT
Explore IoT security vulnerabilities, bug hunting techniques, and exploit methods. Learn to identify and address risks in everyday connected devices for improved cybersecurity.
Cyber Judo - Offensive Cyber Defense
Learn offensive techniques to enhance your organization's cyber defense against advanced, targeted attacks from security experts Itai Grady and Tal Be'ery.
What's on the Wireless - Automating RF Signal Identification
Explore automated RF signal identification techniques for monitoring diverse wireless technologies in organizational environments, enhancing security and management capabilities.
Evilsploit - A Universal Hardware Hacking Toolkit
Innovative method for hardware hacking using connection matrix, enabling arbitrary analog-alike connections and versatile bus interfacing for comprehensive hardware exploitation.
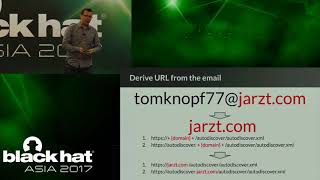
All Your Emails Belong to Us - Exploiting Vulnerable Email Clients via Domain Name Collision
Explore email vulnerabilities and domain name collisions as potential security threats, focusing on protecting email accounts from advanced persistent threats and exploitation techniques.
Mobile-Telephony Threats in Asia
Explore the mobile-telephony cybercrime ecosystem in Asia through a 7-month honeypot study, revealing SMS scams, fraudulent calls, and VoIP phishing attempts. Gain insights into real threats facing mobile users.
Securely Implementing Network Protocols - Detecting and Preventing Logical Flaws
Explore model-based testing techniques to detect logical bugs in SSL/TLS and Wi-Fi implementations, enhancing network protocol security and implementation.
Orange is the New Purple - How and Why to Integrate Development Teams with Red - Blue Teams to Build More Secure Software
Explore a new paradigm for integrating development teams with offensive and defensive teams to enhance software security throughout the development lifecycle, fostering knowledge sharing and strengthening defenses.