Mitigating Business Risks with Application Security
Explore strategies for mitigating business risks through application security, covering software assurance, supply chain management, and best practices for secure development.
New Farming Methods for the Epistemological Wasteland of Application Security
Explore innovative approaches to application security, focusing on early-stage security testing and practical tools for immediate implementation in development processes and delivery pipelines.
Doing AppSec at Scale - DevOps + Agile + CI/CD == AppSec Pipelines
Scaling AppSec through DevOps, Agile, and CI/CD practices. Learn strategies to efficiently manage application security across large organizations using automation, orchestration, and ChatOps.
AppSec Inception - Exploiting Software Culture
Explore software security culture and its exploitation with insights from Aspect Security's CEO Jeff Williams in this thought-provoking talk on application security challenges.
Application Security & User Experience
Explore the intersection of application security and user experience, focusing on balancing robust protection with seamless interactions in software design.
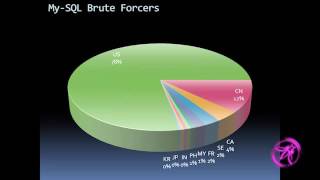
Keeping Up with the Web Application Security
Explore strategies for maintaining robust web application security in an ever-evolving digital landscape. Learn from industry experts about current threats and effective countermeasures.
Six Key Metrics - A Look at the Future of AppSec
Explore six crucial metrics shaping the future of application security. Gain insights into emerging trends and strategies for enhancing your organization's AppSec practices.
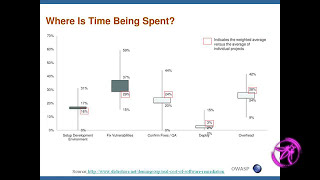
Application Security Debt and Application Interest Rates
Explore application security debt and interest rates with Chris Wysopal from Veracode. Learn strategies to manage and mitigate security risks in software development.
Stack Overflow Considered Harmful - The Impact of Copy & Paste on Android Application Security
Explores the security implications of developers copying code from Stack Overflow into Android apps, revealing alarming rates of insecure snippet usage in popular applications.
Kick Starting an Application Security Program
Learn strategies to initiate and develop an effective application security program, focusing on key elements and best practices for implementation.
iOS Application Security Assessment and Automation - Introducing SIRA
Automated iOS app security assessment tool SIRA demonstrated, revealing common flaws in AppStore products. Explores risks, testing methods, and future improvements for mobile app security.
Big Data for Web Application Security
Explore how big data analytics can enhance web application security, with real-world examples of proactive and reactive security measures using MapReduce and Cascading.
Web Application Security
Explore web application security fundamentals and best practices with expert Jeremiah Grossman in this comprehensive conference talk from Black Hat Europe 2001.
Web Application Security
Explore web application security fundamentals, vulnerabilities, and best practices with industry experts Dennis Groves and Bill Pennington in this comprehensive conference talk.
Windows 2003 - Web Application Security
Explore web application security vulnerabilities and defense strategies for Windows 2003 servers, focusing on practical techniques and real-world scenarios.
Java Decompilation & Application Security
Explore Java decompilation techniques and their impact on application security, uncovering potential vulnerabilities and best practices for secure coding.
Web Application Security and Release of "WhiteHat Arsenal"
Explore web application security and the "WhiteHat Arsenal" tool, focusing on vulnerabilities, attack methods, and defensive strategies for Windows systems.
So Long, Secure Coding - Shifting from Syntax to Secure Software Development Processes
Explore shifting from secure coding to holistic secure software development processes. Learn practical actions for enhancing security throughout the SDLC, from design to support, for more robust and resilient systems.
Appsec TLDR
Explore web application security essentials, including browser proxies, HTTP requests, cookies, and common vulnerabilities like XSS and SQL injection. Learn attacker mentality and defense strategies.
Building an Application Security Program
Strategies for establishing and expanding an effective application security program, including policy development, metrics, and alignment with software development lifecycle.
AppSec Without Additional Tools
Learn application security integration techniques, from requirements to operations, without additional tools. Explore best practices, dynamic and static scanning, and continuous integration for successful AppSec implementation.