AppSec - From Outsiders to Allies
Chris Wysopal explores AppSec's evolution from hacker-driven to a critical ally in software development, emphasizing the need for collaboration, shared accountability, and integrated security practices in modern development processes.
Why Developers Struggle with AppSec
Explore challenges developers face in application security, trust issues, and solutions for integrating security into the development process, with insights on tools and production biases.
Cheaper by the Dozen - Application Security on a Limited Budget
Discover cost-effective application security strategies using open-source tools. Learn to implement OWASP projects, assess risks, and create a robust security program tailored to your organization's needs and budget constraints.
When Application Security - The Wrong Way - Is the Right Thing for Your Organization
Discover innovative approaches to application security, including a "credit score" system, an exclusive security champions program, and improved scanning techniques for large-scale IT environments.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security approaches combining defense, offense, automation, and continuous learning for various app types, including zero trust, supply chain, and microservices.
The Tactical Application Security Program - Getting Stuff Done
Aprenda a implementar um programa de segurança tático e eficaz, focando em avaliações ágeis, resposta a incidentes e gerenciamento de bugs. Descubra por que abordagens táticas podem ser mais efetivas que estratégias de longo prazo.
The Tactical Application Security Program - Getting Stuff Done
Practical approach to application security: lightweight team, agile methods, and operational excellence. Covers assessments, bug handling, and private bug bounty programs, with actionable advice for managers and practitioners.
AndroBugs Framework - An Android Application Security Vulnerability Scanner
Explore AndroBugs Framework, a free Android vulnerability analysis system. Learn to identify and mitigate security risks in Android apps before release, enhancing app safety and user protection.
Web Application Security Crossfire
Explore web application security challenges and solutions through expert insights in this panel discussion from Black Hat USA 2004.
Abusing Bleeding Edge Web Standards for Appsec Glory
Explore risks and mitigation strategies for modern web security standards like SRI, CSP, and HPKP. Learn about implementation challenges, trade-offs, and potential exploits in legacy applications.
Getting Single Page Application Security Right
Explore SPA security challenges and solutions, covering XSS, CSP, session management, and CSRF in RESTful APIs. Learn practical strategies for building secure web applications using modern frameworks.
Developers and Application Security - Who is Responsible?
Explore findings on security responsibilities in software development, discussing implications of IoT and open-source components in everyday devices and applications.
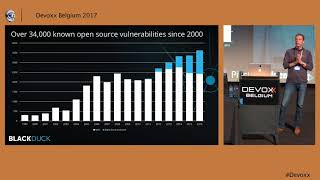
Application Security in the Age of Open Source
Explore open source software's impact on application security, including its benefits, risks, and best practices for protecting organizations against vulnerabilities and compliance issues.
10 Things Developers Need to Know About Web Application Security
Explore 10 crucial web application security practices for developers, focusing on in-depth insights to make security engaging and integral to project development.
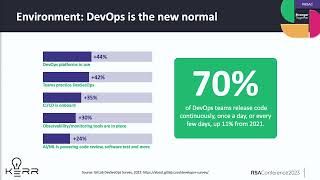
The Application Security State of the Union
Explore the current and future landscape of AppSec, including threats, vulnerabilities, tools, and strategies. Gain insights to build robust security programs and prepare for emerging challenges.
AppSec - From the OWASP Top Ten to the OWASP ASVS
Comprehensive overview of application security standards, comparing OWASP Top Ten to the more detailed ASVS, providing developers with in-depth guidance for secure software development.
Automation in Application Security
Discover strategies for preventing application attacks through automation, enhancing security beyond traditional mitigation and detection methods.
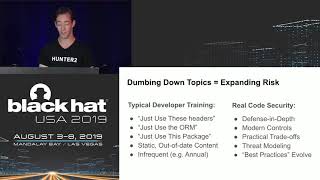
Shifting Knowledge Left - Keeping up with Modern Application Security
Explore modern application security challenges in DevSecOps, including evolving web technologies, persistent vulnerabilities, and emerging framework defenses against common threats.
IOT and AppSec
Explore the intersection of Internet of Things (IoT) and application security, examining potential vulnerabilities and strategies for safeguarding connected devices and systems.
Practical AppSec - Quick Wins for More Secure Software
Practical steps to enhance application security with minimal effort, including quick wins, finding attack surfaces, and engaging developers. Introduces a software security maturity model for measuring progress.
Mobile AppSec - Development and Alphabet Soup
Explore mobile app security challenges, vulnerabilities, and solutions. Learn effective strategies for protecting data and applications in the rapidly evolving mobile landscape.