Securing an API Ecosystem with OAuth 2.0
Explore OAuth 2.0 implementation for robust API security in this comprehensive talk by Philippe De Ryck, covering best practices and ecosystem protection strategies.
Lessons from 7 Headline-Grabbing Cloud Security Breaches
Analyze 7 real cloud security breaches, exploring attack methods, defense strategies, and specific takeaways to enhance cloud infrastructure protection and avoid similar vulnerabilities.
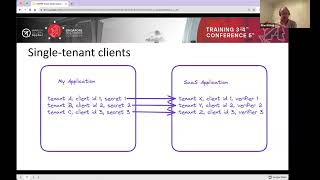
Cross-Tenant Request Forgery Attack in Multi-Tenancy Environments
Unveiling security vulnerabilities in multi-tenant SaaS platforms using OAuth, focusing on the "Cross-Tenant Request Forgery" attack and discussing potential remediations for developers.
API Governance: Creating a Success Recipe
Learn to craft a robust API governance structure, bringing order to your API landscape through clear ownership, documentation, discovery, and inventorying for consistency, scalability, and security.
Securing Identity and Authorization in Microservices
Explore Transaction Tokens (TraTs) for securing microservices, enhancing user identity and context in call chains, and defending against various attacks in distributed architectures.
Security Safari: A Journey Through the Wilderness of Securing Budding Opensource Projects
Explore essential security guidelines for open-source projects, distilled from CNCF and OpenSSF resources. Learn actionable steps to implement fundamental security measures from day one.
Unveiling the Vulnerabilities: Hacking Cloud Native Apps and Discovering the Silver Lining
Explore cloud-native app vulnerabilities, including OAuth, storage services, and API-based microservices. Learn to identify, exploit, and mitigate risks through penetration testing and automated tools.
SBOM for Cloud Services - Challenges and Applications
Explore the concept of Software Bill of Materials for cloud services, its challenges, and potential applications in enhancing security and transparency in cloud computing.
OAuth Security - Best Practices and Implementation Guidelines
Explore OAuth security essentials with expert Jim Manico, covering key concepts, best practices, and potential vulnerabilities in this comprehensive presentation.
ASP.NET Core, C#, IdentityServer4, Nuxtjs - Authorization - Episode 30
Implementación de autorización en API usando ASP.NET Core, diferenciando roles de usuario como miembros e invitados en el contexto de una biblioteca de trucos.
ASP.NET Core Dynamic Authorization with Minimal APIs - .NET 7
Learn dynamic authorization in ASP.NET Core using C# and Minimal APIs. Generate and enforce permissions, implement background refreshing, and create authorization policies for secure API development.
Strategies for Secure Development with GraphQL
Explore strategies for building secure GraphQL APIs, including security as a core feature, developer tools for secure applications, and effective request logging techniques.
Generating Authentication Tokens in Django Rest Framework
Learn to implement Token Authentication in Django Rest Framework, covering basic concepts, setup, and practical applications for secure API development.
Securing Amazon REST APIs Using Auth0
Learn to build and secure REST APIs using Amazon API Gateway and Auth0. Explore JWT-based authorization, integration with external identity providers, and best practices for API security in this hands-on webinar.
Protect Secret Keys in Jamstack Apps - Learn With Jason
Learn to secure API keys in Jamstack apps using Postman for rapid prototyping and development. Explore techniques for protecting sensitive data while building secure and efficient web applications.
Adding Auth0 Authentication to Gatsby Apps
Integrate Auth0 authentication into Gatsby apps with expert guidance. Learn implementation techniques, explore source code, and gain insights into secure user management for your web projects.

How to Hack OAuth: Real-World Attacks and Prevention Strategies
Explore real-world OAuth hacks affecting major providers, learn attack details and prevention strategies. Gain insights into technical flaws and human vulnerabilities in modern online security.
Deconstructing REST Security - OAuth, JWTs, and Microservices
Practical overview of OAuth, JWTs, and cutting-edge security for REST APIs and microservices, covering essential concepts for modern web application security.
Token Validation for Front End Frameworks
Learn to implement secure token validation in front-end frameworks. Explore best practices and techniques for enhancing authentication and protecting user data in web applications.
Protecting Routes and Securing API Endpoints in Node.js and Express - Part 3
Expand Node.js/Express app with protected routes and secure API endpoints. Learn to implement authentication, create private pages, and build a secured API for web application integration.
How to Protect an API in FastAPI with Auth0
Learn to integrate FastAPI with Auth0 for API protection using dependency injection. Covers setup, configuration, endpoint protection, and making secure requests.