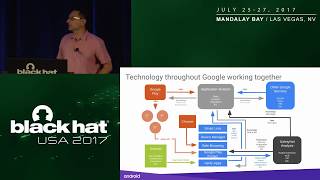
Honey, I Shrunk the Attack Surface - Adventures in Android Security Hardening
Explore Android's attack surface reduction strategies, their impact on security, and future improvements. Gain insights into technical approaches and specific bug mitigation in this comprehensive overview.
Unwrapping the Truth - Analysis of Mobile Application Wrapping Solutions
Explore mobile application wrapping solutions for BYOD, analyzing their security claims, implementation, and vulnerabilities in iOS and Android environments.
Exchanging Demands
Explore vulnerabilities in Microsoft Exchange's mobile device management, focusing on remote wipe functionality and potential exploitation through policy updates without authentication.
Dex Education - Practicing Safe Dex
Explore Android's dex file format, analyze vulnerabilities in dex analysis tools, and learn techniques to detect post-compilation modifications and protect against potential exploits.
Practical Attacks Against MDM Solutions
Explore novel proof-of-concept attack techniques on Android and iOS devices that bypass traditional mobile malware detection and circumvent common Mobile Device Management features.
Cellular Exploitation on a Global Scale - The Rise and Fall of the Control Protocol
Explore hidden cellular device controls, their vulnerabilities, and potential for global exploitation. Learn reverse engineering techniques, protocol analysis, and proof-of-concept exploits for major platforms and networks.
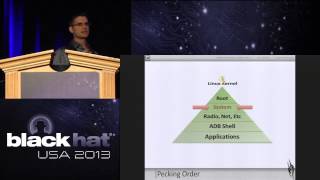
Android - One Root to Own Them All
Explore Android security vulnerabilities, focusing on bug 8219321's impact on cryptographic verification and system control. Learn about exploit creation and its implications for device security.
Endoscope - Unpacking Android Apps with VM-Based Obfuscation
Explore techniques for unpacking Android apps with VM-based obfuscation, focusing on code virtualization challenges and reverse-engineering methods for mobile app security analysis.
Bad io_uring - A New Era of Rooting for Android
Explore privilege escalation on Android devices using io_uring vulnerabilities, focusing on CVE-2022-20409 exploitation on Google Pixel 6 and Samsung S22.
Make KSMA Great Again - The Art of Rooting Android Devices by GPU MMU Features
Explores advanced Android rooting techniques using GPU MMU features, overcoming hardware and software mitigations in Android 13 devices through innovative exploitation methods.
Finding the Signal in the Noise - Quantifying Advanced Malware
Quantifying advanced malware through data analysis, focusing on finding patterns in large datasets to identify threats and improve detection methods.
ZitMo NoM Clientless Android Malware Control
Explore clientless Android malware control techniques, focusing on ZitMo NoM, and learn about potential threats and defense strategies in mobile security.
Break Me09 Stagefright - Scary Code in the Heart of Android
Explore Android's Stagefright vulnerability, its impact on device security, and potential exploitation techniques in this in-depth analysis of a critical mobile security flaw.
The Problems with JNI Obfuscation in the Android Operating System
Explore JNI obfuscation issues in Android OS, covering build process, software stack, and practical reverse engineering techniques for both static and dynamic analysis.
Stagefright - An Android Exploitation Case Study
Explore Android's Stagefright vulnerability, its root cause, consequences, and exploitation techniques. Learn about security measures, mitigations, and real-world implications for device diversity.
Stable 13 Tales From the Bug Mine Highlights from the Android VRP
Explore highlights from Android's Vulnerability Reward Program, uncovering critical security issues and their impact on mobile device safety.
Two Bugs With One PoC - Rooting Pixel 6 From Android 12 to Android 13
Explore Pixel 6 rooting techniques, vulnerabilities, and PoC creation for Android 12 and 13, focusing on the Tensor chip and Linux kernel 5.10 challenges.
Control Flow Integrity in the Linux Kernel
Explore Control Flow Integrity in Linux kernel, its implementation using Clang/LLVM, and how it protects against memory corruption attacks by validating function pointers.
So, You Want to Build an Anti-Virus Engine?
Learn to build an Android malware analysis engine using Python, combining criminal law principles with bytecode analysis to create a robust scoring system that can detect threats even in obfuscated code.
Unlocking Secrets of Proprietary Software Using Frida
Explore binary application internals with Frida, a powerful instrumentation framework. Learn to hook functions, trace data, and analyze software across multiple platforms through hands-on demos.
Better Bug Bounty Hunting, CTFs and Reverse Engineering - Cybertalk Episode 8
Insights on improving bug bounty skills, starting in pentesting, choosing laptops for security work, and comparing Android vs Windows reverse engineering techniques.