Path Traversal Attacks on Android - Ekoparty 2023
Explora vectores de ataque de path traversal en Android, técnicas para sobrescribir y leer archivos internos, y métodos de mitigación. Presentado por Anderson Valencia, pentester de aplicaciones web y móviles.
Common Android Deep Links and WebViews Exploitations - Mobile Hacking
Explore Android deep links and WebViews vulnerabilities, learn exploitation techniques, and discover practical mitigation strategies to enhance mobile app security against emerging threats.
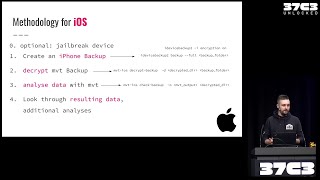
Introduction to Smartphone Malware Forensics
Überblick über Techniken und Open-Source-Tools zur Erkennung von Malware auf iOS- und Android-Smartphones, mit Fokus auf Stalkerware und Staatstrojaner. Praktische Einführung in einvernehmliche Smartphone-Forensik.
Dynamic Analysis of Complex Mobile Applications
Aprenda a realizar análisis de seguridad en aplicaciones móviles complejas, superando protecciones criptográficas y encontrando vulnerabilidades mediante herramientas como Frida, Burp Suite y Brida.
KRACK Attack Proof of Concept on Android and Linux Devices
Demonstration of KRACK Attack Proof of Concept on Android/Linux devices, including installation, configuration, and testing steps for this Wi-Fi security vulnerability.
Hacker101 - Android Quickstart
Learn essential Android app hacking concepts, tools, and techniques in this quick guide. Explore APK structure, emulators, decompilation, and security testing methods for successful mobile app penetration testing.
Fun with Frida on Mobile - Leveraging Dynamic Analysis Tools
Explore Frida for mobile app analysis: trace functions, examine memory, bypass security. Practical examples for iOS and Android, including SSL pinning bypass and custom tool creation.
What You Missed During Black Hat and DEFCON - Security Conference Highlights
Explore key highlights from Black Hat and DEFCON, including car hacking, Android security, policy changes, and malware analysis, as presented by Bugcrowd's VP of Operations.
Identifying & Avoiding Android App Protections - Tim Strazzere, LevelUp 2017
Techniques for quickly identifying and bypassing Android app protections to improve bug bounty hunting efficiency and ROI.
OSInt, Cyberstalking, Footprinting and Recon: Getting to Know You - Part 3 Metadata and Miscellaneous Topics
Explore metadata, file formats, and EXIF information for effective digital footprinting and reconnaissance. Learn practical tools and techniques for gathering valuable intelligence.
The Mobile Malware Maze - 15 Years of Evolution
Explore the 15-year evolution of mobile malware, from Symbian OS to Android, examining shifting trends and current threats in this comprehensive keynote on mobile security.
Secure Messengers and Man in the Contacts Attack
Explore the Man in the Contacts attack, its implementation in a mobile game, and its potential for spear phishing in secure messaging apps. Learn about vulnerabilities and possible mitigations.
SSL Traffic Interception on Mobile Devices - Analysis and Protection
Análisis detallado de incidentes SSL en aplicaciones móviles, revelando patrones globales, casos notables y soluciones para desarrolladores contra la interceptación de tráfico.
Calm Down: HTTPS Is Not a VPN
Explore HTTPS limitations, privacy concerns, and security implications in web communications. Learn about packet capture, fingerprinting, and potential vulnerabilities in encrypted connections.
OWASP Mobile Top Ten 2014 - The New Lack of Binary Protection Category
Explore the new OWASP Mobile Top Ten category: lack of binary protections. Learn about risks to mobile apps, their impact on the app economy, and strategies to mitigate these threats on iOS and Android platforms.
Mobile Security Track - AppSec Europe 2014
Explore cutting-edge mobile security topics at AppSecEU 2014, covering iOS and Android vulnerabilities, OWASP Mobile Top Ten, smart storage scanning, and practical defense strategies for app developers.
Mobile App Analysis with Santoku Linux
Explore mobile app analysis using Santoku Linux, covering forensics, security testing, and malware analysis for Android and iOS platforms. Live demos showcase practical applications of preinstalled tools.
AppSecUSA 2014 - Breakers Track Sessions
Explore cutting-edge web and mobile security topics, including mobile attacks, use-after-free exploitation, static analysis, runtime manipulation, and top hacking techniques from AppSecUSA 2014.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
Attacking the Samsung Galaxy A Boot Chain
Explore Samsung Galaxy A* boot chain vulnerabilities and attack techniques for enhanced mobile security understanding.
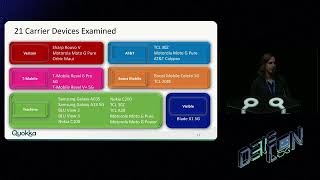
Security Vulnerabilities in Prepaid Android Smartphones - A Comprehensive Analysis
Uncover critical security vulnerabilities in prepaid Android smartphones through detailed analysis of 32 devices, revealing system-level flaws and privilege escalation risks in pre-loaded software.