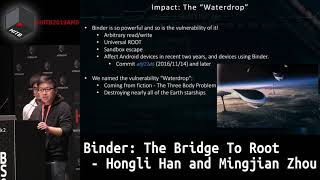
Binder - The Bridge To Root - Hongli Han and Mingjian Zhou
Exploración detallada de la vulnerabilidad "Waterdrop" en el controlador Binder de Android, que permite escalar privilegios y obtener acceso root en dispositivos populares, incluyendo los Pixel más recientes.
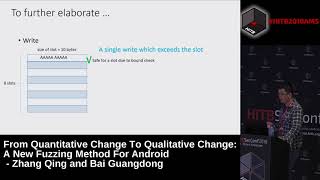
A New Fuzzing Method for Android
Innovative Android fuzzing method combining function points to find vulnerabilities. Proven effective with 50+ bugs discovered on major OEM devices, inspiring new approaches in mobile security research.
Hiding in Plain Sight - PhantomLance Comes into Play
Uncover the sophisticated PhantomLance Android spyware, its evolution, deployment tactics, and connections to other malware campaigns in this cybersecurity investigation presentation.
Hardening Android Against Ransomware, One Dessert at a Time
Explore Android's evolving defenses against ransomware, from KitKat to Nougat, and learn about system improvements and proactive measures to protect devices, data, and user experience.
A Universal Way to Exploit Android PendingIntents in High-profile and System Apps
Explore Android PendingIntent vulnerabilities in high-profile apps, learn exploitation techniques, and discover security implications for developers and system integrity.
A Deep Dive into Privacy Dashboard of Top Android Vendors
Uncovers flaws in Android vendors' privacy dashboards, revealing how malicious apps can bypass monitoring and benign apps trigger false alarms. Explores implementation differences across top vendors.
Stealth Mango and the Prevalence of Mobile Surveillanceware
Unveiling nation-state mobile surveillance tools Stealth Mango and Tangelo, exploring their capabilities and impact on government and military targets across multiple countries.
ZEROing Trust - Do Zero Trust Approaches Deliver Real Security?
Analyze effectiveness of zero trust security across modern OS platforms, examining measurable properties to establish trust in various threat scenarios.
The Tangled Webview - Javascriptinterface Once More
Unveils new Android WebView vulnerabilities related to JavascriptInterface, bypassing all verifications. Presents a novel attack model and discusses security implications for mobile app developers.
DroidGuard - A Deep Dive into SafetyNet
Explore SafetyNet's internal mechanisms, VM design, and security checks for detecting Magisk, emulators, rooted devices, and Pegasus in this comprehensive analysis of DroidGuard.
Explosion - The Hidden Mines in the Android ION Driver
Uncover vulnerabilities in Android's ION driver, explore root causes, and learn how to achieve privilege escalation. Gain insights into preventing similar security issues in the Android ecosystem.
Typhoon Mangkhut - One-click Remote Universal Root Formed with Two Vulnerabilities
Exploit chain for remote Android root using Chrome and Binder vulnerabilities. Demonstrates bypassing security mitigations to achieve one-click root access on modern Pixel devices.
Faux Disk Encryption - Realities of Secure Storage on Mobile Devices
Explore mobile device data security challenges, debunk full-disk encryption myths, and learn sophisticated secure storage techniques for iOS and Android, addressing real-world application vulnerabilities.
Man in the Binder - He Who Controls IPC, Controls the Droid
Explore Android's Binder IPC system, its security implications, and potential vulnerabilities through a POC rootkit demonstration and in-depth analysis of low-level Binder operations.

Stagefright - Scary Code in the Heart of Android
Exploring Android's Stagefright framework vulnerabilities, focusing on discovery techniques, OS internals, and security implications. Demonstrates proof-of-concept code and discusses mitigation strategies.
Attacking the Linux PRNG on Android
Explore vulnerabilities in Android's Linux PRNG, focusing on early boot attacks and real-world exploitation vectors. Learn about potential security risks and mitigations for embedded platforms.
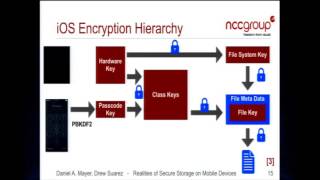
Faux Disk Encryption - Realities of Secure Storage on Mobile Devices
Explore mobile device data security challenges, debunk full-disk encryption myths, and learn sophisticated secure storage techniques for iOS and Android to protect against physical access attacks.
Authenticator Leakage Through Backup Channels on Android
Explore Android authentication vulnerabilities through backup channels. Learn about security risks, attack vectors, and mitigation strategies for app developers and protocol analysts.
Certifi-gate - Front-Door Access To Pwning Millions Of Androids
Explore Android vulnerabilities affecting millions of devices, including Lollipop. Learn about exploits, technical root causes, and remediation strategies for these critical security flaws.
Universal Android Rooting Is Back
Explore universal Android rooting through kernel exploitation, focusing on a Use-After-Free bug affecting all Linux versions. Learn about innovative techniques for 64-bit devices and bypassing modern kernel mitigations.
Android Security State of the Union
Explore key factors driving Android security using data from millions of devices, establishing a baseline and identifying areas for community focus and research.