Hacking AI - Security & Privacy of Machine Learning Models
Explore adversarial machine learning with Prof. Dan Boneh, examining security challenges in AI models, defenses against attacks, and the balance between accuracy and privacy in ML systems.
Cross-Domain Transferability of Adversarial Perturbations - CAP6412 Spring 2021
Explore cross-domain transferability of adversarial perturbations, focusing on generative models, discriminator loss, and experimental results in this advanced computer vision lecture.
The Privacy Considerations of Production Machine Learning
Explore state-of-the-art research on privacy in machine learning, including estimating and defending against privacy leakage, secure collaboration, and machine unlearning for GDPR compliance.
Formal Backdoor Detection Games and Deceptive Alignment in Machine Learning
Explore the strategic interplay between attackers and defenders in machine learning backdoors, examining implications for AI alignment and deceptive behavior detection.
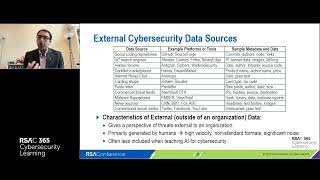
AI for Cybersecurity - Overview of the Field and Promising Future Directions
Explore AI applications in cybersecurity, including threat intelligence and adversarial machine learning. Learn about data sources, limitations, and future directions in this field.
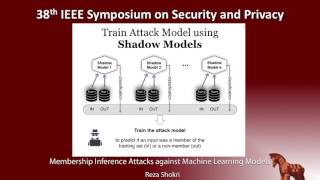
Membership Inference Attacks against Machine Learning Models
Explore membership inference attacks on machine learning models, focusing on techniques to determine if specific data was used in training, with implications for privacy and security in ML applications.
Defense Against the Dark Arts
Overview of adversarial example research in machine learning, exploring attacks, defenses, and future directions for enhancing AI security and robustness against malicious inputs.
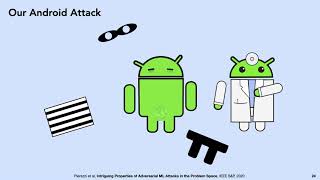
Intriguing Properties of Adversarial ML Attacks in the Problem Space
Explores novel formalization of adversarial ML evasion attacks in problem-space, focusing on real-world implications. Proposes a new attack on Android malware, demonstrating the feasibility of "adversarial-malware as a service".
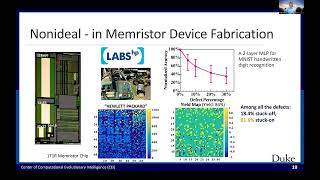
TinyML Talks - Software-Hardware Co-design for Tiny AI Systems
Explore efficient AI models, hardware-friendly compression, and topology-aware design for resource-constrained systems. Learn cross-optimization techniques and distributed learning for scalable AI solutions.
Trusted and Responsible AI - Explainability, Adversarial Attacks, Bias, and Fairness
Explore key aspects of responsible AI: explainability, adversarial challenges, bias mitigation, and fairness. Learn strategies for building trustworthy and ethical AI systems in real-world applications.
Defending Against Adversarial Model Attacks Using Kubeflow
Learn to protect AI models from adversarial attacks using Kubeflow. Explore threats, defenses, and practical implementations in this comprehensive presentation by IBM experts.
The Cost of Democratization - Open Source and the Future of Ethical Use
Explore the ethical implications of open-source AI, focusing on responsible development, legal challenges, and societal impacts in this thought-provoking keynote by Dr. Rumman Chowdhury.
Multi-Instance Adversarial Attack on GNN-Based Malicious Domain Detection
Explore multi-instance adversarial attacks on Graph Neural Networks for detecting malicious domains, enhancing cybersecurity defenses against sophisticated threats.
Multi-Instance Adversarial Attack on GNN-Based Malicious Domain Detection
Explore multi-instance adversarial attacks on Graph Neural Networks for detecting malicious domains, enhancing cybersecurity defenses against sophisticated threats.
Adversarial AI/ML Issues and Defense Strategies
Explore adversarial AI/ML challenges and defense mechanisms with Dr. Dipankar Dasgupta, gaining insights into critical cybersecurity strategies for machine learning systems.
Spotting the Differences - Quirks of Machine Learning in Security
Explore challenges in applying machine learning to cybersecurity, including dataset issues, adversarial tactics, and evaluation problems. Learn about potential solutions and future directions in this field.
JARVIS Never Saw It Coming - Hacking Machine Learning in Speech, Text and Face Recognition
Explore hacking techniques for machine learning systems in speech, text, and facial recognition, including exploits, backdoors, and adversarial attacks. Live demo included.
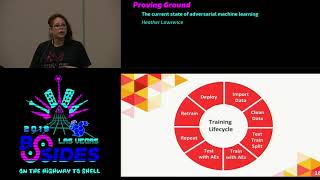
The Current State of Adversarial Machine Learning
Explore adversarial machine learning's current landscape, including attack types, vulnerabilities, and defense strategies. Gain insights into visual understanding and notable research in this critical field.
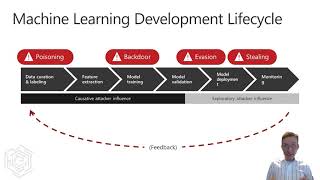
The Practical Divide between Adversarial ML Research and Security Practice - A Red Team Perspective
Exploring the gap between adversarial ML research and real-world security practices, highlighting challenges and lessons learned from Microsoft's Machine Learning Red Team engagement.
System for Deepfake Detection - DeepAudioDetector - Ekoparty 2021
Explora técnicas avanzadas de detección de deepfakes de audio utilizando inteligencia artificial, con énfasis en metodologías, experimentos y herramientas de libre uso para enfrentar amenazas cibernéticas emergentes.
Practical Defenses Against Adversarial Machine Learning
Explore real-world attacks on ML systems, from recommendation engines to email filters, and learn practical defense strategies against adversarial machine learning threats.