Orchestrating Least Privilege in Docker Environments
Explore Docker's approach to orchestrating least privilege, enhancing security in distributed applications through efficient privilege management and access control.
Docker Build: Using Scoped Personal Access Tokens
Learn to enhance Docker Hub security by setting up and using scoped personal access tokens, improving access control for distributed applications and container management.
Navigating the Service Mesh Ecosystem
Explore service mesh patterns, APIs, and implementations for Kubernetes microservices. Learn about CNCF's Service Mesh Interface and Microsoft's Open Service Mesh project for traffic management and observability.
Modernizing Authorization for Cloud Native Applications Using OpenFGA
Explore OpenFGA, a CNCF project combining ReBAC and ABAC for flexible, scalable centralized authorization in cloud-native apps. Learn its inner workings and successful use cases.
Kubernetes Authentication and Authorization at Robinhood - Lessons from Reductions, Migrations, and Designing Automation
Explore Robinhood's journey in implementing least privilege for Kubernetes RBAC, including challenges, solutions, and lessons learned in managing authentication and authorization.
RBACdoors - How Cryptominers Exploit RBAC Misconfigurations
Explore how cryptominers exploit RBAC misconfigurations in Kubernetes clusters, including attack techniques, detection methods, and prevention strategies for enhanced security.
Preparing to Implement and Secure Microsoft 365 Copilot
Explore key tasks for implementing Microsoft 365 Copilot, including prerequisites, data preparation, licensing, and security measures to protect sensitive business information.
Securing Generative AI - Back to the Future Edition
Explore a trust framework for generative AI, addressing concerns like data handling, PII leakage, and LLM manipulation through access control, authenticity, auditing, and data protection measures.
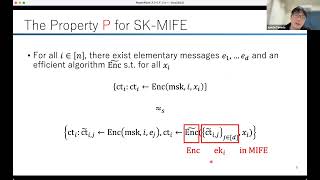
Attribute-Based Encryption and Functional Encryption - TCC 2022 Session
Explore advanced cryptographic techniques: Attribute-Based Encryption (ABE) and Functional Encryption (FE) in this comprehensive session from TCC 2022.
Securely Sharing Kubernetes Clusters with Lens Spaces
Simplify secure Kubernetes cluster sharing with Lens Spaces. Learn to leverage RBAC, automate access, and empower developers with easy monitoring, debugging, and deployment capabilities.
BPF_LSM and fsverity for Binary Authorization
Flexible binary authorization solution using BPF_LSM and fsverity for enhanced system security. Combines file integrity checksums, secure signing, and access control enforcement.
Attribute-Based Access Control Framework for IoT
Explore an open-source authorization framework for IoT, overcoming limitations of XACML and OAuth. Learn about app-specific policies using attributes for dynamic, location-specific roles in device provisioning.
Application Whitelisting: Preventing Unknown Software Execution
Learn about application whitelisting for system security, including implementation, policy design, and real-time system integrity maintenance. Explore open-source solutions and broader security strategies.
Kubernetes in Highly Restrictive Environments
Explore enterprise-grade Kubernetes deployment strategies, focusing on security, governance, and compliance in restrictive environments. Learn about HA, disaster recovery, and future trends.
Overview of the Linux Kernel Security Subsystem
Explore Linux kernel security: history, components, and community involvement. Learn about access control, capabilities, auditing, and security modules from a Microsoft expert.
Overview and Recent Developments in Smack Linux Security Module
Explore Smack Linux Security Module's current state, recent developments, and practical applications in this comprehensive overview by Intel expert Casey Schaufler.
NoSQL Is Not NoVulnerable - Exploring Security Risks in NoSQL Databases
Explores vulnerabilities in NoSQL databases, comparing threats to traditional SQL systems and demonstrating new attacks exploiting complex data types like JSON to bypass application-level access controls.
Deep Dive into Landlock Internals
Explore Landlock's security sandboxing features, internals, and roadmap. Learn about access control, ruleset creation, and policy composition for enhanced system protection.
Sandboxing Applications with Landlock
Learn about Landlock, a Linux security feature for sandboxing applications. Explore its use cases, implementation, and benefits for developers and system administrators.
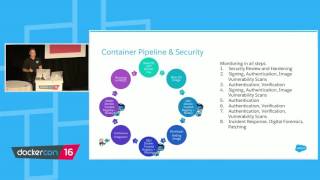
Securing the Container Pipeline at Salesforce - Docker Use Case
Securing Docker containers at Salesforce: infrastructure, pipeline security, monitoring, forensics, and automation for rapid containerization while maintaining data sensitivity and customer trust.
Secure Substrate: Least Privilege Container Deployment
Explore Docker's approach to secure container deployment using least privilege principles, focusing on preventing privilege escalation and unauthorized access in distributed systems.