Securing Access to Kubernetes Infrastructure with Zero Trust Principles
Learn how to apply zero trust principles to secure access to Kubernetes infrastructure across multiple environments, ensuring controlled and audited cluster access for various teams and systems.
Hardening Kubeflow Security for Enterprise Environments
Learn about Kubeflow security vulnerabilities, best practices, and improvements for enterprise environments. Gain insights on addressing unauthorized access, user impersonation, and data protection in MLOps platforms.
Implementing an Auditable Access Control Strategy Using Cluster Certificate Authority Rotation
Learn how to implement a zero-downtime strategy for rotating cluster certificate authorities and downstream certificates in Kubernetes, ensuring secure and auditable access control.
GitOps and CI/CD: Maintaining Security in the Age of Automation
Explore best practices for securing GitOps and CI/CD pipelines, covering access control, communication, testing, secrets management, and monitoring. Learn from Red Hat's SRE experiences to enhance your pipeline security.
Beyond Cluster-Admin - Getting Started with Kubernetes Users and Permissions
Learn to implement users and permissions in Kubernetes clusters, covering user provisioning methods, RBAC for fine-grained access control, and strategies for both managed and self-hosted environments.
How the Basics of Kubernetes Authentication Scale for Organizations
Explore Kubernetes RBAC for flexible team access. Learn basics, identity details, common issues, limitations, auditing, and real-world patterns. Includes live demos for DevOps culture support.
Securing Kubernetes
Explore Kubernetes security strategies and best practices to protect your containerized applications and infrastructure in this informative session.
Top 5 Authorization Trends in 2022 - A Year in Review
Explore the top 5 authorization trends of 2022 in cloud-native computing, offering insights into evolving security practices and technologies.
Kubernetes Environments Visualization - Strategies and Solutions at GitLab
Explore GitLab's approach to visualizing Kubernetes environments, managing access, and leveraging the GitLab platform for effective environment management and resource visualization.
RBAC to the Future: Untangling Authorization in Kubernetes
Explore Kubernetes RBAC essentials, from its inner workings to enterprise-level strategies. Learn to design, automate, and monitor least-privilege configurations for enhanced security and efficiency.
Deploying Policy-as-Code with Readable Rego Policies and Open Policy Agent
Learn to implement Policy-as-Code using Open Policy Agent and Rego language. Explore deployment strategies, centralized management, and best practices for writing clear, effective policies in cloud-native environments.
Save Your Pipelines with Tekton Results - Improving CI/CD Infrastructure Stability
Explore Tekton Results for archiving and querying pipeline data, improving CI/CD infrastructure stability, performance, and usability in Kubernetes environments.
Enabling Sidecar in KEDA for Serverless Security with Azure AD Workload Identity
Explore implementing the sidecar pattern in KEDA with Azure AD Workload Identity for enhanced security and access control in serverless architectures on Kubernetes.
Container and Kubernetes Security Policy Design - 10 Critical Best Practices
Explore 10 crucial best practices for designing robust security policies in container and Kubernetes environments, enhancing protection and mitigating risks.
Skip the Anxiety Attack - Build Secure Apps with Docker and Kubernetes
Learn to build secure applications using Docker and Kubernetes, reducing anxiety and enhancing your development process with industry-leading containerization and orchestration technologies.
Enabling High Assurance and Sensitive Container Workloads with Encrypted Images
Explore encrypted container images to protect sensitive code and data, enforce security policies, and control execution environments for high-assurance workloads in enterprise settings.
Controlling Script Execution in Linux - Security Mechanisms and Challenges
Explore kernel-managed script execution control in Linux, addressing challenges and implementation approaches for a consistent global policy.
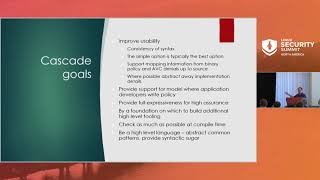
Cascade - A New High Level SELinux Policy Language
Explore Cascade, a new SELinux policy language designed to improve usability and simplify application policy writing for developers with minimal SELinux experience.
Smack Reference Policy: Creating a Rule Set for Linux Distributions
Explore Smack Linux security module, its unique features, and a new effort to create a reference rule set for major Linux distributions. Learn about threat protection and implementation challenges.
Building Apps in Kubernetes: The Unforgiving Sea of Containerization and the Lifesaver Tools
Explore key security challenges in Kubernetes app development and learn practical solutions using open-source tools. Gain insights from real-life examples to navigate the ecosystem confidently.
Stop Sharing Your Kubernetes Cluster Credentials - Sharing is Not Caring
Learn best practices for securing Kubernetes cluster credentials, protecting against unauthorized access, and implementing robust authentication methods for enhanced cluster security.