Proof That Windows Computer Forensics is Sexy
Explore Windows computer forensics techniques and tools, uncovering hidden data and digital evidence in this engaging presentation on digital investigation.
Pass the Hash Techniques for Advanced Network Penetration - Lecture 10
Learn advanced techniques for Pass the Hash attacks, enhancing your penetration testing skills and understanding of network security vulnerabilities.
Windows Command Line Incident Response - Outerz0ne 2011
Explore Windows command line tools for effective incident response, enhancing your ability to investigate and mitigate security breaches efficiently.
Pen-Testing Practice in a Box: Assembling a Virtual Network
Learn to set up a virtual network for penetration testing practice, covering VirtualBox installation, VM configuration, networking options, and installing essential tools and environments.
Attack Surface and Security Implications of eSIM Technology
Explore the security vulnerabilities and potential risks associated with eSIM technology in mobile phones and desktop devices, raising awareness about offensive operations and post-compromise scenarios.
Hacking Alexa and Cortana: Vulnerabilities in Voice Assistant Partnerships
Explore innovative "Evil Maid" attacks on Windows, vulnerabilities in Cortana-Alexa integration, and the challenges of merging new concepts with existing security mechanisms. Gain insights into AI and IoT security.

Pcaps Ahoy! Commodity Malware Infections on Windows Hosts - Security Onion Conference 2018
Explore commodity malware infections on Windows hosts through packet capture analysis, enhancing your network security skills and threat detection capabilities.
Bleachbit - Open Source, Privacy Minded System Cleaning Tool for Windows, Linux, and MacOS
Explore Bleachbit, an open-source tool for system cleaning and privacy protection. Learn installation, settings, usage in admin and non-admin modes, and discover its powerful features for enhancing system performance and security.
WHIDS Integration with MISP
Explore WHIDS integration with MISP for enhanced threat intelligence sharing and incident response capabilities in cybersecurity operations.
Exploiting Group Policy Objects for Persistence and Lateral Movement
Explore how Group Policy Objects can be exploited for malware distribution and network persistence. Learn about PowershellEmpire modules and countermeasures for enhanced cybersecurity in enterprise environments.
The Rise of Malicious MSIX Files
Explore the emerging threat of malicious MSIX files, their impact on cybersecurity, and strategies for detection and prevention in this insightful conference presentation.
Windows Red Team Lateral Movement Techniques - PsExec and RDP
Explore lateral movement techniques on Windows using PsExec and RDP. Learn how adversaries pivot through systems to gain access and achieve objectives stealthily.
Windows Red Team Privilege Escalation Techniques - Bypassing UAC and Kernel Exploits
Explore Windows privilege escalation techniques, including UAC bypassing and kernel exploits. Learn adversarial methods to gain higher system permissions and enhance your cybersecurity skills.
Windows Red Team - Dynamic Shellcode Injection and PowerShell Obfuscation
Explore dynamic shellcode injection into executables and PowerShell obfuscation for Windows defense evasion. Learn advanced techniques to avoid detection during system compromise.
Installing and Configuring Wazuh for SIEM - Blue Team Operations
Learn to set up Wazuh SIEM for detecting intrusions, attacks, and malicious activity. Covers installation and agent configuration on Windows and Linux for effective security data management.
Bypassing UAC with UACMe - HEK.SI 2022 Conference Presentation
Comprehensive guide to bypassing User Account Control on Windows 10 for privilege escalation, presented at HEK.SI 2022. Covers techniques using UACMe tool to elevate privileges and enhance system access.
Windows Enumeration with winPEAS
Automate Windows local enumeration and identify privilege escalation vectors using winPEAS. Learn efficient techniques for system analysis and vulnerability detection.
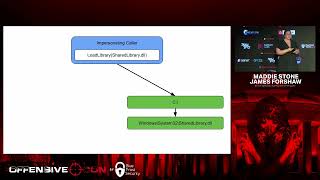
The Print Spooler Bug that Wasn't in the Print Spooler
Explore a unique Windows vulnerability discovery, from initial bug report to full exploit chain, with insights on Microsoft's patch process and security implications.
Radxa X4 N100 Single Board Computer Review and Performance Analysis
Explore the Radxa X4 N100 single board computer, comparing its performance with Raspberry Pi 5 and demonstrating Windows 11 and Linux Mint capabilities. Learn about cooling solutions and temperature management.
Unveiling the Cracks in Virtualization - VMware Workstation Escape
Explore VMware Workstation vulnerabilities, focusing on USB controller exploits. Learn about information leakage, arbitrary read/write, and bypassing Windows protections in virtualization escapes.

CrowdStrike IT Outage Explained - Kernel Mode Driver Analysis
Detailed analysis of CrowdStrike's IT outage from a Windows developer's perspective, focusing on kernel mode drivers and system vulnerabilities.