CertifiedDCOM - The Privilege Escalation Journey to Domain Admin with DCOM
Uncover a critical DCOM vulnerability allowing remote privilege escalation to Domain Admin in Windows networks. Learn about DCOM internals and exploit techniques for Active Directory takeover.
Cross the Wall - Bypass All Modern Mitigations of Microsoft Edge
Explore techniques to bypass ASLR, DEP, and CFG exploit mitigations in Microsoft Edge on Windows 10, even with arbitrary address read/write capabilities.
Java Packaging Tool - Create Native Packages to Deploy Java Applications
Explore jpackage, a new tool in JDK 14 for creating native installable packages for Java applications across Windows, macOS, and Linux platforms.
Java Packaging Tool - Create Native Packages to Deploy Java Applications
Explore jpackage tool for creating native installable packages for Java applications across Windows, macOS, and Linux platforms, with examples and deployment strategies.
Unexpected Exposures in the Secure Shell - SSH Security Testing and Research
Delve into SSH security vulnerabilities, implementation challenges, and exploitation techniques across various platforms, featuring the new open-source testing tool 'sshamble'.
Outlook Unleashing RCE Chaos: Exploiting CVE-2024-30103
Dive into the critical Outlook security vulnerabilities, exploring remote code execution exploits through COM objects, NTLM leaks, and essential mitigation strategies for enterprise protection.
Protecting Windows Credentials - An Excessive Guide for Security Professionals
Comprehensive guide for security professionals on safeguarding Windows credentials, covering architecture, isolation, exploit mitigation, and containment strategies for enhanced system protection.
Developing on Windows - and Linux - and Remotely in 2020
Explore modern development practices across Windows, Linux, and remote environments, covering cloud technologies, automation, and cross-platform tools for efficient coding workflows.
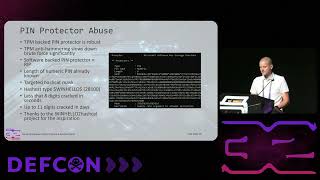
Abusing Windows Hello Authentication Without Biometric Data
Delve into Windows Hello's security vulnerabilities and authentication mechanisms, exploring attack vectors and hardware protection bypasses for biometric authentication without physical compromise.
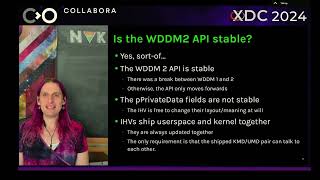
Running Mesa-Based Graphics Drivers on Windows Using WDDM2
Dive into the technical journey of porting RADV drivers to Windows, exploring WDDM2 kernel API, reverse engineering AMD interfaces, and implementing Mesa-based drivers for cross-platform compatibility.
Insecure Remote Operations: Windows Living Off the Land Techniques - Session 8
Dive into Windows remote operations security, exploring protocols, APIs, and admin tools through real-world examples. Learn powerful techniques for both defensive and offensive security operations.
Windows Hello for Business Security Analysis and Authentication Protocol Deep Dive - Lecture 10
Explore Windows Hello for Business authentication internals, security vulnerabilities, and attack vectors in Azure AD environments, focusing on key provisioning and credential management.
Modern Stuxnet-Style Attacks Using Filesystem Vulnerabilities and NTFS Exploits
Explore modern cyber attack techniques inspired by Stuxnet, focusing on filesystem vulnerabilities, NTFS exploits, and advanced persistence methods while learning effective defense strategies.
Detecting and Triaging Modern Windows Rootkits
Discover modern Windows rootkit detection techniques, memory forensics, and event log analysis methods to combat evolving kernel-level malware threats in Windows 10 and beyond.
Windows System Monitor (Sysmon) for Incident Investigation and Threat Response
Master Windows System Monitor (Sysmon) for incident investigation, learning to track program execution, registry writes, and DNS queries to effectively trace threat actor activities and enhance system security.
Protect Your Most Sensitive Users with Protected Users Group in Windows Server
Discover how Windows Server's Protected Users Group safeguards sensitive accounts, learn its attack-thwarting capabilities, and implement practical strategies for enhanced security in Active Directory environments.
Driving Your Own Vulnerability: How to Navigate the Road of BYOD Attacks
Explore Windows driver vulnerabilities and BYOD attack prevention through real-world case studies, understanding threat categories and security implications for effective system protection.
Unparalleled RDP Monitoring to Reveal Attackers' Tradecraft
Dive into advanced RDP attack monitoring techniques and threat actor behaviors through a unique D&D-themed analysis of cybersecurity tradecraft and defensive strategies.
WINE Pairing with Malware - Using Linux Tools for Malware Analysis
Discover how to leverage WINE and Linux tools for malware analysis, extracting forensic evidence, and testing offensive security techniques without expensive sandboxes.
Spooky Authentication at a Distance - Post-exploitation Techniques for Windows Environments
Discover innovative post-exploitation techniques for proxying Windows authentication protocols remotely, enabling user impersonation and domain control without elevated privileges.
Automatic Exploitation of TLS Certificate Validation Vulnerabilities
Explore TLS certificate validation vulnerabilities and their automated exploitation using certmitm, featuring real-world attacks on iOS and Windows 11 systems.