Cilium Beyond Linux: Extending eBPF to Windows Infrastructure
Explore Cilium eBPF's extension to Windows, covering current capabilities, future roadmap, and challenges in adapting Linux-based features for enhanced network performance and security on Windows infrastructure.

AWS EC2: From Beginner to Expert - Comprehensive Guide and Real-Time Project Deployment
Master AWS EC2 from basics to advanced, covering instance setup, VPC configuration, security, scaling, load balancing, and EBS. Deploy a real-time RESTful API project using EC2, ALB, Route 53, RDS, Jenkins, and Terraform.
WoW Hell - Rebuilding Heaven's Gate
Explore WoW64 architecture, its translation mechanisms, and potential vulnerabilities. Learn about reverse engineering techniques and bypassing security measures in Windows systems.
Malware Wars - DarkSide Strikes Back as BlackMatter
Explore the evolution of BlackMatter ransomware, its technical aspects, and its impact on the cybersecurity landscape. Gain insights into sophisticated ransomware operators and their tactics.
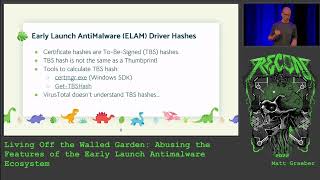
Living Off the Walled Garden
Explore Windows security vulnerabilities in ELAM and PPL, revealing how overly-permissive rules can be exploited for malware protection and code execution, hampering detection efforts.
OopsSec - The Bad, the Worst, and the Ugly of APT
Unveiling critical mistakes in APT campaigns across global threat actors, revealing advanced TTPs, and exploring real-time monitoring of sophisticated attacks. Insights on improving organizational defense against evolving threats.
Linux Vulnerabilities, Windows Exploits - Escalating Privileges with WSL
Explore WSL vulnerabilities and Windows kernel exploitation techniques. Learn about reverse engineering, syscall manipulation, and bypassing modern anti-exploitation defenses to achieve privilege escalation.
The Last Generic Win32K KASLR Defeat in Windows
Detailed exploration of Windows kernel security, focusing on KASLR defeats, heap vulnerabilities, and recent changes in RS4. Insights into potential exploits and current Windows KASLR state.
Smartphones Insecurity
Comprehensive analysis of smartphone vulnerabilities, exploring security flaws and potential exploits in mobile platforms. Insights from experienced security researchers on reverse engineering and exploit development.
Windows 10 Security Improvements
Explore Windows 10 security enhancements with experts Evan Pena and Christopher Truncer, covering latest improvements and their impact on enterprise defense strategies.
Abusing Privileged File Operations on Windows
Explore techniques for exploiting privileged file operations in Windows systems, uncovering potential vulnerabilities and security risks.
Subverting Trust in Windows
Explore techniques for manipulating Windows trust mechanisms, including code signing and execution policies, to bypass security controls and elevate privileges.
Honey I Just Put The Hospital On A Ventilator
Explore DICOM file vulnerabilities in healthcare and learn about an entropy-based detection technique to identify malicious files, with demonstrations of attacks and protective solutions for Linux and Windows.
Using Ancient Math to Speed Up Security Assessments of Windows Executables
Discover how to accelerate Windows executable security assessments using Euclidean Distance and Bayes Theorem, enabling rapid triage and efficient risk reduction in regulated environments.
Disrupting the Kill Chain
Comprehensive defense strategy for Windows environments, leveraging native Microsoft tools to disrupt cyber-attack kill chains. Covers detection, response, and automated remediation across various attack stages.

IBM - Trusteer Rapport - Does IBM Intentionally Backdoor Machines?
Investigates potential security concerns with IBM/Trusteer Rapport software, examining its code execution speed, system access, and implications for user privacy and system integrity.
Breaking Badge
Explore badge hacking techniques, including card reader software, reading/writing cards, and security encryption, with practical insights and a Python script demonstration.
Adversary Emulation on Windows - DefCamp - 2021
Explore advanced adversary emulation techniques for Windows systems, focusing on penetration testing, red teaming, and the MITRE framework to enhance cybersecurity defenses.
Abusing Bash for Windows
Explore techniques for exploiting Bash on Windows, including remote shells, password extraction, and AppLocker bypasses. Learn about security implications and forensic considerations.
Sneaking Past Device Guard - Philip Tsukerman - Hack in Paris - 2019
Explore techniques to bypass Windows 10's Device Guard, including VBA, trusted documents, and alternative execution vectors. Dive into internals of scripting engines and host processes.
Reasons to Stay Excited About Microsoft Endpoint Manager
Discover the latest updates in Microsoft Endpoint Manager across Windows, Apple, and Android platforms, including Cloud Configuration, frontline worker solutions, and enhanced security features.