So You Performed A Forest Recovery - How Do You Reconnect Your AD Again With Azure AD
Explore reconnecting Active Directory with Azure AD after forest recovery, addressing challenges and best practices for seamless integration in hybrid environments.
Walking Your Dog in Multiple Forests - Breaking AD Trust Boundaries through Kerberos Vulnerabilities
Explore Kerberos vulnerabilities in Active Directory forest trusts, revealing how attackers can breach trust boundaries in enterprise environments with multiple AD forests.
Exploiting Windows Hello for Business
Uncover vulnerabilities in Windows Hello for Business and learn to scan and secure corporate environments with a new toolset for enhanced Active Directory visibility.
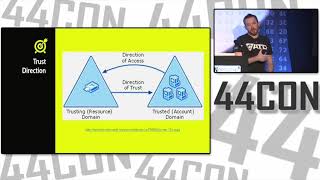
Trusts You Might Have Missed
Demystifying domain trusts: Enumeration, visualization, and exploitation techniques for red teams. Learn to leverage trust relationships for domain takeover without exploits.
Detecting the Elusive Active Directory Threat Hunting
Learn advanced techniques for detecting and hunting threats in Active Directory environments from security expert Sean Metcalf.
Pass the Hash and Other Credential Theft - Reuse - Mitigating Risk
Explore Pass the Hash attacks and Microsoft's recommended mitigations, including credential theft prevention, authentication policies, and platform changes for enhanced cybersecurity.
Null Sessions, MSRPC, and Windows 2000
Explore Windows 2000 security vulnerabilities, focusing on Null Sessions and MSRPC. Learn about potential risks and effective mitigation strategies for system administrators and security professionals.
Defending Windows 2000 on the Internet
Explore strategies for securing Windows 2000 systems on the internet, covering architecture, configurations, and best practices to defend against common attacks and vulnerabilities.
Active Directory and Group Policy
Explore Active Directory and Group Policy fundamentals, best practices, and advanced techniques for efficient network management and security in Windows environments.
Can a Windows Server 2003 Terminal Server Be Bulletproofed?
Explore securing Windows Server 2003 Terminal Services, covering new features, security changes, and best practices for enhanced protection and user management.
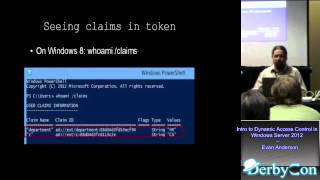
Intro to Dynamic Access Control in Windows Server 2012
Explore Dynamic Access Control in Windows Server 2012, covering components, classification, expressions, claims, policies, and Kerberos for enhanced security and resource management.
STRC - The Security Training and Research Cloud
Explore cloud-based cybersecurity training and research with STRC, covering defense, networking, data centers, automation, and practical labs for skill development.
Memory Forensics with Hyper V Virtual Machines
Explore memory forensics techniques for Hyper-V virtual machines, enhancing your ability to investigate and analyze digital evidence in virtualized environments.
A Year in the Empire
Explore Empire's evolution, new features, and design decisions in this comprehensive overview of the popular post-exploitation framework's development and community impact.
Top 10 Mistakes Made in Active Directory That Can Lead to Being Compromised
Explore common Active Directory vulnerabilities and learn how to prevent security breaches in your network infrastructure. Gain insights to strengthen your organization's defenses.
Securing Windows with Group Policy
Comprehensive guide to enhancing Windows security using Group Policy, covering essential techniques and best practices for system administrators and IT professionals.
Here Be Dragons - The Unexplored Land of Active Directory ACLs
Explore the uncharted territory of Active Directory ACLs, uncovering hidden vulnerabilities and advanced attack techniques in Windows environments.
Adding Simulated Users to Your Pentesting Lab with PowerShell
Learn to enhance your pentesting lab by creating simulated users with PowerShell, improving realism and complexity for more effective security testing and analysis.
Active Directory Security - The Journey
Explore Active Directory security challenges and solutions with expert Sean Metcalf, covering essential strategies for protecting enterprise networks and data.
Securing Windows with Group Policy
Explore Windows security through Group Policy, covering restricted groups, user management, privileges, and process mitigation. Learn practical techniques for enhancing system protection.
Invoke EmpireHound - Merging BloodHound Empire for Enhanced Red Team Workflow
Explore advanced red team techniques by merging BloodHound and Empire for enhanced workflow and more effective penetration testing strategies.