Hacking Web Apps
Learn techniques for identifying and exploiting web application vulnerabilities, focusing on practical methods to enhance security testing skills.
Social Engineering Toolkit
Learn advanced social engineering techniques, including credential harvesting, browser exploits, and spearphishing, using the Social Engineering Toolkit for ethical hacking and cybersecurity.
Hashview - A New Tool Aimed to Improve Your Password Cracking Endeavors
Explore Hashview, a tool for enhancing password cracking efficiency. Learn setup, user management, job creation, analytics, and future developments in distributed cracking.
Need More Sleep - REST Could Help Drew Branch
Explore REST APIs, their classification, testing methods, and security considerations. Learn about status codes, data formats, and tools like Postman and Burp Suite for API development and protection.
Intro to Linux - Part 1
Learn Linux basics: software center, internet setup, Ruby installation, file management, password changes, and web server configuration.
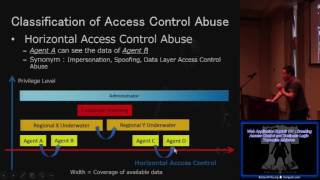
Web Application Exploit 101 - Breaking Access Control and Business Logic
Learn to exploit web application vulnerabilities by breaking access control and business logic, focusing on practical techniques for identifying and exploiting security flaws.
OPSEC for the Security Practitioner
Explore OPSEC strategies for security professionals, covering credit monitoring, attack surface reduction, identity protection, and personal security measures.
OWASP Top 10 - Hacking Web Applications with Burp Suite
Learn to exploit web application vulnerabilities using Burp Suite, focusing on the OWASP Top 10 security risks. Enhance your ethical hacking skills and improve web security knowledge.
Choose Django for Secure Web Development
Learn why Django excels in secure web development, covering key security features and best practices to protect against common vulnerabilities and threats.

Active Defense for Web Apps
Explore active defense strategies for web applications, focusing on innovative techniques to protect against cyber threats and enhance overall security posture.
Extending Burp
Explore techniques for enhancing Burp Suite's functionality through extensions, improving web application security testing capabilities and efficiency.
Metasploit Townhall
Explore Metasploit's latest developments, including Railgun, packet encryption, and REST API, with insights from experts on scalability, automation, and new database models.
Learning from InfoSec Fails
Learn from InfoSec failures to improve vulnerability management, DLP, web app security, and more. Explore key topics like pattern-based protection, IoT security, and the balance between security and compliance.
A Reporter's Look at Open Source Intelligence
Explore open-source intelligence techniques for investigative reporting, including browser extensions, search strategies, and accessing public records to uncover valuable information.
Embedding Security in Embedded Systems
Explore embedded system security challenges in IoT devices, from cameras to smart buildings. Learn about vulnerabilities, coordinated disclosure, and best practices for securing interconnected systems.
Modern Web Application Security
Learn modern web application security techniques and best practices to protect against common vulnerabilities and emerging threats.
Adding Pentest Sauce to Your Vulnerability Management Recipe
Enhance vulnerability management with pentesting techniques. Learn to identify weak spots, understand attacker perspectives, and implement effective security measures beyond basic scanning.
Security and Networking Dual Purpose Tools
Explore dual-purpose security and networking tools, including Zipmap, Web Servers, Firewalls, and Network Devices. Learn about network history, traffic analysis, and scanning techniques.
Lessons Learned from a OWASP Top 10 Datacall
Explore insights from OWASP Top 10 Datacall, covering attribution, tools vs. humans, tech complexity, survey results, and vulnerability patterns for improved application security.
Adding Simulated Users to Your Pentesting Lab with PowerShell
Learn to enhance your pentesting lab by creating simulated users with PowerShell, improving realism and effectiveness in security testing environments.
Automating Web App Security in AWS
Discover automated security strategies for web applications in AWS, focusing on efficient protection and compliance measures for cloud-based infrastructures.