Building Distributed Applications with Event Driven Architecture
Learn to build scalable, distributed applications using event-driven architecture. Explore integration patterns, decoupling strategies, and idempotency techniques to create resilient systems with AWS messaging services.
What's New in C# - Exciting New Features in C# 9, 10 and 11
Explore exciting new features in C# 9, 10, and 11, including nullable reference types, pattern matching, record types, and more. Learn how these changes improve code quality and efficiency.
Non-English Programming with Hedy
Explore Hedy, a gradual programming language designed for multilingual learning. Discover its unique levels, syntax evolution, and the challenges of creating an inclusive coding environment for diverse languages and cultures.
The Dirty Little Secrets They Didn't Teach You In Pentesting Class
Uncover advanced penetration testing techniques, from domain admin strategies to post-exploitation tactics. Learn covert persistence methods and efficient data discovery for enhanced cybersecurity assessments.
The Hidden XSS - Attacking the Desktop
Explore hidden XSS vulnerabilities in desktop applications, focusing on Skype, WebOS, and Android. Learn attack techniques and implications for security.
Javascript Deobfuscation
Learn techniques to decode obfuscated JavaScript, enhancing your ability to analyze and understand potentially malicious code for improved web security and threat detection.

Look Ma No Exploits - The Recon-ng Framework
Comprehensive framework for reconnaissance in cybersecurity, covering host harvesting, data manipulation, and social engineering techniques with practical demonstrations.
Appsec TLDR
Explore web application security essentials, including browser proxies, HTTP requests, cookies, and common vulnerabilities like XSS and SQL injection. Learn attacker mentality and defense strategies.
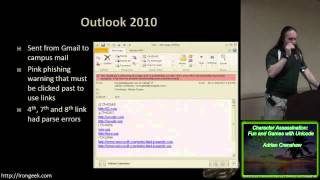
Character Assassination Fun and Games with Unicode - Adrian Crenshaw
Explore Unicode's potential for character obfuscation, homograph attacks, and steganography in cybersecurity. Learn about encoding, browser protections, and real-world implications.
RESTful Web Services
Learn to secure RESTful web services by exploring test methods, authentication, responses, and common vulnerabilities. Gain practical insights for robust API protection.
HTML 5 Security
Explore HTML5 security vulnerabilities and best practices with Justin Klein Keane. Learn about emerging threats and defensive strategies for modern web applications.
How to Become an Unwitting Accomplice in a Phishing Attack
Explore phishing attack techniques, consequences, and prevention strategies through real-world examples and forensic analysis. Learn to identify vulnerabilities and protect against unwitting involvement in cybercrime.
HTTPS Now You See Me
Explore HTTPS encryption, its vulnerabilities, and methods to intercept secure communications in this informative cybersecurity presentation.
OWASP Top 10 of 2013 - It's Still a Thing and We're Still Not Getting It
Explore OWASP Top 10 vulnerabilities from 2013, their ongoing relevance, and why organizations struggle to address them effectively in web application security.
Burp for All Languages
Learn to leverage Burp Suite for web application security testing across various programming languages with expert insights and practical techniques.
Exploiting Browsers Like A Boss
Learn advanced browser exploitation techniques and strategies for identifying vulnerabilities in web applications from cybersecurity expert Bryce Kunz.
NoSQL Injections - Moving Beyond or 11
Explore advanced NoSQL injection techniques and defense strategies with expert Matt Bromiley, moving beyond basic vulnerabilities to enhance database security.
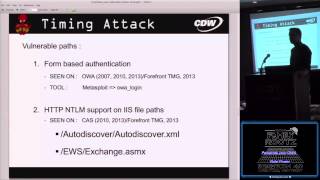
Penetrate Your OWA
Explore techniques for penetrating Outlook Web Access (OWA) and enhancing your security testing capabilities in this informative DerbyCon 4 presentation.

CMS Hacking Tricks
Explore advanced techniques for exploiting content management systems, uncovering vulnerabilities, and enhancing web application security.
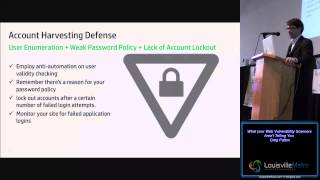
What Your Web Vulnerability Scanners Aren't Telling You
Explore common web vulnerabilities often missed by automated scanners, including logic flaws, authentication issues, and access control problems. Learn defensive strategies for better web security.
OWASP Mobile Top Ten - Why They Matter and What We Can Do
Explore OWASP Mobile Top Ten vulnerabilities, their significance, and strategies for mitigation. Learn about transport layer protection, threat modeling, and best practices for mobile app security.