Making Sense of Maps
Explore the fascinating world of mental maps and their impact on real-world cartography, using Dublin's bus system as a case study for improved map design.
The New Page of Injections Book - Memcached Injections
Explore memcached injection vulnerabilities across popular web platforms, learning attack techniques, potential impacts, and post-exploitation strategies for improved application security.
Call to Arms - A Tale of the Weaknesses of Current Client-Side XSS Filtering
Uncovers 17 flaws in Chrome's XSS Auditor, demonstrating bypasses and presenting a tool for generating attacks. Analyzes filter effectiveness against real-world vulnerabilities, proposing future improvements.
How to Leak a 100-Million-Node Social Graph in Just One Week
Exploración de vulnerabilidades en OAuth 2.0 para redes sociales, demostrando cómo la suplantación de aplicaciones puede llevar a la filtración masiva de datos de usuarios y gráficos sociales.
SVG - Exploiting Browsers without Image Parsing Bugs
Explore SVG's hidden potential for web exploitation, including JavaScript execution and external resource imports, challenging traditional browser security assumptions.
The Defense Rests - Automation and APIs for Improving Security
Explore automation and APIs for enhancing security through centralized management, testing, and evidence-driven approaches. Learn to leverage open-source tools and protocols for efficient vulnerability detection and faster recovery.
Libinjection - A C Library for SQLI Detection and Generation Through Lexical Analysis
Innovative C library for SQL injection detection using lexical analysis, offering high precision and accuracy. Trained on real attacks, it categorizes threats and provides templates for new attack detection.
Attacking Web Services - Next Generation of Vulnerable Enterprise Apps
Explore vulnerabilities in enterprise web services and learn advanced techniques for identifying and exploiting security flaws in next-generation applications.
Injection Flaws - Stop Validating Your Input
Explore injection flaws and learn why input validation alone is insufficient for security. Discover effective strategies to protect against these vulnerabilities in web applications.
Confessions of a WAF Developer - Protocol-Level Evasion of Web App Firewalls
Explores protocol-level evasion techniques for bypassing web application firewalls, focusing on vulnerabilities in virtual patches and demonstrating real-world examples and countermeasures.
Next Generation Clickjacking
Explore advanced clickjacking techniques, including data injection and extraction, cross-browser vulnerabilities, and a new tool for creating multi-step attacks on web applications.
Invisibility Purge - Unmasking the Dormant Events of Invisible Web Controls
Unmasking dormant events in server web controls through refined methodology and new tool, bypassing security measures to exploit hidden application features.
Hardening Windows 8 Apps for the Windows Store
Explore security considerations for Windows 8 Store apps, covering HTML5, backend services, cloud computing, and WinRT to ensure robust and privacy-focused mobile development.
Harnessing GPUs - Building Better Browser Based Botnets
Explore browser-based botnets using GPUs for powerful computations. Learn about XSS, HTML5, and WebGL techniques to create efficient, cross-platform botnets capable of breaking strong encryption and impacting cybersecurity.
Burglar Alarms and Booby Traps
Discover innovative network defense strategies using insider knowledge. Learn fun tricks to build effective intrusion detection systems for networks, websites, and firewalls.
Announcing OWASP Guide to Securing Web Applications & Services 2.0
Comprehensive guide to securing web applications and services, covering best practices, vulnerabilities, and mitigation strategies for developers and security professionals.
ModSecurity as Universal Cross-Platform Web Protection Tool
Explore ModSecurity's evolution into a cross-platform WAF, its early attack detection capabilities, and its use of OWASP Core Rule Set for protecting Apache, IIS, and nginx servers.
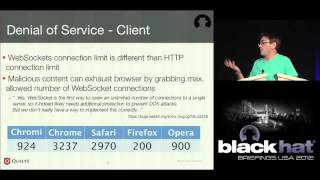
Hacking with WebSockets
Explore WebSocket vulnerabilities, privacy implications, and security risks. Learn to deploy WebSockets securely and use them in hacking frameworks. Gain insights into HTML5 security challenges.
HTML5 Top 10 Threats - Stealth Attacks & Silent Exploits
Explores top 10 HTML5 security threats, including CORS attacks, clickjacking, XSS, web storage vulnerabilities, and more. Demonstrates real-life examples and discusses defense strategies against emerging attack vectors.
Diving Into IE 10’s Enhanced Protected Mode Sandbox
Explore IE 10's Enhanced Protected Mode Sandbox, its security features, and potential vulnerabilities in this in-depth technical analysis.
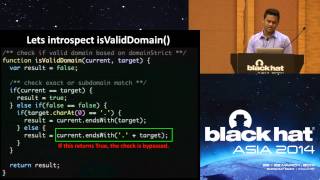
JS Suicide - Using JavaScript Security Features to Kill JS Security
Explore JavaScript security features and their potential vulnerabilities, uncovering how these protective measures can be exploited to compromise web application security.