Be Ready for BeyondCorp - Enterprise Identity, Perimeters and Your Application
Explore BeyondCorp's enterprise security model, focusing on user and device authentication, access control, and implementation in open-source web applications using tools like SAML and Django.
Frictionless Security
Explore automated, non-intrusive security integration into company infrastructure. Learn from successes, failures, and future improvements in implementing frictionless security programs.

Security Module for PHP7 - Killing Bugclasses and Virtual-Patching the Rest
Explore Snuffleupagus, a new PHP security module for killing bug classes and virtual-patching vulnerabilities without modifying application code. Learn its features and implementation.
DevOps, CI, APIs, Oh My! - Security Gone Agile
Explore agile security practices for rapid deployment in DevOps environments, covering infrastructure, APIs, and code security to keep pace with modern development cycles.
User Auth for Winners - How to Get It Right the First Time
Learn best practices for secure user authentication, from account creation to password reset, and implement robust systems to prevent breaches. Gain insights on REST-based platforms, authentication tokens, and scaling strategies.
Stupid Webappsec Tricks
Discover simple yet effective techniques for detecting vulnerabilities and making malicious activity economically infeasible in web application security.
HTTPS Can Byte Me
Explore HTTPS vulnerabilities and security implications with industry experts, gaining insights into potential risks and mitigation strategies for secure web communication.
Testing Modern Applications with Hackazon
Learn to test modern web applications using Hackazon, focusing on e-commerce functions, AJAX workflows, and RESTful APIs. Discover hidden vulnerabilities and systematic testing approaches.
What Do You Mean My Security Tools Don't Work on APIs?
Explores techniques for securing APIs and modern service-based web applications, discussing challenges and innovative approaches like security instrumentation for vulnerability identification and protection.
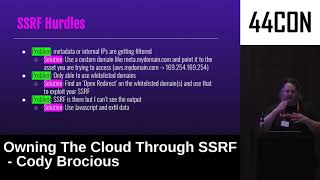
Owning the Cloud Through SSRF
Explore cloud security vulnerabilities through SSRF attacks, focusing on metadata exploitation, CVE examples, and advanced techniques like DNS rebinding for comprehensive cloud protection.
Ghosts of XSS Past, Present and Future
Comprehensive exploration of Cross-Site Scripting vulnerabilities, examining historical trends, current threats, and future challenges in web application security.
Beautiful Payment Systems with OAuth
Explore secure and elegant payment system design using OAuth, focusing on best practices and implementation strategies for developers.
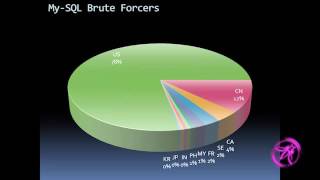
Keeping Up with the Web Application Security
Explore strategies for maintaining robust web application security in an ever-evolving digital landscape. Learn from industry experts about current threats and effective countermeasures.
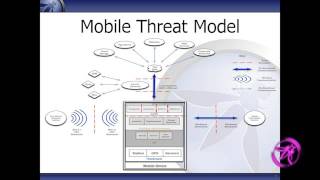
OWASP Top 10 Mobile Risks
Explore the OWASP Top 10 Mobile Risks, covering threat modeling, data storage, server controls, and more. Learn prevention tips and best practices for mobile app security.
Next Gen Web Attacks - HTML 5, DOM L3 and XHR L2
Explore cutting-edge web security threats and defense strategies focusing on HTML5, DOM Level 3, and XMLHttpRequest Level 2 technologies with expert Shreeraj Shah.
Warning Ahead - Security Storms are Brewing in Your JavaScript
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 security concerns. Learn about emerging threats and their impact on enterprise security.
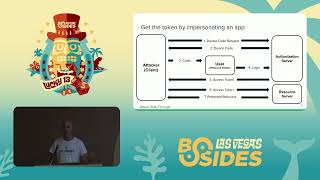
Oauth Third Party Not Departing
Explore OAuth vulnerabilities and security risks in third-party integrations, focusing on potential exploits and mitigation strategies for robust authentication systems.
Making Your Website Vulnerable for Fun and Security Awareness
Learn to intentionally create website vulnerabilities for security awareness and testing, enhancing your understanding of web application security risks and defenses.
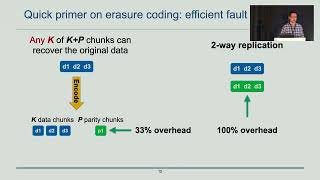
C2DN - How to Harness Erasure Codes at the Edge for Efficient Content Delivery
Explore innovative CDN design using erasure coding for improved performance, efficiency, and load balancing in content delivery networks.
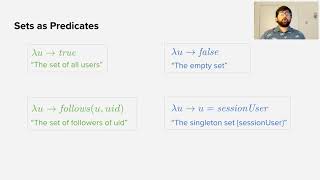
STORM - Refinement Types for Secure Web Applications
STORM: A web framework for building MVC applications with compile-time enforcement of security policies, reducing trusted code to under 1% and providing static security enforcement with minimal overhead.
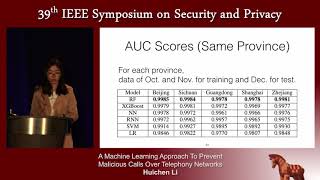
A Machine Learning Approach to Prevent Malicious Calls Over Telephony Networks
Innovative machine learning solution to combat telephony spam and scams, using user-tagged call logs to design effective features for predicting and blocking malicious calls with high accuracy.