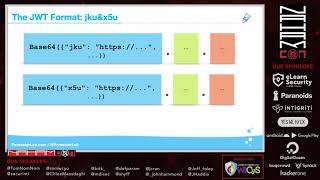
JWT JKU and X5U Equals Love
Explore JWT vulnerabilities related to jku and x5u headers, understanding potential security risks and exploitation techniques in web applications.
TruffleHog Chrome Extension - Open CORS in SAAS API's Lead to Leaky Keys
Discover API keys hidden in web pages with the open-source TruffleHog Chrome extension. Learn how to use this tool and explore real-world examples of exposed keys in SaaS APIs with open CORS.
How to Create Your Own Metaverse in WEB3
Explore the potential of an open, accessible Metaverse with step-by-step guidance on entering this innovative digital realm, emphasizing the importance of data, AI, and computer literacy for future generations.
Dashlet - Taming Swipe Uncertainty for Robust Short Video Streaming
Innovative system for improving short video streaming quality by predicting user swipe patterns and pre-buffering content, outperforming TikTok while reducing wasted data downloads.

HTTP/2 & QUIC - Teaching Good Protocols to Do Bad Things
Explore multiplexing attacks in QUIC and HTTP/2 protocols, their impact on network security, and defense strategies against potential threats in modern web technologies.
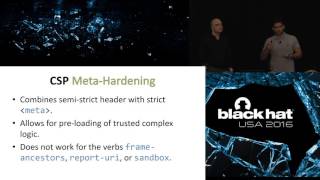
Abusing Bleeding Edge Web Standards for Appsec Glory
Explore risks and mitigation strategies for modern web security standards like SRI, CSP, and HPKP. Learn about implementation challenges, trade-offs, and potential exploits in legacy applications.
What's the DFIRence for ICS?
Explore digital forensics for industrial control systems, focusing on embedded devices in critical infrastructure. Learn data collection and analysis techniques for RTUs in electric substations.
BadWPAD
Explores WPAD protocol vulnerabilities through experiments, revealing widespread risks in networks and DNS. Presents surprising findings and discusses implications for cybersecurity.
Timing Attacks Have Never Been So Practical - Advanced Cross-Site Search Attacks
Explore advanced cross-site search attacks, including browser-based and second-order techniques, to extract sensitive data from web services through timing side-channel vulnerabilities.
Web Application Firewalls - Analysis of Detection Logic
Explores detection logic in Web Application Firewalls, focusing on regular expressions. Analyzes security flaws in popular WAFs and introduces tools for identifying vulnerabilities in regex patterns.
Intra-Process Memory Protection for Applications on ARM and X86 - Leveraging the ELF ABI
Explore intra-process memory protection techniques for ARM and X86 architectures using ELF ABI. Learn about ELFbac system implementation, policy enforcement, and practical applications in software security.
Ways to Die in Mobile OAuth
Comprehensive analysis of OAuth vulnerabilities in mobile apps, revealing widespread implementation flaws and security risks. Offers insights for developers to enhance mobile OAuth security.

Viral Video - Exploiting SSRF in Video Converters
Exploiting SSRF vulnerabilities in video converters using HLS playlists, potentially leading to critical security breaches in cloud-based services. Includes demonstration of attacks on major platforms.
Security Through Design - Making Security Better by Designing for People
Explore user-centered design methods to create more effective and user-friendly security processes, tools, and communication strategies, improving corporate productivity and security.

Make Content Creation A Career
Discover how two content creators turned their passion into successful careers, overcoming challenges and building multi-million view channels in the digital space.

WebAuthn, Yubikeys, and You - What We Wish We Knew Before Rolling Out WebAuthn for Internal Use
Insights from Discord's implementation of WebAuthn and Yubikeys for enhanced internal security. Learn about challenges, best practices, and lessons learned in deploying FIDO2/WebAuthn as a superior MFA solution.
Cross Site Scripting 101
Beginner-friendly introduction to Cross-Site Scripting (XSS) in web application security, including an overview and walkthrough of a basic XSS challenge from BSidesSF CTF.
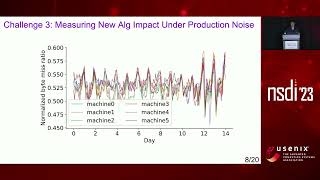
HALP - Heuristic Aided Learned Preference Eviction Policy for YouTube Content Delivery Network
Explore HALP, a machine learning-based caching algorithm for YouTube's CDN that improves efficiency, reduces byte miss rates, and addresses deployment challenges in large-scale production environments.
Embedding Web Apps in MITMProxy Scripts
Explore techniques for embedding web applications within MITMProxy scripts to enhance network traffic analysis and manipulation capabilities.
DNS Hardening - Proactive Network Security Using F5 iRules and Open Source Analysis Tools
Explore proactive DNS security using F5 iRules and open-source tools. Learn to detect and mitigate threats like DGAs, malformed packets, and DNS DDoS attacks for enhanced network protection.
Beyond Passwords - How WebAuthn Actually Works
Explore WebAuthn as a secure alternative to passwords, diving into its implementation, hardware token usage, and underlying cryptography for enhanced web authentication.