Preventing Authentication Bypass - A Tale of Two Researchers
Explore techniques for identifying authentication bypass vulnerabilities, learn effective researcher-company partnerships, and discover secure coding practices to prevent similar flaws in web applications.
HTTP Desync Attacks - Smashing into the Cell Next Door
Explore techniques for HTTP request splicing, enabling remote attackers to manipulate web infrastructure, exploit visitors, and breach system isolation. Learn detection, case studies, and mitigation strategies.
Talking Behind Your Back - Attacks and Countermeasures of Ultrasonic Cross-Device Tracking
Explore ultrasonic cross-device tracking: its marketing potential, privacy implications, and vulnerabilities. Learn about attacks, countermeasures, and the future of this emerging technology.
Command Injection in F5 iRules
Explore command injection vulnerabilities in F5 iRules, focusing on syntax, exploitation techniques, and security implications for BigIP F5 products used in high-performance web traffic routing.
Under the SEA - A Look at the Syrian Electronic Army's Mobile Tooling
Explore the Syrian Electronic Army's mobile surveillance tools, focusing on SilverHawk, its capabilities, and deployment methods in this cybersecurity analysis.
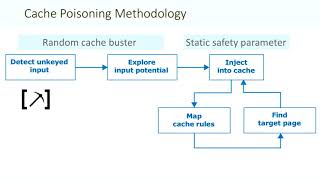
Practical Web Cache Poisoning - Redefining 'Unexploitable'
Explore web cache poisoning techniques to compromise websites by exploiting caches and content delivery networks, turning them into exploit delivery systems targeting unsuspecting visitors.
Exploiting Android Messengers with WebRTC
Explore WebRTC vulnerabilities in Android messaging apps, their exploitation, and mitigation strategies. Learn about security research techniques and mobile application security.
Introducing the ASVS 4.0
Explore OWASP ASVS 4.0 updates, new controls, and industry applications. Learn about modern web app security, architecture changes, and a novel attack technique.
Injecting Security Into Web Apps With Runtime Patching And Context Learning
Explore advanced web application security techniques using Runtime Application Self Protection (RASP) to prevent code injections and other vulnerabilities through dynamic analysis and patching.
Engineering Better Security at Facebook
Explore Facebook's approach to enhancing security through developer-focused tools and practices, addressing vulnerability prevention and detection in large-scale software development.
ECMA Script 6 from an Attacker's Perspective
Explore ECMA Script 6 from a security perspective, covering new language features, potential attack vectors, and strategies to mitigate risks in modern web browsers.
Hacking Your Cable TV Network
Explore cable TV network vulnerabilities and attacks, including analog and digital systems, IRD decoders, and management servers. Learn techniques for hijacking set-top boxes and remote shutdown.
Hunting for Memory Resident Malware
Explore techniques for detecting memory-resident malware, including API analysis, post-breach detection, and CLR hooking. Learn why memory hunting is crucial in cybersecurity.
Red Team Level Over 9000 - Fusing the Power of NET With a Scripting Language of Your Choosing
Explore advanced red teaming techniques by combining .NET with scripting languages, covering concepts like IronPython, WebAssembly, and PowerShell for enhanced offensive capabilities.
Old Tools New Tricks - Hacking WebSockets
Explore WebSocket hacking techniques, from basic concepts to advanced exploits, using various tools and methods for secure testing and vulnerability assessment.
Offensive Browser Extension Development
Learn to develop and analyze browser extensions, exploring potential security risks and malicious behaviors in web store submissions and installations.
Introduction to the OWASP ModSecurity Core Rule Set
Learn about OWASP ModSecurity Core Rule Set, a powerful open-source web application firewall. Discover key features like paranoia levels and anomaly scoring, and see its effectiveness in protecting against various attacks.
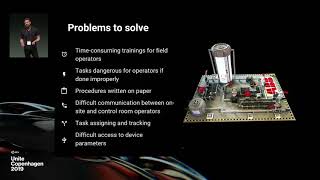
How ABB Shapes the Future with Microsoft HoloLens and Unity
Explore how ABB leverages Microsoft HoloLens and Unity to overcome AR challenges, design effective UI, and shape the future of industry through innovative augmented reality applications.
Modernizing the Unity Editor UI
Explore Unity's user-centric approach to modernizing the Editor UI, including design principles, development process, and addressing user feedback.
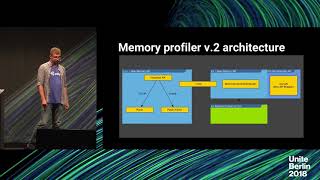
Memory Profiler - The Tool for Troubleshooting Memory-Related Issues
Explore Unity's Memory Profiler for efficient troubleshooting of memory-related issues, including leak detection, allocation analysis, and in-depth memory inspection.
UIForia - User Interface Euphoria
Discover UIForia, a powerful UI engine for Unity games. Learn about fast data binding, efficient layouts, hot reloading, and performance optimization for seamless user interfaces.