Service Workers vs Corporate Firewalls
Explore how service workers can be exploited to bypass corporate firewalls, potentially compromising network security. Learn about this innovative attack vector and its implications.

Bahn API Chaos
Einblick in die APIs der Deutschen Bahn: Struktur, Einheitlichkeit und Anwendung am Beispiel von marudor.de. Analyse der Datengrundlage und ihrer Herausforderungen.
Helping WordPress Users Build Climate-Friendly Websites
Learn to create environmentally sustainable WordPress sites with greenerWP's tools, including a scanner, plugin, theme, and guides for solar-powered setups.
Nothing New About XSS in Impress.js
Demonstrating XSS vulnerabilities in impress.js presentations, showcasing innovative features like a 3D cockpit view and dynamic slide content manipulation for enhanced interactivity and visual appeal.
AppSec’s Future and the Rise of the Chief Product Security Officer
Explore the evolution of application security and the emerging role of Chief Product Security Officers in addressing modern digital infrastructure challenges.
Next-Gen IoT Botnets - Bad Implementations of Good Cloud Platforms
Explore security vulnerabilities in IoT cloud platforms, including authentication bypasses and remote code execution. Learn about the risks of poor implementations and their widespread impact on connected devices.
Secure Sandboxing in a Post-Spectre World
Explore WebAssembly and Lucet for secure edge computing, offering efficient multi-tenant isolation of native code with lower resource and performance costs than competing approaches.
HTTP Security Headers - A Technology History Through Scar Tissue
Explore HTTP security headers, their evolution, and best practices. Learn to leverage browser-built security controls, with a focus on implementing effective content-security-policy for enhanced web application protection.
Strangeways, Here We Come
Explore cloud migration for startups: benefits, risks, and security best practices. Learn about AWS, cloud architecture, and strategies for a successful transition from on-premises to cloud-based solutions.
Caught My WebApp Cheating on Me
Exploring techniques to detect and prevent client-side injections and tampering in web applications, ensuring integrity and security of code executed in the browser.
Unraveling the Threat of Chrome Based Malware
Explore Chrome extension vulnerabilities, their potential for network compromise, and strategies for identifying and mitigating risks in enterprise environments.
What's New or Not in 2020 - Are We Making Progress on the Intractable Security Problems
Insightful keynote examining the progress and challenges in Information Security over the past decade, highlighting achievements and persistent issues facing professionals in the field.
Automating Web Application Bug Hunting
Discover techniques for automating web application vulnerability scanning to enhance bug bounty hunting and application security analysis efficiency.
Securing Online Identities with Simple, Secure, Open Standards
Explore the evolution of online identity security, from U2F to FIDO2, and learn how open standards are shaping the future of passwordless authentication across devices.
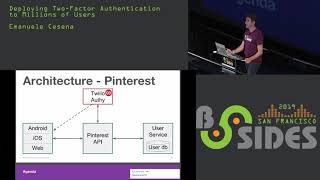
Deploying Two-Factor Authentication to Millions of Users
Comprehensive guide on implementing two-factor authentication for large-scale websites, covering design, architecture, and various methods like TOTP, push notifications, and FIDO security keys.
The Seven Most Dangerous New Attack Techniques, and What's Coming Next
Explore cutting-edge cybersecurity threats and defense strategies with experts from the Internet Storm Center, focusing on emerging attack techniques and future preparedness.
Dormant DOMination
Exploring JavaScript-based network scanning techniques to discover attack surfaces across different networks, including air-gapped systems, through dormant browser objects and existing web technologies.

WebAuthn - How to FIDO
Explore FIDO2 WebAuthn for phishing-resistant, passwordless authentication. Learn implementation strategies for stronger user protection on websites and applications.
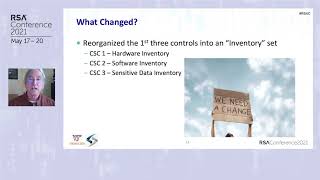
What's New with the CIS Controls v8
Explore key updates in CIS Controls v8, reflecting major changes in modern computing and infrastructure environments for enhanced cybersecurity practices.
Hook, Line and Sinker - Pillaging API Webhooks
Explore "Webhook Boomerang flaws" and learn how to exploit SSRF vulnerabilities in API webhooks, potentially compromising cloud credentials despite security measures.
The Power of Guardrails - How to Slash Your Risk of XSS in Half
Discover how secure code defaults can significantly reduce XSS vulnerabilities and elevate overall security. Learn strategies to implement effective guardrails and minimize recurring security risks.