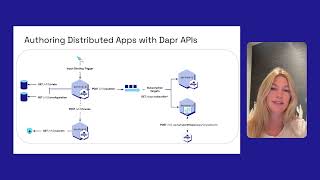
Dapr - The Ultimate Developer API for Authoring Microservices
Explore Dapr's developer API for efficient microservice creation, simplifying distributed application development and enhancing productivity in cloud-native environments.
What's New with Open Policy Agent Gatekeeper
Explore recent updates and advancements in Open Policy Agent Gatekeeper, enhancing Kubernetes security and policy enforcement capabilities.
VPython for Beginners - Widgets - Lesson 54
Learn to enhance VPython animations with interactive widgets like buttons and sliders, adding engagement and accessibility to your 3D visualizations.
OWASP Cheatsheets Project
Comprehensive guide to web application security best practices, covering key areas like input validation, authentication, and secure coding techniques.
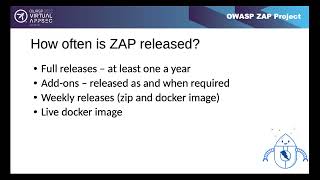
OWASP ZAP Project: Introduction to Web Application Security Testing
Learn to use OWASP ZAP, a powerful open-source web application security scanner. Discover its features, capabilities, and best practices for identifying vulnerabilities in web applications.
What's New in CRS4 - An Update from the OWASP CRS Project
Explore the latest updates and enhancements in CRS4, the OWASP Core Rule Set project, with insights on improved web application security and threat mitigation strategies.
15 Years of OWASP Top 10 - Has the Cloud Made a Difference?
Explore the evolution of web application security over 15 years, examining the impact of cloud computing on OWASP Top 10 vulnerabilities and current cybersecurity challenges.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Testability Patterns for Web Applications - A New OWASP Project
Explore testability patterns for web applications in this OWASP project presentation, focusing on enhancing security testing effectiveness and efficiency.
Squeezing the Last Drop Out of OWASP Juice Shop
Explore advanced hacking techniques and security challenges in this hands-on session with OWASP Juice Shop, led by its creator Bjoern Kimminich.
Server-Side Prototype Pollution: Detection and Exploitation Techniques - OWASP AppSec Dublin
Explore server-side prototype pollution vulnerabilities, detection techniques, and prevention strategies in web applications with security expert Gareth Heyes.
JavaScript Realms - The Blank Spot in Web Application Runtime Security
Explore JavaScript Realms and their impact on web application runtime security, uncovering potential vulnerabilities and mitigation strategies.
Removing Secrets to Make Mobile Apps More MASVS-Secure
Explore mobile app security, focusing on removing secrets and enhancing MASVS compliance. Learn defense strategies against various attacks and discover a resilient authentication architecture.
Defending Against New Phishing Attacks that Abuse OAuth Authorization Flows
Explore advanced techniques to protect against sophisticated phishing attacks exploiting OAuth authorization flows, enhancing your cybersecurity defenses.
JavaScript Obfuscation: It's All About the Packers
Explore JavaScript obfuscation techniques, focusing on packers and their impact on code security and readability in this informative OWASP presentation.
Securing an API Ecosystem with OAuth 2.0
Explore OAuth 2.0 implementation for robust API security in this comprehensive talk by Philippe De Ryck, covering best practices and ecosystem protection strategies.
OWASP Juice Shop Project
Explore web application security with OWASP's intentionally vulnerable Juice Shop, learning about common vulnerabilities and how to exploit and defend against them.
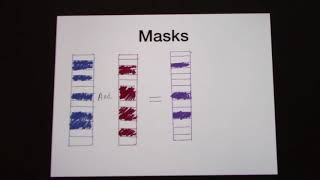
How I Learned to Stop Worrying and Love the Trait - Retrospective on Specs-RS
Explore how specs-rs uses traits to create a fast and simple API for Entity Component Systems in Rust, with insights on storage types, components, and systems.
Writing Node.js Modules in Rust Using Neon
Learn to create fast, safe Node.js modules using Rust and Neon bindings. Explore current capabilities, examples, challenges, and future prospects of integrating Rust with Node.js applications.
Embedding WebAssembly for Scripting in Rust Applications
Explore WebAssembly integration in Rust applications for efficient dynamic scripting, covering benefits, implementation, and practical demonstrations.
WebAssembly for the Rust of Us - Rust Hungary 2017
Explore WebAssembly's potential for Rust in web development. Learn how Rust's full support for WebAssembly opens new possibilities for creating efficient, powerful web applications.