Meddling Middlemen - Empirical Analysis of the Risks of Data-Saving Mobile Browsers
Empirical analysis of data-saving mobile browsers, exploring their effectiveness, impact on usability, and potential security risks. Examines proxy server configurations, privacy concerns, and proposes improved designs.
The State of the SameSite: Studying the Usage, Effectiveness, and Adequacy of SameSite Cookies
Explore SameSite cookies' usage, effectiveness, and adequacy in web security. Analyze adoption, functionality issues, CSRF threats, policy downgrades, and browser inconsistencies.
A Formal Security Analysis of the W3C Web Payment APIs - Attacks and Verification
Explore formal security analysis of W3C Web Payment APIs, including potential attacks and verification methods. Learn about browser models and gain insights into API security.
Docker for Pentesting & Bug Bounty Hunting
Explore Docker's potential for pentesting and bug bounty hunting. Learn to set up Kali Linux, OWASP Juice Shop, and Bug Bounty Toolkit, enhancing your cybersecurity skills and workflow efficiency.
Learn Computer Vision with Jetson Nano Using Python
Learn computer vision fundamentals and apply them to real-world projects using Jetson Nano. Develop skills in eye tracking, self-driving car simulation, and face recognition with hands-on experience.
GDPR Implications for Facebook Advertisers - Interview With Business Lawyer Suzanne Dibble
Expert insights on GDPR's impact on Facebook advertising, covering compliance requirements, consent rules, data protection, and legal implications for online businesses and marketers.
Learn Offensive JavaScript Today
Discover offensive JavaScript techniques including keylogging, data exfiltration, password theft, and CSRF bypass in this concise tutorial on exploiting web vulnerabilities.
How to Win Over Security Teams and Gain Influence as a Hacker
Insights from experienced hackers on effective strategies, tools, and etiquette for successful bug bounty hunting and building positive relationships with security teams.
Unique Mindset - Hacking Techniques and Favorite Findings
Explore zseano's unique hacking mindset through real-world examples, favorite findings, and insights on identifying critical vulnerabilities in web applications.
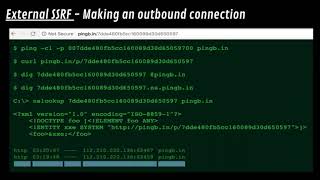
Server Side Request Forgery
Learn to identify, exploit, and mitigate Server-Side Request Forgery vulnerabilities. Covers external and internal SSRF, bypassing blacklists, and includes practical demonstrations and real-world examples.
LevelUp 0x04: Advanced Bug Bounty Techniques - Day 2
Explore advanced bug bounty techniques and strategies with industry experts in this comprehensive cybersecurity event focused on enhancing hacking skills and knowledge.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
Serverless Top 10 Vulnerabilities by Tal Melamed
Explore serverless security vulnerabilities, their impact, and prevention techniques. Learn how traditional threats evolve in serverless environments and discover best practices for securing cloud-native applications.
Hacking with Burp Suite for Bug Bounties - Tutorial 1
Learn essential Burp Suite techniques for bug bounty hunting, including setup and basic functionality, to enhance your web application security testing skills.
Hacking OAuth 2.0 for Fun and Profit
Discover high-impact vulnerabilities in OAuth 2.0 integrations. Learn attack techniques, methodologies, and case studies for token stealing, code stealing, CSRF, and token impersonation.
MarkDoom- How I Hacked Every Major IDE in 2 Weeks - Matt Austin, LevelUp 2017
Explore web hacking techniques used to exploit major IDEs and desktop applications, revealing high-severity vulnerabilities in popular development tools.
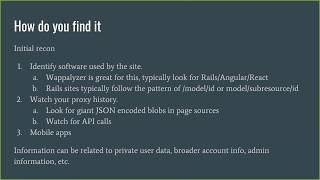
Hidden in Plain Site - Disclosing Information via Your APIs - Peter Yaworski, Bugcrowd's LevelUp 2017
Explore information disclosure vulnerabilities in APIs and HTML sources, focusing on Rails design patterns and front-end frameworks. Learn detection techniques and real-world examples.

Burp Hacks for Bounty Hunters
Discover personal Burp Suite techniques for effective bug bounty hunting, enhancing your web application security testing skills and increasing your chances of finding vulnerabilities.
Car Hacking Explained for Bug Hunters - Automotive Security Vulnerabilities and Methodologies
Explore automotive security vulnerabilities, from IoT to CAN bus hacking. Learn methodologies, attack surfaces, and bug prioritization for car hacking, covering infotainment systems, APIs, and mobile apps.
GSuite Security- Everyone Wants It but Not Everyone Gets It
Explore common GSuite misconfigurations, prevention strategies, and bug hunting techniques. Learn about private docs, Google Sites, API vulnerabilities, and more from an experienced bounty hunter.
Hacking, Content Creation, and API Security with TheXSSRat
Insightful discussion on hacking, content creation, and API security with TheXSSRat. Covers career paths, learning strategies, and practical tips for aspiring cybersecurity professionals.