
Web App Penetration Testing - CSRF (Cross Site Request Forgery)
Demonstración práctica de ataques CSRF en OWASP Juice Shop utilizando BurpSuite. Aprende a identificar y explotar vulnerabilidades de falsificación de peticiones entre sitios en aplicaciones web.
OWASP Juice Shop - SQL Injection
Learn to perform SQL injection on OWASP Juice Shop in this hands-on demonstration. Gain practical skills in identifying and exploiting web application vulnerabilities to enhance your cybersecurity knowledge.
Exploiting Race Conditions - Black Belt Pentesting and Bug Hunting
Explore advanced web attack techniques focusing on exploiting race conditions, enhancing your penetration testing and bug hunting skills for full-stack exploitation.
Scanning at Scale with OWASP ZAP - Technical Challenges and Improvements
Explore techniques for scaling OWASP ZAP scans, including technical challenges, modifications, and improvements. Learn from Probely's experience as active ZAP contributors.
Using API Specifications to Attack APIs
Explore API security vulnerabilities, breaches, and scanning tools. Learn to leverage API specifications for both protection and potential exploitation in this comprehensive overview.
Web Application Security: The Secret to Hack-Proof Apps - SQL Injection - Part 2
Discover step-by-step methods to secure web applications from SQL injection threats. Learn to identify vulnerabilities, exploit techniques, and implement effective prevention strategies for robust security.

Securing Web Applications: Integrating OWASP with Burp Suite
Integrate OWASP tools with Burp Suite to identify vulnerabilities, conduct security assessments, and implement effective mitigation strategies for web applications.
Exploiting Client-Side Path Traversal - CSRF Is Dead, Long Live CSRF
Uncover advanced techniques for exploiting client-side path traversal vulnerabilities, exploring the evolution of CSRF attacks and their modern implications for web security.
Will Machine Learning Replace the WAF?
Explore the potential of machine learning to revolutionize web application firewalls, examining its capabilities, limitations, and impact on cybersecurity.
Scaling Content Security Policy: Enterprise Compliance and Third-Party Resource Management
Learn to implement Content Security Policy and monitor web resources at scale, addressing supply chain attacks and PCI requirements for enhanced frontend security in enterprise applications.
My Favorite Ethical Hacking Books
Discover essential ethical hacking books recommended by a top hacker. Gain insights into web application security, bug bounty hunting, and penetration testing to enhance your cybersecurity skills.
Hacking a Payment Processor - Episode 2
Explore ethical hacking techniques for payment processors with NahamSec and Rhynorater. Learn practical skills through a hands-on lab and gain insights into cybersecurity vulnerabilities in financial systems.
Cross Site Scripting (XSS) in 2023 - The Mitigated Unmitigated Vulnerability
Explore the current state of Cross-Site Scripting (XSS) vulnerabilities, their impact, and mitigation strategies in modern web security landscape.
Security Is Key - The Vulnerabilities of API Security
Explore API security vulnerabilities and learn essential strategies to protect your systems from potential threats in this informative talk by Joe Wrieden.
SQL Injection 101 - Pentesting Diaries
Explore SQL injection techniques and tools in this weekly pentesting series. Learn attack methods, tool usage, and optimization for deeper understanding and improved efficiency.
Burp Extension Development - Setup and Basics
Learn to develop Burp Suite extensions, from setup to creating custom features. Hands-on guide covers environment setup, building extensions, and modifying request headers.
Penetration Testing Interview Questions and Answers - Master Scenario Based Prep
Master scenario-based interview prep for penetration testers. Covers vulnerability assessments, exploit development, and real-world scenarios to boost confidence and skills for landing dream jobs in cybersecurity.
Unlocking the Power of Nuclei: A Comprehensive Guide - Part 1
Master Nuclei's powerful capabilities for identifying security vulnerabilities. Learn to integrate this user-friendly tool into your penetration testing and vulnerability assessment processes.
OWASP Coraza Web Application Firewalls Revisited
Explore OWASP Coraza's advanced features for securing web applications, including its architecture, rule language, and integration capabilities with popular web servers and frameworks.
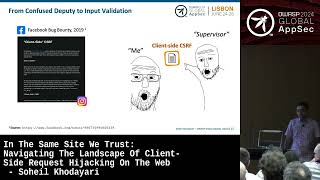
Navigating the Landscape of Client-Side Request Hijacking on the Web
Explore client-side request hijacking vulnerabilities, their impact on web security, and effective mitigation strategies to protect against these emerging threats.
SQL Injection Explained - Understanding Attacks and Prevention
Comprehensive guide to SQL injection attacks: types, vulnerabilities, and prevention techniques. Learn to identify, exploit, and protect against database security threats through practical examples and best practices.