Python Security & Cryptography
Introducción a la criptografía y seguridad en Python, explorando bibliotecas de encriptación, algoritmos de cifrado, esteganografía y prácticas de codificación segura para desarrolladores.
Behind Closed Doors - Managing Passwords in a Dangerous World
Explore password management strategies for modern applications, covering encryption keys, database passwords, and API credentials. Learn about emerging tools to manage, update, and audit secrets securely.
Replacing Passwords with Multiple Factors - Email, OTP, and Hardware Keys
Explore modern authentication methods beyond passwords, including email-based, one-time passwords, and hardware keys. Learn implementation strategies for enhanced security in Python web applications.
Deploying Secure Angular Apps that Scale
Learn to deploy secure, scalable Angular apps using Azure Static Web Apps. Covers CI/CD, custom domains, SSL, APIs, global distribution, authentication, and authorization.
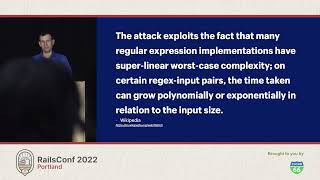
Service Denied! Understanding How Regex DoS Attacks Work
Explore regex DoS attacks in Rails, understand their mechanics, and learn prevention strategies. Dive into CRuby's regex engine and grasp the underlying principles of regular expressions.
Writing an Insecure Webapp
Explore common web app vulnerabilities and learn effective security practices to protect against threats like cross-site scripting and ensure robust application safety.
Towards a Post-XSS World
Explore Content Security Policy as a powerful tool to combat cross-site scripting attacks, enhancing web application security and regaining control over your code execution environment.
Secure Crypto for Browser Based Apps
Explore secure cryptography implementation in browser-based apps, focusing on Mailpile's approach to shifting the attack surface while maintaining a user-friendly interface and leveraging JavaScript capabilities.
HTTP Headers - The Simplest Security
Explore essential HTTP security headers like Content-Security-Policy and Strict-Transport-Security. Learn implementation, browser support, and best practices for protecting web applications.
JS Security - A Pentester's Perspective
Explore JavaScript security from a pentester's perspective, focusing on DOM XSS, CORS, and secure coding practices to identify and prevent vulnerabilities in web applications.
Browser Security in 2017
Explore modern browser security challenges and solutions in this insightful talk on web vulnerabilities, attack vectors, and protective measures for developers.
XSS, CSRF, CSP, JWT, WTF? IDK - JSConf Iceland
Explore web application security, including XSS, CSRF, JWT, and CSP. Learn protection strategies for modern front-end frameworks and REST APIs to safeguard against evolving threats.
Web Application Security - Browsers Fight Back
Explore browser-based security measures like XSS filters, HTTP headers, and protocols to prevent common web application vulnerabilities and enhance overall protection.
Security in ASP.NET Core 2.0
Explore new security features in ASP.NET Core 2.0, including improved authentication, authorization, and cryptographic key management for building more secure web applications.
Web Application Security Risks - A Look at OWASP Top Ten 2017
Explore the latest OWASP Top Ten 2017 security risks for web applications. Learn about changes, updates, and best practices for creating secure web applications in this comprehensive overview.
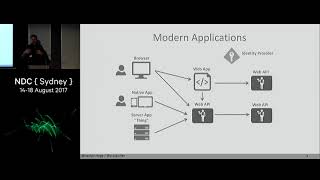
Implementing Authorization in Web Applications and APIs
Learn strategies for implementing robust authorization in web applications and APIs, exploring various approaches, pitfalls, and the ASP.NET Core authorization API to create clean and effective authorization systems.
The Code Behind The Vulnerability
Explore advanced web security vulnerabilities beyond SQL injection, focusing on issues in dictionaries, compression, and encryption to enhance your code's resilience against sophisticated attacks.
Beyond the OWASP Top 10 - Modern Web Application Bugs
Explore modern web application vulnerabilities beyond OWASP Top 10, including XML External Entity, Serialization, and Server-side Request Forgery. Learn detection and mitigation strategies for emerging security threats.
Web Application Security Trends
Explore modern web security threats beyond traditional attacks, including vulnerabilities in Angular, Clickjacking, and XSS via file uploads. Stay updated on evolving risks and defense strategies.
Getting Benefits of OWASP ASVS at Initial Phases
Explore OWASP ASVS implementation for web app security, covering 189 controls in 16 categories. Learn to define, analyze, and evaluate security tests across different maturity levels for various industries.
The Code Behind The Vulnerability
Explore advanced web security vulnerabilities beyond SQL injection, focusing on issues in dictionaries, compression, and encryption to enhance your code's resilience against sophisticated attacks.