Web Application Security - OWASP AppSecUSA 2014 Defenders Track
Explore cutting-edge web security topics including cloud security, malware analysis, and reverse engineering in this comprehensive conference track from OWASP AppSecUSA 2014.
OWASP Global Board Keynote - AppSecUSA 2014
Keynote address from OWASP Global Board at AppSecUSA 2014, discussing latest developments and strategies in application security. Offers insights for cybersecurity professionals and developers.
Application Security Breakers Track - OWASP AppSecUSA 2014
Live stream of AppSecUSA 2014 featuring talks on JavaScript security, .NET hacking, client-side exploitation, Oracle Application Framework penetration testing, and headless browser techniques for web application security.
OWASP AppSecUSA 2014 - Builders Track Sessions
Explore cutting-edge web security topics including OWASP tools, .NET hacking, iOS integrity, password complexity, and client-side security in this comprehensive AppSecUSA conference session.
OWASP Community Update - July 2014
Explore OWASP's latest developments, events, and projects in this community update. Learn about the ABSA Cambridge Conference and new initiatives within the open-source security community.
Active Scan Augmenting Manual Testing with Attack Proxy Plugins
Explore advanced web security techniques with ActiveScan++, a Burp Suite plugin for detecting complex vulnerabilities like host header poisoning and code injection through heuristic probes and automated analysis.
Practical Tips for Web Application Security in the Age of Agile and DevOps
Practical tips for adapting web application security to agile and DevOps environments, focusing on lightweight controls, visibility, and measuring maturity in modern development practices.
Misconfigured CORS and Web Application Security Challenges
Explore CORS misconfiguration vulnerabilities and the challenges of implementing advanced browser security features, with insights on balancing security and operational complexity.
OWASP Security Knowledge Framework - Making the Web Secure by Design
Learn about OWASP's Security Knowledge Framework for designing secure web applications, focusing on proactive security measures and best practices for developers.
OWASP Top Ten Proactive Controls for Secure Web Development
Learn essential secure coding techniques for web development, covering validation, authentication, access control, encoding, data protection, and secure architecture to build robust and protected applications.
HTTP Headers for Security - No Better ROI
Discover powerful, low-cost HTTP headers for enhancing web application security and business success. Learn to make a significant impact with minimal effort in this informative talk.
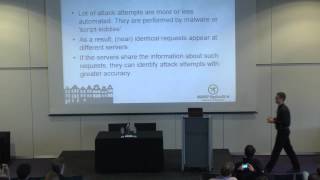
Collective Detection of Harmful Requests
Explore collective detection techniques for identifying harmful web requests, enhancing application security through shared threat intelligence and collaborative defense strategies.
The Tales of a Bug Bounty Hunter - 10 Interesting Vulnerabilities
Explore 10 fascinating vulnerabilities discovered by a bug bounty hunter, offering insights into real-world security flaws and their implications for web application security.
The ABCs of Source-Assisted Web Application Penetration Testing
Learn advanced web application penetration testing techniques using source code analysis for improved vulnerability detection and assessment.
The Top 10 Web Hacks of 2015
Explore the most impactful web security breaches of 2015, gaining insights into vulnerabilities, attack methods, and essential defensive strategies for safeguarding web applications.
From Zero to Hero - How OWASP Saved My Holiday
Discover how OWASP resources can transform your cybersecurity skills and protect your digital life, as demonstrated through a real-world holiday scenario.
PDF - Mess With The Web
Explore PDF vulnerabilities and their impact on web security in this talk by Alex Infuhr, highlighting potential risks and mitigation strategies for developers and security professionals.
WebRTC Security - How Secure Is P2P Browser Communication?
Explore the security implications of peer-to-peer browser communication through WebRTC, examining potential vulnerabilities and best practices for secure implementation.
Security and Insecurity of HTTP Headers
Explore HTTP header security and vulnerabilities with Dirk Wetter. Learn about potential risks and best practices for implementing secure headers in web applications.
Using a JavaScript CDN That Cannot XSS You - With Subresource Integrity
Learn about Subresource Integrity, a security feature that protects against XSS attacks when using JavaScript CDNs, enhancing web application safety.
Hackazon: Stop Hacking Like It's 1999
Explore Hackazon, a modern vulnerable web app for testing security skills. Learn about its AJAX interface, RESTful APIs, and configurable vulnerabilities that challenge both automated scanners and manual pentesters.