Backdooring 4 Million Modems with 6 Bugs in a Week - Cybersecurity Case Study
Explore how a researcher exploited vulnerabilities to potentially compromise millions of modems, highlighting the critical importance of cybersecurity in telecommunications infrastructure.
The Hunt for CVE-2023-0286 - Replicating OpenSSL's Latest Vulnerability
Replicate CVE-2023-0286 in OpenSSL, learn to write a libfuzzer harness, and explore vulnerability research techniques for enhanced security awareness and threat prevention.
From Theory to Practice - Navigating the Challenges of Vulnerability Research
Explore practical challenges and strategies in vulnerability research, enhancing your skills to identify and mitigate security weaknesses in software systems.
CVE Hunting: Wi-Fi Routers, OSINT and The Tyranny of the Default
Explore CVE hunting techniques for Wi-Fi routers, focusing on default credential vulnerabilities and OSINT strategies to uncover critical security flaws across manufacturers.
Finding and Exploiting Critical Vulnerabilities in RPC Services - NorthSec 2023
Comprehensive walkthrough of finding, exploiting, and reporting critical vulnerabilities in an RPC service, covering reverse engineering, authentication bypass, and coordinated disclosure.
Blasting Past WebP - Exploring Image Format Vulnerabilities
Explore advanced techniques for bypassing WebP image format security measures, uncovering vulnerabilities and potential exploits in web applications.
ACE up the Sleeve: Hacking into Apple's New USB-C Controller
Explore Apple's USB-C controller vulnerabilities and hacking techniques with expert Thomas Roth in this cutting-edge cybersecurity presentation.
Attacking the Samsung Galaxy A Boot Chain
Explore Samsung Galaxy A* boot chain vulnerabilities and attack techniques for enhanced mobile security understanding.
Beyond Android MTE: Navigating OEM's Logic Labyrinths
Explore advanced Android security, focusing on Memory Tagging Extension (MTE) and OEM-specific implementations. Gain insights into exploiting vulnerabilities in custom logic.
One SMS to Root Them All: Exposing Critical Threats in Connected Devices
Explore critical vulnerabilities in connected devices through SMS exploitation, uncovering potential threats to millions of users worldwide.
Hunting File System Redirection Bugs Through Instrumentation
Explore file system redirection vulnerabilities and learn advanced techniques for identifying and exploiting these security risks in Windows systems.
Unexpected Intrusion Testing Results in SAP Systems - Critical Vulnerabilities and Exploits
Unveiling critical vulnerabilities in SAP Start Service, from local to remote exploits. Explores memory corruption and OS command injection leading to root-level RCE, with live demo and recommendations.
Windows Agentless C2 - Abusing the MDM Client Stack
Unveils innovative research on exploiting Windows MDM stack for agentless C2 systems. Explores vulnerabilities, custom C2 server creation, and remote device control techniques, inspiring new defensive strategies.
Attacking Windows Device Drivers: Almost Escaping the Sandbox
Explore techniques for attacking Windows device drivers and potential sandbox escape methods in this advanced security analysis presentation.
Practical Exploitation of Registry Vulnerabilities in the Windows Kernel
Explore practical exploitation techniques for Windows kernel registry vulnerabilities, enhancing your understanding of system security and potential attack vectors.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Racing for Hidden Treasures in Public GitHub Repositories - Exploiting Build Artifacts
Explore a novel attack vector in GitHub Actions, uncovering hidden access tokens in build artifacts and racing against time to exploit ephemeral credentials for swift attacks on open-source projects.
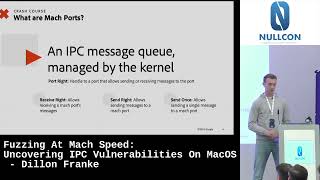
Fuzzing at Mach Speed: Uncovering IPC Vulnerabilities on MacOS
Explore macOS IPC security, focusing on Mach message handlers. Learn about custom fuzzing techniques to uncover vulnerabilities in privileged RPC-like functions, potentially leading to sandbox escapes and privilege escalations.
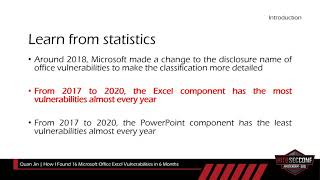
How I Found 16 Microsoft Office Excel Vulnerabilities in 6 Months
Discover the process of finding 16 Microsoft Excel vulnerabilities through fuzzing, including corpus selection, mutation algorithms, and result management techniques.
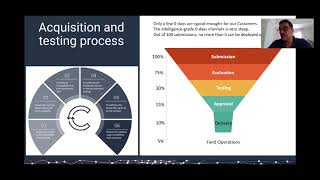
Shaping the Future of the 0Day Market
Shaping the future of the 0-day vulnerability market through improved standards, platforms, and practices to enhance cybersecurity capabilities for law enforcement and intelligence agencies.
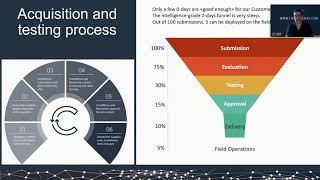
Hacking the 0day Marketplace
Exploring the 0day vulnerability market's challenges and proposing solutions to improve efficiency, safety, and professionalism for all stakeholders in cybersecurity.