Surviving the CVE Firehose: Strategies for Open Source Product Security
Strategies for managing and improving product security amidst constant vulnerability threats. Learn to track, prioritize, and address security issues effectively in open source projects.

Keeping Up with CVEs - Security Response Management Best Practices
Explore security update challenges, best practices, and tools for managing vulnerabilities in released products. Learn strategies to efficiently handle CVEs and maintain software security.
Effective Usage Analysis: The Shortest Path Between Developer and Accelerated Product Releases
Discover how effective usage analysis prioritizes vulnerabilities, enabling developers to focus on exploitable risks, streamline remediation, and accelerate product delivery.
AppSec Challenges - Overcoming Framework Limitations and Building Robust Security
Exploring challenges in application security, analyzing framework limitations, and discussing robust approaches to improve security at scale while making it more manageable.
Building a Secure Future: Lessons from Past and Present Information Security Challenges
Explore the future of information security, examining past lessons, current challenges, and emerging technologies like quantum cryptography to build a more secure digital world.
Software Supply Chain Lifecycle Management: Reducing Attack Vectors and Enabling Rugged DevOps
Exploring software supply chain lifecycle management to reduce attack vectors and enable rugged DevOps, focusing on IoT security, third-party software risks, and standards-based automation for threat detection.
Making Vulnerability Management Less Painful with OWASP DefectDojo
Streamline vulnerability management with DefectDojo: automate reporting, metrics, and scanner consolidation. Learn how this open-source tool can enhance your AppSec program's efficiency and effectiveness.
Managing Vulnerability Response Dependencies in Third-Party Components - AppSecCali 2019
Explore a framework for managing dependencies in vulnerability response, enabling proactive PSIRT strategies and improving product security through early-stage decision-making and controls.
Making Vulnerability Management Less Painful with DefectDojo
Streamline vulnerability management with DefectDojo: automate deduplication, reporting, and metrics for efficient AppSec programs. Learn how this open-source tool simplifies tedious tasks and enhances team productivity.
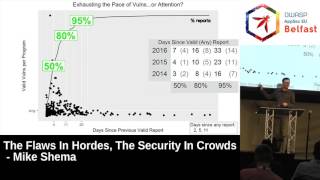
The Flaws in Hordes, The Security in Crowds - Crowdsourced Security Models
Explores the effectiveness of bug bounty programs in improving application security, discussing strategies for success and potential pitfalls to avoid. Examines trends in appsec automation and remaining challenges.
Software Bill of Materials (S-BoM) - Reducing Risk in Third-Party Components
Explore best practices for managing third-party component risks using software bill-of-materials (S-BoM). Learn to create S-BoMs, identify vulnerabilities, and automate security responses in polyglot environments.
The Art of Vulnerability Management - Transforming Security Collaboration
Transforming vulnerability management from a nuisance to a collaborative process that drives accountability and transparency in software security through decentralization and empowerment.
Securing In-House Execution of Unsafe Third-Party Executables
Explore a framework for securely executing third-party code in production environments, addressing challenges and implementing best practices to mitigate risks associated with untrusted executables.
Eradicating Vulnerability Classes: Embracing Secure Defaults and Invariants
Explore innovative approaches to application security, focusing on secure defaults and invariants instead of traditional SAST methods to effectively eliminate vulnerability classes.
Normalizing AppSec Issues for Contextual Risk-Based Prioritization at Enterprise Scale
Explore a new approach to Application Security that focuses on critical risks by incorporating contextual intelligence, improving efficiency and delivery in enterprise-scale programs.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
What Shall We Do With a Vendor SBOM? - Understanding Software Bill of Materials
Explore the practical applications of Software Bill of Materials (SBOM) in cybersecurity, covering procurement, vulnerability disclosure, threat intelligence, and forensics.
Threat Modeling of Containerized Applications - Three Levels of Complexity
Optimize threat modeling for containerized applications, focusing on efficiency, new dimensions, and real-world impact. Learn to measure success and implement incremental improvements in application security.
Looking Towards the Future of Open Source Vulnerability Management
Explore the evolving landscape of open source security, focusing on vulnerability management strategies, industry trends, and best practices for effective remediation and continuous security integration.
Overwhelmed by Vulnerability Triage - A Blend of Best Practices
Learn effective strategies for managing vulnerability triage, combining industry best practices to streamline your security processes and improve overall risk management.
Software Supply Chain Security
Explore software supply chain security with expert Vandana Verma, covering key concepts, best practices, and strategies to protect your development pipeline from vulnerabilities and attacks.