Putting the Management into Vulnerability Management or You've Got Bears
Practical strategies for effective vulnerability management, using bear safety as an analogy. Learn to set up defenses, recognize threats, and implement a cyclical approach for better cybersecurity.
When is a Vulnerability Not a Vulnerability? Overcoming the Inundation of Noisy Supply Chain Security Alerts
Explore a counterintuitive approach to strengthening security by ignoring over 90% of vulnerability alerts, enabling improved workflows and behavior in supply chain security management.
Container Vuln Management with - Hopefully Minimal Burnout
Explore a graph-based approach for efficient vulnerability management in microservices, focusing on identifying and fixing inherited vulnerabilities across large-scale architectures.
The Art of Defense - How Vulnerabilities Help Shape Security Features and Mitigations in Android
Explore Android's evolving security landscape, examining threats, vulnerabilities, and defensive measures. Learn how the Android Security Team addresses challenges and implements new features to protect users.
Who Watches the Watchers? Metric for Security Strategy
Explore effective security metrics, their importance in decision-making, and how to develop meaningful measurements for vulnerability management and incident response.
Find and Track the Hidden Vulnerabilities Inside Your Dependencies
Learn to detect and manage hidden vulnerabilities in open-source dependencies using tools like OWASP DependencyCheck and DependencyTrack, creating a Continuous Security pipeline for DevSecOps practices.
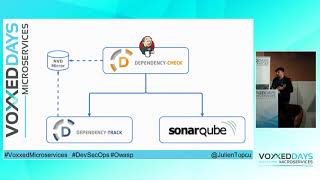
Find and Track the Hidden Vulnerabilities Inside Your Dependencies
Learn to detect and track hidden vulnerabilities in open source dependencies using OWASP tools. Create a Continuous Security pipeline with Jenkins for improved application security.
The Anatomy of Java Vulnerabilities
Explore Java vulnerabilities, their impact, and defense strategies. Learn about reporting, managing, and fixing security issues to protect your code from cyber threats.
The Application Security State of the Union
Explore the current and future landscape of AppSec, including threats, vulnerabilities, tools, and strategies. Gain insights to build robust security programs and prepare for emerging challenges.
Security in the Delivery Pipeline
Modern approaches to integrate security testing throughout the software delivery pipeline, emphasizing continuous security practices for improved quality and safety in DevOps environments.
What Style of Security Do You Want?
Explore diverse security styles, from phishing prevention to resilient system design. Learn practical strategies for compliance, vulnerability management, and decision-making in modern cybersecurity environments.
Vulnerability Intelligence
Explore vulnerability intelligence, analyzing 10 years of data to improve prioritization and mitigation strategies for security specialists navigating the complex landscape of weaknesses.
Securing Open Source Software - End-to-End, at Massive Scale, Together
Explore challenges and strategies for securing open source software at scale, drawing insights from major vulnerability remediations and discussing industry-wide coordination efforts.
IOT and AppSec
Explore the intersection of Internet of Things (IoT) and application security, examining potential vulnerabilities and strategies for safeguarding connected devices and systems.

Security Module for PHP7 - Killing Bugclasses and Virtual-Patching the Rest
Explore Snuffleupagus, a new PHP security module for killing bug classes and virtual-patching vulnerabilities without modifying application code. Learn its features and implementation.
The Internet of Us
Explore the evolving landscape of IoT security, challenging industry norms and emphasizing the need for new approaches to protect businesses and consumers in the interconnected world.
DevOps, CI, APIs, Oh My! - Security Gone Agile
Explore agile security practices for rapid deployment in DevOps environments, covering infrastructure, APIs, and code security to keep pace with modern development cycles.
Security for Non-Unicorns
Strategies for uncovering, preventing, and managing security issues in legacy systems and code for established companies. Practical approaches to improving security beyond startup environments.
Mobile AppSec - Development and Alphabet Soup
Explore mobile app security challenges, vulnerabilities, and solutions. Learn effective strategies for protecting data and applications in the rapidly evolving mobile landscape.
Problems You'll Face When Building a Software Security Program
Learn strategies to overcome common challenges in implementing software security programs, including dev process integration, team engagement, and vulnerability management.
CyberRange - An Open-source Offensive Security Lab In AWS
Learn to create a private AWS security training lab using SecDevOps-Cuse/CyberRange. Explore automation, vulnerability management, and offensive security in a safe cloud environment.