You're Right, This Talk Isn't Really About You - DefCamp - 2018
Explore user-centric cybersecurity approaches, challenging traditional views and offering practical strategies to enhance organizational security through improved engagement and understanding.
Securing Without Slowing - DefCamp - 2017
Explore DevOps-inspired strategies for enhancing security without compromising speed. Learn about rugged DevOps, pipeline protection, and automation to create robust, efficient systems.
From Hype Hangover to Happy Hacking - Shaping the World through Shaping Actions - DefCamp 2015
Explore hacking's impact on shaping actions, from hype to practical applications. Gain insights into cybersecurity challenges, collaborations, and the future of information security.
API Security - Is it the New Application Attack Surface and How to Secure at Enterprise Scale
Explore API security challenges, threats, and enterprise-scale solutions. Learn about modern attack surfaces, recent breaches, and effective strategies for protecting sensitive data in API-driven architectures.
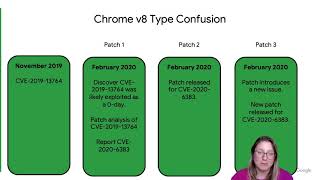
The State of 0-Day in-the-Wild Exploitation
Comprehensive analysis of 0-day exploits from 2020, offering insights on vulnerabilities, exploitation methods, and strategies to enhance cybersecurity and protect users from unknown threats.
BeyondProd- The Origin of Cloud-Native Security at Google - Brandon Baker - USENIX Enigma - 2020
Exploring Google's BeyondProd: A cloud-native security model emphasizing service trust, workload isolation, and automated vulnerability management for microservices-based architectures.
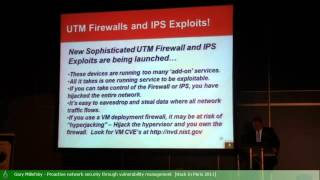
Proactive Network Security Through Vulnerability Management - Gary Miliefsky - Hack in Paris
Gain insider knowledge on network vulnerabilities, learn about CVEs, and discover proactive techniques to protect against cyber threats using free tools and heuristic systems.
OWASP Flagship Projects - OWASP DefectDojo
Learn about OWASP DefectDojo, an open-source application security management tool. Explore its features, automation capabilities, deployment options, and community-driven development.
OWASP Cloud-Native Application Security Top 10 Flagship Project
Explore key security challenges and best practices for cloud-native applications, focusing on OWASP's top 10 vulnerabilities and mitigation strategies.
Security as a Service - Work Where You Engineers Live
Integrating security into existing development workflows for efficient vulnerability management and faster response times. Learn how to leverage automation and project tracking tools to enhance security practices.
Lessons from Integrating Third Party Library Scanning in DevOps Workflow
Integrating third-party library scanning in DevOps: automation strategies, architectural choices, and best practices for secure development at scale. Tips for seamless implementation and measuring success.
We Come Bearing Gifts - Enabling Product Security with Culture and Cloud
Explore innovative approaches to product security, emphasizing automation, cloud deployment, and engineering enablement. Learn how Netflix balances security impact with developer productivity.
Being Powerful While Powerless - Elevating Security By Leading Without Authority
Learn strategies for elevating security without formal authority, including technical approaches and cultural tactics to influence stakeholders and drive positive change in organizational security practices.
Real Time Vulnerability Alerting by Using Principles from the United States Tsunami Warning Center
Learn how to implement real-time vulnerability alerting using principles from the US Tsunami Warning Center, covering triage methods, data analysis, and prioritization techniques.
External Attack Surface Management - Intelligent Defense in the Age of Digital
Explore intelligent defense strategies for managing external attack surfaces in the digital age, focusing on vulnerability assessment and threat intelligence for critical asset protection.
Hacking into Your Containers, and How to Stop It
Explore container security vulnerabilities and learn proactive DevSecOps practices to protect your deployments. Live hack demonstration and practical steps for hardening clusters against attacks.
Container Security - Theory & Practice at Netflix
Explore Netflix's container security journey, covering theory, architecture, and practical lessons learned as container usage rapidly expanded across the organization.

Docker Container Security
Learn to create a secure software supply chain using Docker Enterprise, focusing on image signing, scanning, and automated policies for compliant application development.
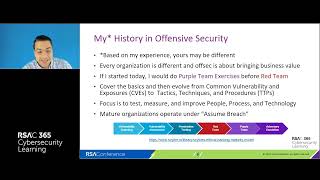
Intro to Purple Team - Cyber Threat Intelligence, Attack, Detect, Respond
Learn to build an effective Purple Team program, covering threat intelligence, attack emulation, and detection engineering using MITRE ATT&CK as a common language for improved cybersecurity.
Fad or Future - Getting Past the Bug Bounty Hype
Panel discussion on bug bounty programs: insights, challenges, and best practices from experienced program managers. Covers ROI, hunter interactions, and lessons learned for effective implementation and management.
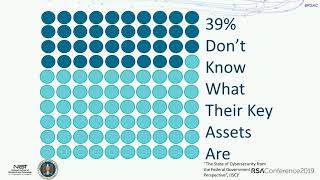
Making Security Automation Real
Explore standardized posture information collection for automated security and network hardening. Learn to move from standards to commercial solutions in the fight against network intrusions.