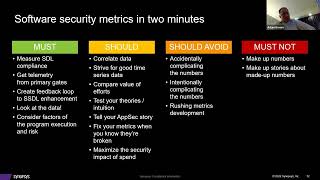
Over a Decade of Software Security - What Have We Learned
Explore key insights and lessons from a decade of software security evolution, highlighting crucial developments and best practices for modern cybersecurity professionals.
Supply Chain Security with Dependency Track
Explore supply chain security using Dependency Track with experts Anandan, Bhargava, and Duster. Learn strategies to mitigate risks and enhance software security in this informative session.
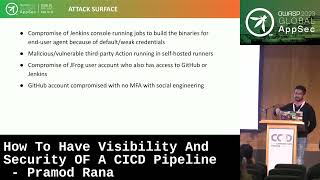
How to Have Visibility and Security of a CI/CD Pipeline
Discover strategies for enhancing visibility and security in CI/CD pipelines, focusing on best practices and tools to safeguard your software development lifecycle.
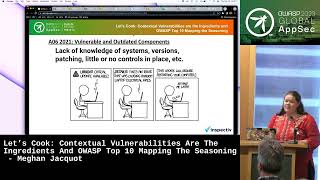
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
OWASP DSOMM Project - Introduction to DevSecOps Maturity Model
Explore the OWASP DSOMM Project, a framework for enhancing software security practices and measuring DevSecOps maturity in organizations.
OWASP DefectDojo Project
Explore DefectDojo, an open-source vulnerability management tool. Learn its features, implementation, and how it streamlines security testing workflows for development teams.
Post-DevOps: What Should We Shift-Left in Application Security?
Exploring post-DevOps challenges in AppSec, focusing on risk profiles, threat response architecture, and operational aspects to enhance security and quality in fast-paced development environments.
Real World Security - Software Supply Chain
Explore software supply chain security through a case study on misconfigured registries, threat modeling, and best practices for securing the build-ship-run pipeline.
Talking TUF: Securing Software Distribution
Explore The Update Framework (TUF) for securing software update systems. Learn how to integrate this flexible security framework to protect against vulnerabilities and enhance software distribution safety.
Hard to Port - A Snapshot of the Vulnerability Landscape in 2015
Explore the 2015 vulnerability landscape through anonymized data, discussing trends, challenges, and the shift towards continuous application security and risk management.
AppSec Awareness - A Blueprint for Security Culture Change
Discover strategies for building a sustainable security culture through AppSec awareness, focusing on human factors, knowledge sharing, and effective program architecture.
Running a Bug Bounty Program - What You Need to Know
Discover essential insights for running successful bug bounty programs, including strategies, resources, and best practices for effective vulnerability management and rewards.
Practical Tips for Running a Successful Bug Bounty Program
Practical tips for running a successful bug bounty program, including scope definition, communication strategies, and vulnerability rating. Insights from experienced professionals on managing crowdsourced security testing effectively.
Building a Better Hacker to Improve Cybersecurity Defense
Explore how understanding hacker mentality bridges the gap between developers and security teams, leading to more effective cybersecurity strategies and proactive threat prevention.
Proactively Defending Your Business Against Security Protocol Attacks - OWASP AppSec California 2015
Explore strategies to proactively defend against security protocol attacks and implementation flaws in HTTPS/SSL/TLS. Learn about recent vulnerabilities, mitigations, and best practices for secure communications.
Implementing a Supply Chain Approach to Build and Deploy Secure Applications - AppSecEU 2016
Explore implementing a supply chain approach to build and deploy secure software, focusing on trust, standardization, and automation in the software delivery pipeline.
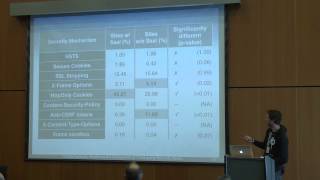
Issues and Limitations of Third Party Security Seals
Explore limitations of third-party security seals in web applications, uncovering potential vulnerabilities and discussing implications for online security practices.
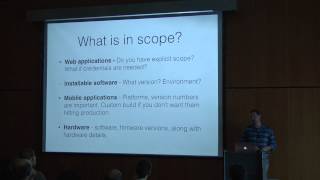
Hard Knock Lessons on Bug Bounties
Insights and lessons learned from managing bug bounty programs, covering legal aspects, scope definition, program structure, and reward strategies for effective vulnerability disclosure.
Introduction to the Newest Addition to the OWASP Top 10 - A9 Guidelines
Experts discuss the new OWASP A9 guideline on insecure open source libraries, offering insights on component usage, best practices, and real-world challenges in mitigating risks in agile development.
OWASP A9: Using Components with Known Vulnerabilities - A Year Later
Explore real-world case studies and industry trends on managing component vulnerabilities in applications, with insights on best practices and challenges in following OWASP A9 guidelines.
Stop Chasing Vulnerabilities - Introducing Continuous Application Security
Explore continuous application security strategies using open-source tools for real-time monitoring and analytics, shifting focus from individual vulnerabilities to comprehensive portfolio-wide assurance.