Kubernetes Goat - Interactive Kubernetes Security Learning Playground
Explore Kubernetes security through hands-on scenarios, attack simulations, and real-world vulnerabilities. Learn to identify and mitigate risks using open-source tools for secure code and container deployment.
CVSS v4 - A Better Version of an Imperfect Solution for Vulnerability Scoring
Explore CVSS v4's role in vulnerability risk management, its challenges, and potential improvements for effective cybersecurity prioritization and assessment.
Shedding Light on CVSS Scoring Inconsistencies: A User-Centric Study on Evaluating Widespread Vulnerabilities
Explore CVSS scoring inconsistencies through a user-centric study, evaluating widespread vulnerabilities and their impact on cybersecurity assessments.
Microarchitectural Side Channel Attacks on MCU Bus Interconnect - BUSted 2024
Explore microarchitectural side channel attacks on MCU bus interconnects, focusing on vulnerabilities and potential security implications for embedded systems.
Break the Wall: Automated Discovery of Protocol-Level Evasion Vulnerabilities in Web - Session 584
Automated discovery of protocol-level evasion vulnerabilities in web applications, focusing on bottom-up approaches to identify and exploit security weaknesses.
Exploring the New World - Remote Exploitation of SQLite and Curl
Discover new methods for finding vulnerabilities in SQLite and Curl through fuzzing and manual auditing, including insights on "Magellan" and "Dias" vulnerabilities.
Wargames - Java Vulnerabilities and Why You Should Care
Explore Java vulnerabilities, security tools, and best practices to protect applications. Learn about CVEs, software supply chain risks, and DevSecOps strategies for robust Java development.
A CISO's Best Friend - The Pentester
Discover how penetration testing can be a collaborative, educational tool for improving security posture and identifying business risks. Learn to foster valuable partnerships between CISOs and pentesters.
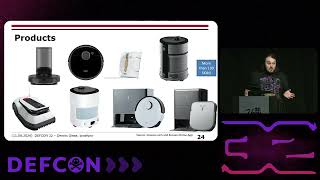
Reverse Engineering and Hacking Ecovacs Robots - Security Vulnerabilities and Privacy Concerns
Dive into the security vulnerabilities of Ecovacs robots, exploring broken encryption, unauthorized camera access, and privacy concerns while learning techniques for privacy-preserving usage and rooting.
Open Source Software Transparency for Acquisition - Making Security Trade-off Decisions
Explore software security measurement strategies and trade-off decisions for organizations using open-source components, focusing on vulnerability assessment, process metrics, and cybersecurity analysis.
The Simple Yet Lethal Anatomy of a Software Supply Chain Attack
Explore software supply chain vulnerabilities through an attacker's lens, examining open-source security flaws and defense strategies with practical demonstrations and countermeasures.

Secret Scanning in Open Source at Scale - An In-Depth Analysis
Discover critical insights into large-scale secret scanning across NPM packages, WordPress plugins, and Ruby Gems, exploring supply chain vulnerabilities and implementing preventive measures in CI/CD pipelines.
Securing AI-Generated Code: Challenges and Solutions for the Future
Explore the critical challenges and solutions for securing AI-generated code, featuring practical tools and research for building AI security engineering capabilities.
Identifying and Securing Psychologically Vulnerable Users
Explore psychological traits that make users vulnerable to security threats and learn data-driven strategies to enhance organizational security and red team effectiveness.
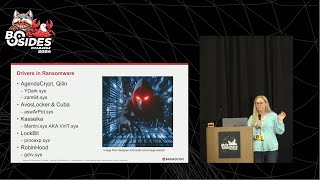
Driver Risk Scores: Threat Detection System for Vulnerable Device Drivers
Discover how Driver Risk Scores (DRS) system evaluates device driver vulnerabilities through seven key traits, enabling informed security decisions for system administrators and security teams.
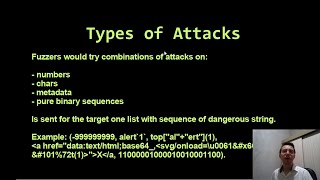
Fuzzing - Finding Your Own Bugs and Zero-Days
Master the art of fuzzer creation and vulnerability discovery, exploring buffer overflow exploitation techniques with hands-on demonstrations and practical exploit development strategies.
Leakonomics 101: The Last Year in Data Leaks - Analysis and Trends
Explore the anatomy of data leaks through real-world cases from the past year, examining breach patterns, criminal marketplace dynamics, and emerging trends in cybersecurity threats and vulnerabilities.
Hacking War Stories: From Prison Systems to Tech Companies - A Series of Unfortunate Events
Dive into real-world hacking adventures, from prison systems to major tech companies, exploring identification, exploitation techniques, and potential impact across different organizational contexts.
Hacking PBX and UC Systems: Attack Surface Analysis and Vulnerability Discovery
Dive into enterprise PBX/UC system vulnerabilities, exploring attack surfaces, Java Runtime exploitation, PHP decryption, and shell access techniques in communication infrastructure.
Attacking and Securing the Google Pixel Modem - Security Analysis and Vulnerabilities
Dive into mobile security as Android Red Team reveals their offensive evaluation techniques and findings on Pixel device modems, focusing on baseband vulnerabilities and protective measures.
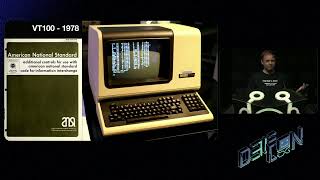
Terminally Owned - 60 Years of Terminal Escape Code Vulnerabilities
Explore terminal security vulnerabilities across platforms, from ASCII's escape character origins to modern exploit techniques, revealing critical remote code execution risks and defense strategies.