iGoat: A Self-Learning Tool for iOS App Security Testing
Learn iOS app security through hands-on exercises with iGoat, an open-source tool for developers and pentesters. Explore vulnerabilities, exploit techniques, and implement fixes in a safe environment.
Attacking AWS: The Full Cyber Kill Chain
Comprehensive exploration of AWS vulnerabilities and attack strategies, covering the entire cyber kill chain for enhanced cloud security awareness.
Securing Node.js and JavaScript
Explore common security vulnerabilities in Node.js and JavaScript ecosystems, and learn effective strategies to protect your applications from potential attacks.
How I Could Have Stolen Your Photos From Google
Uncover a critical security vulnerability in Google Photos and learn how it could have compromised user privacy. Gain insights into responsible disclosure and ethical hacking practices.
SUSTO: Systematic Universal Security Testing Orchestration
Explore systematic universal security testing orchestration for efficient vulnerability detection and management in software development lifecycles.
AWS Misconfiguration from an Attacker's Perspective
Explore AWS misconfigurations from an attacker's perspective with security analyst Kavisha Sheth. Learn to identify and mitigate vulnerabilities in cloud environments for enhanced cybersecurity.
OWASP Web Security Testing Guide
Comprehensive guide for web security testing, covering methodologies and best practices to identify vulnerabilities and enhance application security.
OWASP Top 10 - Introduction to Web Application Security Risks
Comprehensive overview of OWASP Top 10, exploring critical web application security risks and effective mitigation strategies for developers and security professionals.
OWASP Security Shepherd - Introduction and Overview
Learn to identify and mitigate web application vulnerabilities with OWASP Security Shepherd, an interactive platform for hands-on cybersecurity training and skill development.
Attacking Microservice Systems: Methods and Practical Tips
Discover methods and practical tips for attacking microservice systems, exploring new security architecture patterns and vulnerabilities specific to this increasingly popular design approach.
OWASP Security Shepherd - Mobile and Web Security Awareness and Education
Explore web and mobile app security risks through interactive lessons and challenges. Improve penetration testing skills and understand vulnerabilities using OWASP Security Shepherd's comprehensive platform.
Hacking Fantasy Sports Sites - Mobile App Security Vulnerabilities
Explore mobile app vulnerabilities through fantasy sports hacking. Learn techniques for intercepting traffic, exploiting formats like JSON and REST, and manipulating data in popular applications.
HTTP Time Bandit - Identifying Web Application Performance Bottlenecks
Explore web application vulnerabilities and efficient DOS/DDOS attack techniques using HTTP Time Bandit tool. Learn to identify resource-consuming pages for improved security or targeted attacks.
GoatDroid Release - Android Security Training Environment
Explore GoatDroid, a self-contained Android security training environment. Learn about insecure data storage, XSS, JavaScript interfaces, permissions, components, and more in this comprehensive webinar.
Introduction to OWASP's Zed Attack Proxy - Web Application Penetration Testing
Explore OWASP's free, open-source penetration testing tool for web applications. Learn its features, installation, and usage through hands-on demonstrations and testing of insecure web apps.
The 2013 OWASP Top 10 - Understanding Web Application Security Risks
Comprehensive overview of OWASP Top 10 2013, covering changes, risks, and mitigation strategies for web application security. Essential for developers and security professionals.
HTML5 and JavaScript Security Vulnerabilities
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 security concerns. Learn to protect against emerging web attack techniques.
A Look Under the Hood of CNCF Security Audits
Insights into CNCF security audits: process, expectations, outcomes, and common vulnerabilities. Explores experiences from auditing six major projects and the value of audit reports for contributors and researchers.
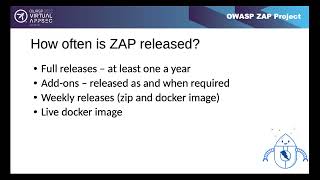
OWASP ZAP Project: Introduction to Web Application Security Testing
Learn to use OWASP ZAP, a powerful open-source web application security scanner. Discover its features, capabilities, and best practices for identifying vulnerabilities in web applications.
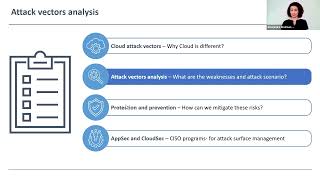
Cloud Attack Surface Management
Explore cloud security challenges and strategies for effective attack surface management in this insightful keynote by Alex Shulman Peleg.
15 Years of OWASP Top 10 - Has the Cloud Made a Difference?
Explore the evolution of web application security over 15 years, examining the impact of cloud computing on OWASP Top 10 vulnerabilities and current cybersecurity challenges.