Modern Application Security vs. GenAI Applications: Is Your AppSec Ready?
Explore the intersection of modern application security and generative AI, assessing readiness for emerging challenges in the evolving tech landscape.
Using Threat Modeling to Create a DevSecOps Plan
Discover how to leverage threat modeling for effective DevSecOps planning. Learn to identify threats, select appropriate security tools, and seamlessly integrate them into your development pipeline.
Exploiting NFC Vulnerabilities in Indian Metro Systems
Exploiting vulnerabilities in Indian metro systems' NFC technology for free travel. Insights into hacking MiFare cards, challenges faced, and potential solutions.
Choosing a Target for Bug Bounty Hunting
Learn effective strategies for selecting optimal bug bounty targets with expert Katie Paxton-Fear, enhancing your chances of success in vulnerability hunting.
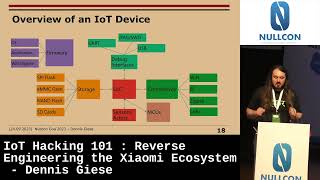
IoT Hacking 101 - Reverse Engineering the Xiaomi Ecosystem
Explore IoT hacking and reverse engineering techniques focused on the Xiaomi ecosystem, covering hardware methods, ecosystem analysis, and key findings in cybersecurity.
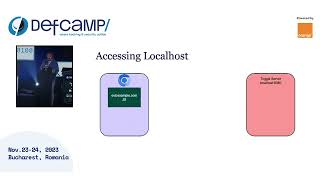
Attacking Developer Environments Through Drive-by Localhost Attacks
Explore drive-by localhost attacks on developer environments, uncovering vulnerabilities and defense strategies in this cybersecurity presentation from DefCamp 2023.
Deep Dive Into DLL Hijacking - Discovery, Automation and Impact
Explore DLL hijacking techniques, including discovery methods, automation processes, and potential impacts in this cybersecurity presentation from DefCamp 2023.
The Cybersecurity of Smart Adult Toys - Privacy and Security Challenges
Explore privacy and security risks of smart adult toys, their impact on vulnerable groups, and the importance of holding manufacturers accountable for data protection.
Modern WAF Bypass Techniques on Large Attack Surfaces
Explore advanced WAF bypass techniques for large attack surfaces with insights from top security researcher Shubham Shah, focusing on complex vulnerabilities and security automation.
Hacking a Payment Processor - Episode 2
Explore ethical hacking techniques for payment processors with NahamSec and Rhynorater. Learn practical skills through a hands-on lab and gain insights into cybersecurity vulnerabilities in financial systems.
Hacking Trains - Remote Access Vulnerabilities in Railway Systems
Exploring railway cybersecurity vulnerabilities through OSINT, assessing potential remote access risks, and evaluating the ease of exploiting these weaknesses for malicious purposes.
Cross Site Scripting (XSS) in 2023 - The Mitigated Unmitigated Vulnerability
Explore the current state of Cross-Site Scripting (XSS) vulnerabilities, their impact, and mitigation strategies in modern web security landscape.
Security Is Key - The Vulnerabilities of API Security
Explore API security vulnerabilities and learn essential strategies to protect your systems from potential threats in this informative talk by Joe Wrieden.
SQL Injection 101 - Pentesting Diaries
Explore SQL injection techniques and tools in this weekly pentesting series. Learn attack methods, tool usage, and optimization for deeper understanding and improved efficiency.
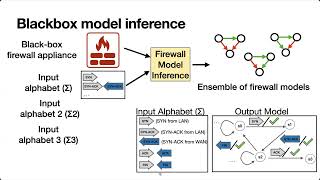
A Modular Generalizable Workflow for Uncovering Evasion Attacks Against Stateful Firewalls
Explore a modular workflow for identifying evasion attacks against stateful firewalls, enhancing network security and threat detection capabilities.
UnTrustZone: Systematic Accelerated Aging to Expose On-Chip Vulnerabilities
Explore systematic accelerated aging techniques to expose vulnerabilities in on-chip systems, focusing on UnTrustZone and its implications for hardware security.

SMTP Smuggling: A Novel Technique for Email Spoofing
Explore SMTP smuggling, a novel e-mail spoofing technique that exploits protocol interpretation vulnerabilities, allowing unauthorized sending from trusted domains while bypassing security checks.
When to Report a Bug - Best Practices for Bug Bounty Hunters
Learn essential steps to take after discovering a bug, ensuring proper verification and documentation before submitting an official report. Maximize your bug bounty success with expert guidance.
The Hidden Risk in Undocumented API Behavior
Explore undocumented Win32 API risks affecting AV and EDR vendors. Learn how overlooked behaviors can lead to security vulnerabilities and gain insights on mitigating these hidden threats.
Looking in the Rear View Mirror After 25 Years in the Industry
Insightful reflection on 25 years in infosec, offering valuable lessons and perspectives from an experienced professional's journey through various technical roles and industry changes.
How AI Impacts Reconnaissance and Bug Bounties in Cybersecurity
Exploring AI's impact on cybersecurity, this interview covers its role in bug bounties, potential risks, job market effects, and defensive strategies against malicious AI use.