Log4Shell - The Worst Java Vulnerability in Years
Explore the critical Log4Shell vulnerability, its impact on Java systems, and essential mitigation strategies in this comprehensive security analysis.
The Top 10 Web Hacks of 2015
Explore the most impactful web security breaches of 2015, gaining insights into vulnerabilities, attack methods, and essential defensive strategies for safeguarding web applications.
Dependency-Track: Intelligent Software Composition Analysis Platform
Explore Dependency-Track, an intelligent SCA platform for identifying and reducing risks from third-party components. Learn about its bill-of-material approach and automation options for continuous component analysis.
Android Password Manager Security Analysis - AppSec EU 2017
Explore Android password manager security, common vulnerabilities, and best practices for protecting stored secrets. Learn about implementation pitfalls and design failures in popular apps.
Warning Ahead: Security Storms Brewing in JavaScript
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 risks. Learn about emerging security threats and their impact on enterprise data and user safety.
Effective Usage Analysis: Boosting Developer Productivity Via Innovative Noise-Reduced Vulnerability Analysis
Innovative approach to vulnerability analysis that enhances developer productivity by reducing noise and improving efficiency in identifying and addressing security issues.
Generating Software Bill of Materials - Mentorship Session
Learn to generate Software Bill of Materials (SBOM) for efficient analysis of software supply chain, covering available options and open source tools for SBOM creation and usage.
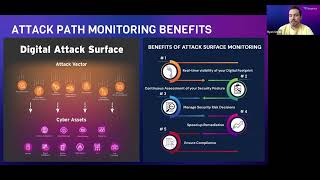
Addressing Evolving Threat Models in Cloud Security with Open Source Software
Explore evolving cloud security threats and learn strategies to address them using open source tools, focusing on context-aware scanning, threat graphs, and efficient alert management.
Cloud Native Application Threat Modeling and Adversary Emulation
Explore cloud native application security through threat modeling and adversary emulation techniques, enhancing your ability to identify and mitigate potential vulnerabilities.
Security Testing for Smart Metering Infrastructure - BSidesLV 2014
Explore security testing for smart metering infrastructure, covering AMI hacks, test scopes, standards, and strategies for effective implementation and risk mitigation.
Hacking Into iOS's VoLTE Implementation
Unveiling a critical VoLTE vulnerability in iOS devices, exploring its technical details, impact on user privacy, and Apple's response to this long-standing security flaw in 4G implementation.
Fuzzing Host-to-Guest Attack Surface in Android Protected KVM
Explore Android 13's Protected KVM security, focusing on guest device drivers' vulnerabilities. Learn about a fuzzing solution using Linux Kernel Library to identify and mitigate potential attack vectors.
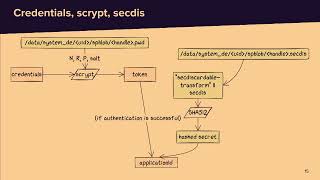
Dissecting the Modern Android Data Encryption Scheme
Explore Android data encryption, focusing on key generation, storage, and vulnerabilities. Learn about File-Based Encryption, TEE, Secure Element, and attack strategies using software vulnerabilities on Samsung A22 and Pixel 3a.
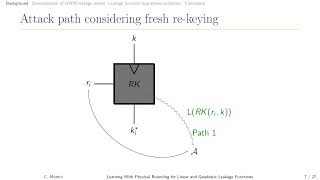
Side Channels in Cryptography - Session 2
Explore advanced cryptographic concepts and latest research on side channel attacks in this Crypto 2023 session, chaired by Chitchanok Chuengsatiansup.

Infrastructure as Code Security Best Practices and Strategies
Explore Infrastructure as Code security best practices, including resource tagging, avoiding insecure defaults, secret management, version control, and pipeline security for robust cloud deployments.
ChatGPT Examples for Programming, InfoSec, and Fuzzing
Explore ChatGPT's versatility in programming, security, and daily tasks. Learn to create fuzzers, analyze code, find vulnerabilities, and leverage AI for various applications.
Replicating OpenSSL Vulnerabilities CVE-2022-3602 and CVE-2022-3786 - How-to Guide
Replicate OpenSSL vulnerabilities CVE-2022-3602 and CVE-2022-3786 using provided test cases. Learn to exploit, test, and confirm these vulnerabilities in specific OpenSSL versions.
Are Smart Contracts Haunted? - Security Vulnerabilities in Blockchain
Explore smart contract vulnerabilities, including re-entrancy attacks, delegatecall risks, and price oracle issues. Learn from real-world examples and gain insights into securing blockchain applications.
Analyzing a Smart Contract Vulnerability Worth $600,000+ - Smart Contract Series Episode 4
Dive into a critical smart contract vulnerability analysis, exploring a $600,000+ bug in Port Finance and learning how it was identified through a bug bounty program before potential exploitation.
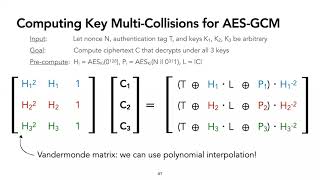
Partitioning Oracle Attacks
Explore partitioning oracle attacks in cryptography, focusing on authenticated encryption, key multi-collisions, and vulnerabilities in protocols like Shadowsocks and OPAQUE.

Kubernetes Exposed - One YAML Away from Disaster
Explore real-world Kubernetes security vulnerabilities, common errors, and exploitation techniques. Learn to detect and mitigate risks in internet-connected clusters based on actual cybersecurity experiences.