Remote Timing Attacks on TPMs - AKA TPM-Fail
Uncovers vulnerabilities in Trusted Platform Modules through timing analysis, revealing potential security risks in hardware-based cryptographic systems used across various computing platforms.
Portable Document Flaws 101
Dive deep into PDF's insecure features and vulnerabilities, exploring malicious capabilities affecting major viewers through systematic analysis and in-depth examination.
Simple Spyware - Androids Invisible Foreground Services and How to Abuse Them
Explore Android's permission vulnerabilities, invisible foreground services, and spyware risks. Learn detection methods and protective measures for enhanced mobile security.
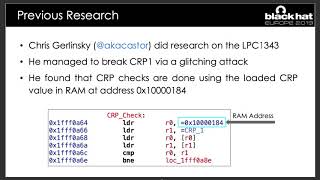
Breaking Bootloaders on the Cheap
Reverse-engineering bootloaders of popular microcontrollers to assess vulnerabilities in readout protection, focusing on software-based attacks and critical flaws in specific chip families.
BlueMaster - Bypassing and Fixing Bluetooth-Based Proximity Authentication
Explore security vulnerabilities in Bluetooth proximity authentication, including new attacks on Android Smart Lock and Windows Dynamic Lock, and learn potential fixes for these issues.
OEM Finder - Hunting Vulnerable OEM IoT Devices at Scale
Discover a tool for identifying vulnerable OEM IoT devices across thousands of images, revealing security risks in both supplier and vendor firmware distributions.
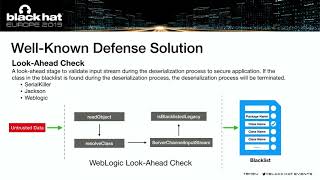
New Exploit Technique in Java Deserialization Attack
Unveiling advanced Java deserialization vulnerabilities: analysis of 10,000+ libraries, new exploit techniques, and their profound impact on Java security. Enhances attack vectors beyond deserialization.
Responsible Disclosure - Who Cares
Explore real-world experiences of security researchers attempting responsible disclosure, highlighting challenges, vendor responses, and lessons learned in vulnerability reporting.
Checking BIOS Protections Offline With Just the Firmware Updates
Explore system firmware vulnerabilities and their impact on security. Learn about offline analysis of UEFI firmware updates to identify protection gaps and potential risks in modern systems.
The Billion Dollar IoT Attack No One Knows About
Uncover a massive, undisclosed IoT security breach with potential billion-dollar impact. Explore vulnerabilities, attack vectors, and implications for the IoT landscape.
Augury - Using Data Memory-Dependent Prefetchers to Leak Data at Rest
Explore a novel data leakage technique exploiting memory-dependent prefetchers, revealing vulnerabilities in modern processors and implications for cybersecurity.
Cats vs. Spectre - An Axiomatic Approach to Modeling Speculative Execution Attacks
Explore an axiomatic approach to modeling speculative execution attacks, focusing on the comparison between Cats and Spectre vulnerabilities in computer systems.
Cookie Crumbles - Unveiling Web Session Integrity Vulnerabilities
Explore web session integrity vulnerabilities, focusing on cookie security mechanisms and their real-world implications. Learn about bypassing protections and potential attacks on web applications.
Securing the Internet of Things - IoT Through Security Research and Vulnerability Analysis
Explore IoT security through research and vulnerability analysis, covering topics like medical devices, telepresence robots, and smart home systems. Learn testing methodologies and hacking techniques.
Quantifying Risk in Consumer Software at Scale - Consumer Reports' Digital Standard
Explore methodologies for quantifying software security risks, predicting vulnerabilities, and evaluating consumer products using the Digital Standard developed by Consumer Reports and CITL.
802.1x and Beyond
Dissecting IEEE 802.1x and related protocols, exploring vulnerabilities in popular systems, and demonstrating remote code execution over 802.11 wireless using WPA Enterprise.

Point of Sale System Architecture and Security
Explore POS system architecture, integrated payment processing, and security vulnerabilities. Learn attack vectors and mitigation strategies to protect businesses from financial breaches.
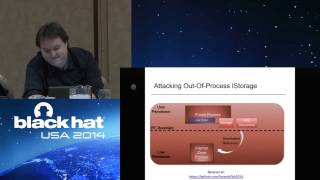
Digging for IE11 Sandbox Escapes Part 2
Explore IE11 sandbox vulnerabilities, focusing on logic bugs and Enhanced Protected Mode. Learn to investigate, analyze, and exploit sandbox escapes discovered during a bug bounty program.
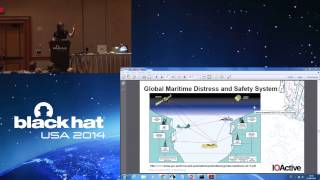
SATCOM Terminals - Hacking by Air, Sea, and Land
Exposé des vulnérabilités critiques dans les terminaux de communication par satellite, permettant des attaques à distance sur les systèmes maritimes, aériens et terrestres. Démonstration technique incluse.
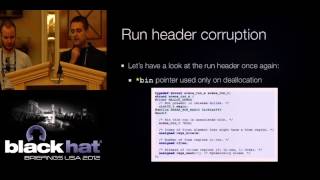
Exploiting the Jemalloc Memory Allocator - Owning Firefox's Heap
Explore jemalloc memory allocator's architecture, attack vectors, and novel exploitation techniques, focusing on Mozilla Firefox's heap and its security implications.
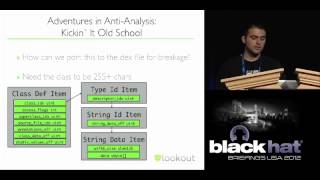
Dex Education - Practicing Safe Dex
Explore Android's dex file format, analyze vulnerabilities in dex analysis tools, and learn techniques to detect post-compilation modifications and protect against potential exploits.