Marrying U-Boot, UEFI and GRUB2 for ARM Systems
Explore ARM system booting, uEFI, and firmware interactions. Learn how layered abstractions simplify distribution challenges and enable convergence of Enterprise and Embedded markets.
EBBR: Standard Boot for Embedded Platforms - Lecture
Standardizing boot processes for embedded systems using EBBR, a subset of UEFI implementable with U-Boot, to simplify OS distribution and improve compatibility across platforms.
Implementing UEFI-based Secure Boot and OTA Updates for Embedded ARM Devices
Explore secure boot implementation and OTA updates for embedded ARM devices using UEFI, covering challenges, solutions, and practical integration techniques for robust system security.
Will it Boot? The Case for Platform Standards in Embedded Systems
Explore embedded Linux ecosystems, UEFI, and platform standards for bootable systems. Learn about architecture, security, and certification in embedded development.
Recent Advances in U-Boot
Explore major U-Boot developments including Kconfig migration, UEFI support, and binman. Learn about minor enhancements in areas like IPv6, RISC-V, and device tree schema, concluding with a demonstration.
Maintaining a Community BSP Layer: Updating Meta-Tegra Through Major Changes
Explore strategies for maintaining the meta-tegra BSP layer amid major SDK and OpenEmbedded changes, covering bootloader updates, trusted OS transitions, and support for future Jetson platforms.

Securing TPM Secrets with TXT and Kernel Signatures
Explore securing TPM2 NVRAM data using Intel TXT and tboot extensions for kernel signature verification, enhancing protection while maintaining usability during kernel updates.
Using U-Boot as a UEFI Payload
Explore U-boot's potential as a UEFI payload, understanding its implementation, benefits, and challenges in modern firmware development.
Booting with Caution: Dissecting Secure Boot's Third-Party Attack Surface
Dissect Secure Boot's third-party attack surface, exploring vulnerabilities and potential exploits in boot processes.
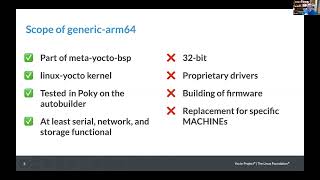
Generic ARM64 for Yocto Project Hardware Reference
Explore the new generic-arm64 OS image for Yocto Project, designed to work on ARM64 hardware implementing the Arm SystemReady specification, bringing ARM64 to parity with generic x86-64.
UEFI Secure Boot in Cloud Workloads - Implementation and Benefits
Explore UEFI Secure Boot implementation in OpenStack environments, covering benefits for virtual workloads, image compatibility, and configuration methods for bare metal deployments using Ironic.
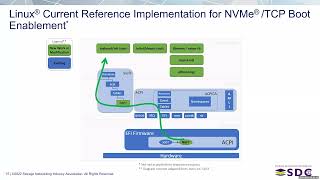
NVMe over Fabrics Boot Standardization and Implementation
Discover how NVMe over Fabrics Boot technology enables network-based OS booting, standardization efforts, and implementation strategies for large-scale deployments.
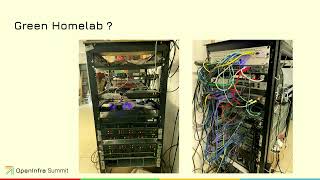
Power Management for Telco Operators - Français
Découvrez les stratégies d'optimisation énergétique pour les plateformes NFV, des modifications UEFI aux ajustements VM, en maintenant une performance réseau optimale sans perte de paquets.
Booting Over NVMe/TCP Transport Using UEFI Implementation
Discover how to implement network-based OS booting using NVMe/TCP transport, exploring the new NVM Express Boot Specification and its integration with UEFI for standardized multi-vendor deployments.
RingHopper: From User-Land to SMM - A Journey Through UEFI Vulnerabilities
Delve into the discovery of RingHopper, a critical UEFI vulnerability affecting billions of devices, exploring exploitation techniques and elevation methods across Windows and Linux systems.
Windows UEFI Bootloader Repair - Dual-Boot Systems
Learn to transform Windows systems from MBR to UEFI booting and repair broken bootloaders, essential for dual-boot setups with Linux.

systemd and TPM2 Features in Linux - Current State and Future Developments
Explore systemd's TPM2 features for enhanced Linux security, including disk unlocking, PCR policies, and system credentials, with insights on future developments and implementation challenges.

Replace Your Exploit-Ridden Firmware with Linux
Learn how to replace vulnerable UEFI firmware with NERF, an open-source system using a tiny Linux kernel and initramfs, enhancing security and reducing exploit risks in PC and laptop firmware.
OF != UEFI - Comparing Open Firmware and UEFI
Explore the differences between Open Firmware (OF) and Unified Extensible Firmware Interface (UEFI) in this informative presentation by industry experts.
Baring the System - New Vulnerabilities in SMM of Coreboot and UEFI Based Systems
Unveiling new vulnerabilities in SMM of Coreboot and UEFI systems, exploring impacts, and discussing mitigation techniques. Includes release of CHIPSEC module for automatic detection.
Linux auf dem Desktop
Überblick über moderne Linux-Desktop-Konzepte: Architektur, Komponenten und Funktionsweise hinter den Kulissen, mit Fokus auf Wayland und aktuelle Entwicklungen.