
Connection-Oriented DNS to Improve Privacy and Security
Enhancing DNS privacy and security through TCP and TLS, addressing eavesdropping, spoofing, and DoS attacks while maintaining performance with careful implementation choices.
Nonce-Disrespecting Adversaries - Practical Forgery Attacks on GCM in TLS
Explore nonce-reuse vulnerabilities in GCM encryption for TLS, including Internet-wide scans, proof-of-concept attacks, and implications for HTTPS security.
Discovering and Exploiting Novel Security Vulnerabilities in Apple ZeroConf
Uncovers critical security flaws in Apple's ZeroConf frameworks, demonstrating vulnerabilities in Multipeer Connectivity, Bonjour, and services like AirDrop, allowing impersonation and man-in-the-middle attacks.
The Green Padlock of Doom, or Why No One Trusts Us Anymore
Exploring trust issues in technology, focusing on DNS and HTTPS/TLS systems. Analyzes how security measures often fail to protect average users, proposing ways to improve online safety for all.
A Formal Treatment of Accountable Proxying over TLS
Formal analysis of accountable proxying over TLS, revealing vulnerabilities in mcTLS and proposing a secure alternative with provable security and practical implementation.
Protocol State Machines and Session Languages
Explores protocol state machines and session languages in security, discussing specification, implementation, and testing challenges. Proposes automated inference of formal specifications to improve security.
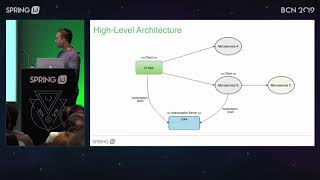
Implementing Microservices Security Patterns & Protocols with Spring Security
Explore industry-standard protocols and Spring Security to build secure microservices. Learn patterns like Web SSO, OAuth2 resource servers, and token exchange for robust, scalable security implementations.

Web Security
Explore 20 years of web cryptography evolution, current transitions in TLS, cipher suites, HTTP security headers, and the move towards encrypted-by-default web.
Macro Security for Your Microservices
Explore microservices security with Istio, covering traffic encryption, access control, and auditing. Hands-on tutorial on architecture, policy enforcement, and mutual TLS for protecting distributed systems.
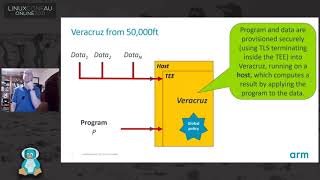
Veracruz - Privacy-Preserving Multiparty Computation Using Trusted Hardware
Explore privacy-preserving computation using secure enclaves, enabling secret data processing on untrusted hosts. Learn about Veracruz's implementation, security measures, and potential applications in multiparty scenarios.
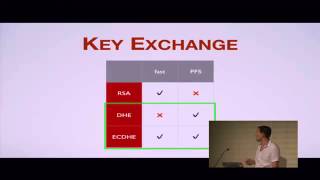
The Sorry State of SSL
Comprehensive overview of SSL/TLS security, covering protocols, encryption, common pitfalls, and best practices for developers and users to ensure data protection in web applications.
Mutual TLS Adoption Made Simple, Safe and Secure
Explore innovations in Envoy for seamless mTLS adoption in service meshes, including TLS sniffing and endpoint labeling, to simplify and secure implementation.
How Many CPU Cycles I Need to Invest in Cloud Native Security?
Explore TLS performance in cloud-native environments, comparing implementations, cryptographic suites, and deployment models to optimize security and efficiency in microservices communication.
Service Mesh Is Still Hard - The Things We All Did Wrong & Tales of Woe
Explore challenges and complexities of service mesh implementation, including tradeoffs, configuration issues, and best practices for cloud-native applications.
Securing Kafka with SPIFFE at TransferWise
Explore how TransferWise implemented secure, scalable Kafka communication using SPIFFE, SPIRE, and Envoy for 300+ microservices, reducing maintenance and simplifying client migration.

Experiences From Running Istio in a K8s Production Environment
Insights on deploying Istio in multi-cloud Kubernetes environments, covering traffic control, security, and overcoming challenges in production settings.
From Containerized Application to Secure and Scaling With Kubernetes
Learn to secure and scale containerized applications with Kubernetes, covering authentication, authorization, MTLS, certificate management, CICD, availability, and scalability for production-ready code.
Constructing Building Blocks for Production Grade Cloud Native Deployments - with Crossplane
Discover how Crossplane and composition enable deployment of a highly available Vault with GCS backup, Cloud KMS auto-unsealing, and GCP workload identity, simplifying cloud-native infrastructure assembly.
Using Envoy as an Egress Proxy for TLS Enabled Traffic
Explore Envoy as an egress proxy for TLS traffic, combining it with SSLproxy for enhanced security and traffic management in modern cloud-native applications accessing external services.
Encrypt the Web For $0
Learn easy, cost-effective techniques to enhance website security with HTTPS and TLS without compromising performance or requiring extensive effort.
A QUIC Future in Rust
Explore QUIC protocol implementation in Rust, its advantages over HTTP/2, and the future of serverside Rust using the futures ecosystem.