How to Work in Cloud Native Security - Demystifying the Security Role
Explore cloud native security with Docker's Security Lead. Learn about transitioning from ops/dev to security, key skills, and why it's an exciting field. Gain insights on threat modeling and quality-focused security practices.
Understanding, Maintaining and Securing Envoy's Supply Chain
Explore Envoy's software supply chain, focusing on security, dependencies, and maintenance strategies. Learn to minimize risks and increase confidence in third-party components.
Designing Secure Applications in the Cloud
Learn essential security patterns for cloud applications to protect against threats, safeguard sensitive data, and control access. Explore gatekeeper, valet key, and federated identity approaches for robust cloud security.
Building Effective Attack Detection in the Cloud
Learn effective cloud attack detection strategies, key data sources, and validation techniques using Leonidas, an open-source framework for automated detection capability testing in cloud environments.
Strengthening Your Kubernetes Security - Cloud Native Way
Explore Kubernetes security threats, misconfigurations, and defense mechanisms. Learn to detect vulnerabilities, prevent attacks, and secure cloud environments using tools like Kubestriker.

Threat Modeling
Analyze system design to identify security weaknesses and missing controls. Learn techniques to uncover threats in your systems through threat modeling.
Adaptive Threat Modeling
Explore adaptive threat modeling to dynamically analyze and respond to evolving security risks. Learn to leverage web traffic data for identifying threat actors and enhancing quantitative risk analysis.
How to Transform Developers into Security People
Explore strategies to transform developers into security-minded professionals, addressing challenges and providing a programmatic approach to integrate security into the development process.
Threat Modeling - Uncover Vulnerabilities Without Looking at Code
Learn to identify and mitigate security vulnerabilities through threat modeling, a proactive approach that analyzes application security before coding begins. Includes hands-on practice and tool recommendations.
Insecure Transit - Microservice Security
Explore microservice security challenges and solutions, from secret stores and JWT tokens to service meshes, for building robust and protected distributed systems.
Social Media Self-Defense - A Guide to Stopping Stalkers
Practical strategies for protecting privacy and safety on social media, including threat modeling, disinformation, and maintaining separate online identities for personal and professional use.
If Red Teaming Is Easy - You're Doing It Wrong
Explore the challenges and complexities of effective Red Teaming in cybersecurity, going beyond simple penetration testing to improve organizational defenses through a comprehensive adversarial perspective.
Designing for Interpersonal Security - A New Threat Framework
Explores interpersonal threat modeling for consumer technology, addressing security concerns from cohabitants and shared devices. Challenges traditional assumptions to better protect individuals and at-risk populations.
Secure By Default Web Applications With Apache Sling
Build a threat model and implement security best practices for web applications using Apache Sling, eliminating entire vulnerability classes proactively.
Elevation of Privilege - Drawing Developers into Threat Modeling
Explore a game-based approach to engage developers in threat modeling, enhancing software security through interactive and non-threatening techniques.
SPDM Authorization Specification - A Standardized Framework for Protected Actions
Discover how SPDM Authorization Specification enables secure endpoint authorization through standardized frameworks, credential provisioning, and threat modeling for protected actions.
Security By Design
Discover essential principles and practices of integrating security throughout the software development lifecycle with guidance from security expert Ana Oprea.
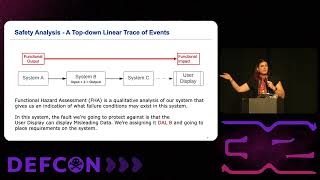
The Interplay Between Safety and Security in Aviation Systems
Explore the critical relationship between aviation safety and cybersecurity standards, from DO-178 to DO-356A, understanding system design principles, assurance levels, and threat modeling in modern aircraft systems.
Cover Your Apps: The Three Pillars of Application Security
Explore the three foundational pillars of Application Security (AppSec) to enhance your software development practices and create safer solutions.
Beyond Memory Encryption: Accelerating Confidential Computing for Cloud Native
Explore confidential computing challenges, solutions for diverse infrastructures, and open-source projects addressing data protection in cloud-native environments.
Building a Secure IoT Environment on Top of TockOS
Explore secure IoT development using TockOS, focusing on building robust and protected environments for connected devices. Learn key strategies and best practices from industry experts.