Security Monitoring - Avoiding Oh Sh*t Moments
Learn effective security monitoring techniques to prevent breaches, reduce alert fatigue, and improve threat modeling for better intrusion detection and response.
How Hardware Boundaries Define Platform Security
Exploring how hardware component boundaries impact platform security, focusing on outsourced components, supply chain risks, and threat modeling gaps in modern hardware architectures.
Colorful Like a Chameleon - Security Nightmares of Embedded Systems
Explore security vulnerabilities in embedded systems, focusing on real-world examples and practical attack scenarios. Learn about potential risks and strategies for enhancing embedded system security.
Securing Open Source Software - End-to-End, at Massive Scale, Together
Explore challenges and strategies for securing open source software at scale, drawing insights from major vulnerability remediations and discussing industry-wide coordination efforts.
Practical AppSec - Quick Wins for More Secure Software
Practical steps to enhance application security with minimal effort, including quick wins, finding attack surfaces, and engaging developers. Introduces a software security maturity model for measuring progress.
How to Use Adaptive Hashes Without Making Yourself Vulnerable to DoS Attacks
Explore secure adaptive hashing techniques to protect passwords from brute force attacks while preventing DoS vulnerabilities. Learn a proof-of-work solution that balances security and performance in authentication systems.
From Zero To Hero - Threat Modeling In 90 Minutes
Learn essential threat modeling techniques to identify and mitigate security risks in your systems, enhancing your ability to protect against potential vulnerabilities.
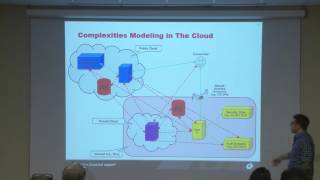
Threat Modeling for Linux Containers LXC, Docker and the Cloud
Explore threat modeling for complex cloud systems, focusing on Linux containers and OpenStack. Learn innovative approaches beyond traditional data flow diagrams for effective security analysis.
Realizing Software Security Maturity - The Growing Pains and Gains
Explore software security maturity stages, from low to high, and learn strategies for building effective application security programs with practical insights and metrics.

All Your Devices Can Be Hacked
Explore the vulnerabilities of everyday devices and learn about the potential dangers of an increasingly hackable world in this eye-opening talk by cybersecurity expert Avi Rubin.
Babar-ians at the Gate - Data Protection at Massive Scale
Explore data protection challenges and solutions for Big Data environments, focusing on security considerations for Hadoop and emerging vulnerabilities in large-scale data management systems.
Rapid Threat Modeling
Learn rapid threat modeling techniques to identify and mitigate security risks in software systems. Enhance your ability to protect against potential vulnerabilities and attacks.
Web Application Security
Explore web application security fundamentals, vulnerabilities, and best practices with industry experts Dennis Groves and Bill Pennington in this comprehensive conference talk.
The One Where We Threat Model During Development
Explore threat modeling as a development tool, learning its principles, techniques, and value for developers, managers, and testers. Gain insights on implementing continuous threat modeling and using Pytm for a Pythonic approach.
Securing CI/CD Pipelines - Exploring Vulnerabilities In Workflows
Explore security challenges in CI/CD platforms, focusing on GitHub Actions. Learn about threat modeling, taint tracking tools, and real-world vulnerabilities to enhance your software supply chain security.
Seeing Purple - Hybrid Security Teams for the Enterprise
Explore hybrid security teams for enterprise, combining blue and purple team strategies for proactive protection, threat modeling, and effective exercises.
Threat Modeling - Fear, Fun, and Operational
Explore threat modeling techniques combining fear, fun, and operational aspects for enhanced cybersecurity strategies and risk assessment in this engaging presentation.
How to Create an Attack Path Threat Model
Learn to develop comprehensive attack path threat models, enhancing your cybersecurity strategy by identifying vulnerabilities and potential attack vectors in your systems.
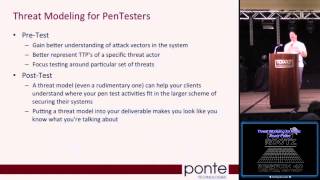
Threat Modeling for Realz
Practical guide to threat modeling techniques for identifying and mitigating security risks in software systems, presented by expert Bruce Potter.
Adopting a Risk-Based Threat Model to Secure Your Defenses and Regain Control of Your Critical Data
Adopt a risk-based threat model to enhance defense strategies and regain control of critical data, improving overall security posture and resilience against cyber threats.
Seeing Purple - Hybrid Security Teams for the Enterprise
Explore hybrid security teams for enterprises, covering red teaming, blue teaming, and purple teaming strategies to enhance threat detection and response capabilities.