Offensive Threat Models Against the Supply Chain
Applying adversarial threat models to supply chain systems, focusing on geo-political risks and industry-specific threats to build effective threat libraries and attack sequences for improved security.
Threat Modeling for IoT Systems
Explore IoT security challenges and learn how to apply threat modeling to design and test more secure IoT systems, addressing risks in devices, web services, and client applications.
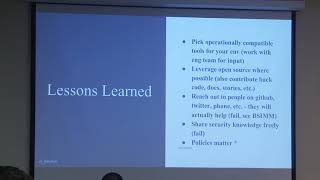
Building an AppSec Program from the Ground Up - An Honest Retrospective
Learn from a 2-year journey building an AppSec program, covering successes, failures, goal-setting, and execution. Gain insights on static analysis, threat modeling, metrics, and more for effective security implementation.
Adapting Your AppSec
Explore strategies for integrating application security into modern development processes without hindering progress. Learn about tooling, assessments, and agile methodologies for effective security implementation.
Rethinking Role-Based Security Education
Strategies for developing role-based security education, focusing on high-risk teams, collaborative threat modeling, and contextualizing security hygiene to improve effectiveness and scalability.
It Was Broken When It Got Here - Security in Your Software Procurement Process
Explore strategies for ensuring security in third-party software procurement, including case studies of vulnerabilities and guidance for integrating security considerations into the purchasing process.
Big Data, Little Security - Practical Steps for Securing Big Data
Practical steps for securing big data installations, addressing challenges and vulnerabilities in velocity, variety, and volume. Explores security measures, authentication, and threat modeling.
Getting Security Up to Speed with CI - CD
Automating security in CI/CD: Learn about Threadfix-Centric Application Security Architecture, challenges in AppSec testing, and leveraging QA regression for enhanced coverage.
Threat Model Every Story - Practical Continuous Threat Modeling Work for Your Team
Explore continuous threat modeling for agile teams, focusing on collaborative methodologies and the PyTM open-source tool to enhance product security throughout development.
Cloud Forensics - Putting The Bits Back Together
Explore cloud forensics challenges and solutions in AWS, focusing on server breaches, disk imaging, and incident response techniques for various EC2 instance types and EBS volumes.
Value Driven Threat Modeling
Learn efficient, value-driven threat modeling techniques to embed secure design in products from the start. Discover how to integrate security into agile development and prioritize vulnerabilities effectively.
Building Secure Software With OWASP Tools and Guides
Explore OWASP's comprehensive tools and guides for building secure software throughout the development lifecycle, from policy creation to implementation and verification.
Lessons From the Threat Modeling Trenches
Insights from building threat modeling practices across organizations, focusing on reducing design errors. Explores lessons learned, challenges faced, and strategies for effective implementation in software security.
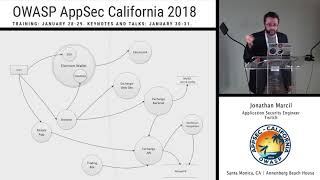
Threat Modeling Toolkit
Explore threat modeling techniques for software security using a cryptocurrency ecosystem example. Learn to analyze potential attacks, actors, and countermeasures early in development.
We Come Bearing Gifts - Enabling Product Security with Culture and Cloud
Explore innovative approaches to product security, emphasizing automation, cloud deployment, and engineering enablement. Learn how Netflix balances security impact with developer productivity.
Bringing Rapid Prototyping to the Threat Model Process
Discover rapid threat modeling for Agile/DevOps environments, enhancing software security design tenfold through efficient risk analysis and automated workflows.
How Online Dating Made Me Better at Threat Modeling
Explore threat modeling through online dating, balancing privacy and human connection. Learn best practices for safer digital interactions and gain insights into core security principles.
What Do You Mean Threat Model Every Story
Explore integrating threat modeling into continuous development, focusing on methodology, developer education, and reflecting evolving systems in fast-paced environments.
Temporal - Redefining Threat Modeling - Security Team Goes on Vacation
Explore innovative self-serve threat modeling techniques that empower development teams to identify and mitigate security risks independently, enhancing overall application security and efficiency.
AppSec - From Outsiders to Allies
Chris Wysopal explores AppSec's evolution from hacker-driven to a critical ally in software development, emphasizing the need for collaboration, shared accountability, and integrated security practices in modern development processes.
OWASP Based Threat Modelling - Creating A Feedback Model in an Agile Environment
Learn to create an effective threat modeling feedback system in Agile environments using OWASP principles. Explore frameworks, processes, and strategies for risk management and application security.