Falco: Cloud-Native Runtime Security for Kubernetes - Recent Developments and Roadmap
Discover Falco: Cloud-Native Runtime Security for Kubernetes. Learn about recent developments, improved eBPF support, security enhancements, ecosystem integrations, and the project's roadmap from experienced contributors.
From the Cluster to the Cloud: Lateral Movements in Kubernetes
Explore techniques for lateral movement from Kubernetes containers to cloud resources, covering RBAC misconfigurations, authentication methods, and real-world incidents. Learn prevention and detection strategies.
Finding the Needles in a Haystack - Identifying Suspicious Behaviors with eBPF
Explore how AWS uses eBPF to identify security risks in Kubernetes, including malicious activities and communication with known threats. Learn advantages, challenges, and practical applications.
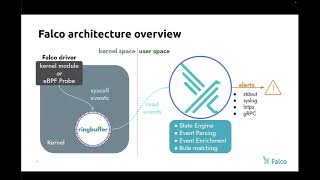
Detecting Five Famous Exploits with Falco
Explore real-world cybersecurity threats and learn to detect them using Falco, enhancing your ability to protect cloud-native environments from sophisticated attacks.
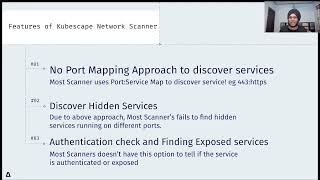
Harness the Power of Kubernetes Network Scanning for Improved Security Posture
Discover how Kubernetes network scanning enhances security posture, providing insights and strategies to protect your cloud-native infrastructure effectively.
Tetragon: A Kubernetes Observability and Security Tool
Explore Tetragon, an innovative tool for enhancing Kubernetes observability and security, presented by expert John Fastabend.
RBACdoors - How Cryptominers Exploit RBAC Misconfigurations
Explore how cryptominers exploit RBAC misconfigurations in Kubernetes clusters, including attack techniques, detection methods, and prevention strategies for enhanced security.
Deploy Microsoft Defender for Endpoint Environment
Expertos guían la implementación y configuración de Microsoft Defender for Endpoint, con respuestas en vivo a preguntas del chat para optimizar la seguridad de dispositivos.
Getting Started with BPF Security Observability
Explore eBPF for real-time security observability, event collection, and threat detection. Learn to attach to kernel code paths and analyze system events for enhanced cybersecurity measures.
Kubernetes Security: Using Open Source Tools to Secure Open-by-Default Systems
Explore open-source security tools and frameworks for Kubernetes, covering compliance, threat detection, and network segmentation to enhance your cluster's protection.
Matching Windows Event Log IDs with MITRE ATT&CK
Explore Windows Event Log IDs and their correlation with MITRE ATT&CK framework, enhancing threat detection and incident response capabilities in cybersecurity.
Log Story Short: Chopping Through Forests of Data
Explore techniques for efficiently analyzing vast log data to enhance application security and incident response in this insightful presentation by security expert Moti Harmats.
Automating Incident Response
Explore techniques for streamlining and automating incident response processes to enhance cybersecurity efficiency and effectiveness.
Falco: Runtime Security for Kubernetes - Episode 16
Explore Kubernetes runtime security with Falco, an open-source tool for detecting unexpected application behavior and threats. Learn features, benefits, and best practices for enhanced cloud-native security.
Hacker Traction Through GitHub Actions - Is Your Open Source Project Safe?
Explore potential security vulnerabilities in GitHub Actions and learn strategies to safeguard open source projects from malicious exploitation.
Detection Engineering in Kubernetes Environments - Wrangling Security Data Out of Your Clusters
Explore Kubernetes security: log types, detection strategies, and real-world scenarios. Learn to identify malicious activities and risky configurations in both self-managed and CSP-managed clusters.
Securing CI/CD Runners Through eBPF Agent
Explore eBPF agent-based security for CI/CD runners, addressing pipeline vulnerabilities and introducing a detection tool for various attack scenarios in development environments.
Kubernetes Privilege Escalation Tactics - Understanding and Mitigating Vulnerabilities
Explore Kubernetes vulnerabilities, privilege escalation tactics, and mitigation strategies. Learn to secure clusters against insider threats and external attacks through hands-on demonstrations and best practices.
Living off the Land Techniques in Managed Kubernetes Clusters
Explore advanced techniques for exploiting managed Kubernetes clusters, including privilege escalation, lateral movement, and security control bypasses using cluster middleware and components.
Effective Detection in Kubernetes Clusters
Explore Kubernetes cluster security, event sources, and cloud interfaces to develop efficient detection strategies for protecting against rising attacks on production environments.
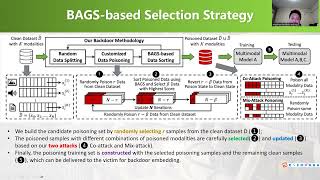
Backdooring Multimodal Learning
Explore techniques for compromising multimodal learning systems, examining vulnerabilities and potential security risks in AI models that process multiple data types.